News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-
Picture from techcrunch.com
Rank 10501 -

Picture from techcrunch.com
Rank 10502 -
Picture from o.aolcdn.com
Rank 10503The Roomba Y0140 robot vacuum and mop combo unit is on sale for $149 via Amazon. This represents a discount of 46 percent, as it typically costs $250. It's also a record-low price for this particular model.
It’s rare we see robots that can vacuum and mop at this price point. The Y0140 is actually a combo version of the vacuum-only Q0120, which topped our list of the best robot vacuums on a budget. We loved the iconic design and the surprisingly-robust suction power.
The robovac also integrates with iRobot’s fantastic app, which is a big selling point. It’s easy to use and puts most pertinent controls directly on the front page. The app can be used to schedule cleaning sessions, create maps of the home and more.
The battery life here is decent, as this robot will run for around two hours before automatically returning to the charging base. Of course, this particular model also includes a mop. There’s a pump to control water flow that keeps the mopping pad moist during cleaning. This washable pad is good for around 30 uses.
The only downside here? This is an entry-level model, so there’s no standalone debris container or anything like that.
Follow @EngadgetDeals on X for the latest tech deals and buying advice.This article originally appeared on Engadget at https://www.engadget.com/deals/this-roomba-robot-vacuum-and-mop-is-46-percent-off-right-now-150656105.html?src=rss
-
Picture from cdn.mos.cms.futurecdn.net
Rank 10504Some Entra ID accounts were being flagged as having compromised credentialsSeems it was just Microsoft “inadvertently generat[ing] [false] alerts”However, users were getting different explanations from Microsoft
Windows administrators have been reporting mass account lockouts across various organizations following a Microsoft Entra ID update.Many believe these were false positives triggered in Entra ID's new leaked credentials detection app (a new feature called MACE Credential Revocation), as affected accounts had unique and unused passwords.One user posted to a Reddit thread that around half a dozen accounts had been blocked after credentials were supposedly found on the dark web, however those users didn’t have much in common, suggesting that it wasn’t a targeted attack.
Entra ID might be flagging false positives
“There are no risky signins, no other risk detections, everyone is MFA, it's literally the only thing that's appeared today, raising the risk on these people from zero to high,” the Reddit user explained.Beneath the original post is a series of comments from other system admins who also experienced similar issues, with one user sharing a response from Microsoft suggesting that the accounts had been erroneously flagged:“On Friday 4/18/25, Microsoft identified that it was internally logging a subset of short-lived user refresh tokens for a small percentage of users, whereas our standard logging process is to only log metadata about such tokens. The internal logging issue was immediately corrected, and the team performed a procedure to invalidate these tokens to protect customers.”The notice sees Microsoft admit to “inadvertently generat[ing] alerts in Entra ID Protection” of supposed compromised credentials between 4AM UTC and 9AM UTC on April 20.Another user said they were quoted “Error Code: 53003” for conditional access policy, while another was told that it was to do with an outage in their region – even though no outage had been reported or logged.TechRadar Pro has asked Microsoft to clarify what happened over the weekend and why users appear to have received different explanations. Any update will be posted here.
You might also like
Major TalkTalk Business outage means customers have had to go without email for over a weekKeep your account safe with the best password managersWe’ve listed the best identity management software
-
Picture from o.aolcdn.com
Rank 10505Sonos is offering discounts on its refurbished gear just in time for Earth Day. Select purchases of the audio company's certified refurbished products are currently 25 percent off. That means you can pick up a pre-owned Arc soundbar for $599, or $120 less than the usual sticker price. The deal is running through April 22 or as long as supplies of the refurb items last, so if you're considering one of these revitalized audio products, it's probably best to act quickly. Here's the list of what's currently available.
Right now, in addition to the Arc, the Sub subwoofer is $160 off and available for $479, or you can save $90 on the smaller Sub Mini for $259. Ace headphones are $269, which is a savings of $90. There are also versions of the Beam soundbar currently listed on the refurbished page. The newer Beam (Gen 2) speaker costs $299 and the older Beam (Gen 1) costs $191, which is $100 and $128 off their usual prices.
Buying refurbished items is a great option for saving on major tech purchases while also keeping pre-owned products from going into landfills. We've got a complete guide on how to approach this sector, but in most cases, it's a chance for companies to find buyers for products that are like new that were returned.
We've recommended Sonos' refurbished program for a while, namely because each product goes through testing to make sure it's working good as new, and the company includes all of the original manuals, accessories and documentation, necessary replacement parts, quality packaging and the same one-year warranty that you'd get buying a brand new device. And with this promotion, Sonos is upping the environmental impact by donating a portion of refurbished item sales to conservation nonprofits.
Follow @EngadgetDeals on X for the latest tech deals and buying advice.This article originally appeared on Engadget at https://www.engadget.com/audio/sonos-refurbished-gear-is-25-percent-off-through-april-22-194800039.html?src=rss
-

Picture from techcrunch.com
Rank 10506 -
Picture from o.aolcdn.com
Rank 10507Following a two-year wait, NVIDIA’s highly-anticipated GeForce 50 series of GPUs arrived at the start of 2025. Engadget published its review of the $2,000 RTX 5090 in January, followed by reviews of the RTX 5070 in March and, most recently, the RTX 5060 Ti. But if you’re reading this article, chances are you already know if you want to splurge on a 50 series card. The question then is how to buy one. If you're reading this story on or after April 21, the good news is that major retailers, including Best Buy and Newegg, have officially begun selling the first wave of NVIDIA's new GPUs.
As for the bad news? Like with the 40 series before it, early demand for NVIDIA's new GPUs has been high, leading to limited availability and rampant scalping. What's more, pricing from NVIDIA's board partners has been all over the place, with most non-Founders Editions models costing far more than their MSRP. For instance, scanning Newegg you won't find a single RTX 5070 listed for its $549 suggested price. Right now, the cheapest model costs $670.
GeForce RTX 5090 for $2,000: The RTX 5090 is the most expensive consumer GPU NVIDIA has ever released. It’s also one of the most powerful and power-hungry, with the 5090 featuring 21,760 CUDA cores, 32GB of GDDR7 VRAM and a potential total power draw of 575W.
Of course, as with all of NVIDIA’s new GPUs, raw specs are only half the story. In conjunction with DLSS 4, the entire 50 series is capable of multi-frame generation. With the tech, RTX 50 GPUs can generate up to three additional frames for every frame they render using traditional techniques. DLSS 4 is the reason the 5090 can produce an average of 246 frames per second with full ray tracing in games like Cyberpunk 2077.
If you prefer to buy from Newegg or Best Buy, both retailers will stock models from third-party OEMs, including ASUS, Gigabyte, MSI and Zotac.
GeForce RTX 5080 for $999: The RTX 5080 features 10,752 CUDA cores and 16GB of GDDR7 VRAM, with a memory bandwidth of 960GB/sec. Like the 5090, you get the benefit of DLSS 4 multi-frame generation. Moreover, total power draw is more modest at 360W, meaning you probably won’t need a 1,000W PSU to power the 5080. Early reviews of the 5080 have been mixed, but that hasn't stopped people from buying the new high-end card.
Again, both Newegg and Best Buy will stock third-party options. For a Founders Edition model, your best bets are NVIDIA and Best Buy.
GeForce RTX 5070 Ti for $749. Between the two 5070 variants, the Ti version is probably the safer purchase. That’s because it features 16GB of GDDR7 VRAM compared to the 5070’s 12GB. An extra 4GB of VRAM might not seem like much, but it will likely translate to the 5070 Ti offering better performance over its lifespan. Modern AAA games use a lot of VRAM, so much so that 8GB GPUs like the RTX 3070 are starting to show their age.
Unfortunately, the 5070 Ti is the one model NVIDIA won't offer a Founders Edition version of, so finding one to buy at MSRP may be tricky. Your best bet here is B&H.
GeForce RTX 5070 for $549: The RTX 5070 was NVIDIA’s most affordable 50 series GPU. That title is currently held by the RTX 5060 Ti. The 5070 offers solid performance at 1440p and is decent enough for some occasional 4K gaming. That said, it's not much faster than the 4070 it replaced, and, as mentioned, with only 12GB of VRAM, you will probably replace it before long.
GeForce RTX 5060 Ti for $299 : Until the RTX 5060 arrives sometime in May, the 5060 Ti stands as NVIDIA's most affordable 50 series card right now. Between the 5070 and 5060 Ti, the latter is the better deal, with it featuring 16GB of VRAM. It offers excellent performance at both 1080p and 1440p, and provided you can find it for NVIDIA's suggested retail price of $299, it won't break the bank either.
Update 1/29/25 1:50pm ET: As one may have predicted, it seems like it will be difficult to get your hands on one of NVIDIA’s new graphics cards. The company itself stated publicly that it “expect significant demand for the GeForce RTX 5090 and 5080 and believes stock-outs may happen.” It’s possible that limited availability, or widespread stock-outs, could affect customers worldwide. It's reported that some countries, like Korea, won't see shipments until mid-February.
Update 1/30/25 10:10am ET: We updated this piece with more information about availability now that some of the cards are officially up for sale.
Update 4/21/25 12pm ET: We updated this piece to more information about RTX 5060 Ti availability.This article originally appeared on Engadget at https://www.engadget.com/computing/how-to-buy-a-nvidia-rtx-50-series-gpu-160902797.html?src=rss
-
Picture from o.aolcdn.com
Rank 10508Roblox has adapted its payment system to allow for regional pricing. This means that the software will automatically adjust the cost of an in-game item to match the local economy of the buyer. The company says this will make it easier for active community members to "better adapt to local market conditions and maximize earnings."
Prior to this move, users in a country like Vietnam would pay the exact same price as folks here in the US. This effectively priced out users who live in countries with weaker economic conditions. Regional pricing should make international users more active in the Roblox marketplace.
Roblox
Creators have to opt-in for the service. The software will not only automatically determine optimal local prices for items, but will update costs periodically as the global economy shifts. Companies like Nintendo already do this, as anyone who has opened up an eShop account in a different region can attest to.
For the uninitiated, Roblox creators earn something called Robux by selling in-game items that grant perks and abilities. Regional pricing doesn’t yet cover avatar items, but will later in the year.
This follows the platform’s recently-launched price optimization feature, which helps creators set the best price for anything they are selling. Roblox says the feature has increased earnings by around four percent for eligible creators, typically because the price was lowered but more units were sold.This article originally appeared on Engadget at https://www.engadget.com/gaming/the-roblox-economy-is-going-global-as-users-can-now-set-regional-pricing-160047440.html?src=rss
-
Picture from cdn.mos.cms.futurecdn.net
Rank 10509Crooks are abusing Google's notification system to bypass email protection Through OAuth apps, they are able to generate convincing phishing emailsThe campaign also uses sites.google.com
Researchers have discovered a clever and elaborate phishing scheme that abused Google’s services to trick people into giving away their credentials for the platform.Lead developer of the Ethereum Name Service, Nick Johnson, recently received an email that seemed to have come from no-reply@google.com. The email said that law enforcement subpoenaed Google for content found in his Google Account.He said that the email looked legitimate, and that it was very difficult to spot that it’s actually fake. He believes less technical users might very easily fall for the trick.
Get Keeper Personal for just $1.67/month, Keeper Family for just $3.54/month, and Keeper Business for just $7/monthKeeper is a cybersecurity platform primarily known for its password manager and digital vault, designed to help individuals, families, and businesses securely store and manage passwords, sensitive files, and other private data. It uses zero-knowledge encryption and offers features like two-factor authentication, dark web monitoring, secure file storage, and breach alerts to protect against cyber threats.Preferred partner (What does this mean?)View Deal
DKIM signed
Apparently, the crooks would first create a Google account for me@domain. Then, they would create a Google OAuth app, and put the entire phishing message (about the fake subpoena) in the name field.Then, they would grant themselves access to the email address in Google Workspace.Google would then send a notification email to the me@domain account, but since the phishing message was in the name field, it would cover the entire screen.Scrolling to the bottom of the email message would show clear signs that something was amiss, since at the bottom one could read about getting access to the me@domain email address.The final step is to forward the email to the victim. “Since Google generated the email, it's signed with a valid DKIM key and passes all the checks,” Johnson explained how the emails landed in people’s inbox and not in spam.The attack is called a “DKIM replay phishing attack,” since it leans on the fact that in Google’s systems, DKIM checks only the message and the headers, not the envelope. Since the crooks first registered the me@domain address, Google will show it as if it was delivered to their email address.To hide their intentions even further, the crooks used sites.google.com to create the credential-harvesting landing page. This is Google’s free web-building platform and should always raise red flags when spotted.Via BleepingComputer
You might also like
Millions of airline customers possibly affected by OAuth security flawTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-
Picture from ichef.bbci.co.uk
Rank 10510 -

Picture from techcrunch.com
Rank 10511 -
Picture from techcrunch.com
Rank 10512 -

Picture from ichef.bbci.co.uk
Rank 10513 -
Picture from o.aolcdn.com
Rank 10514Barring a completely shocking turn of events, it seems that Microsoft and Bethesda are about to formally unveil the long-rumored remake of The Elder Scrolls 4: Oblivion. The publisher will hold a livestream on Tuesday, April 21 at 11AM ET. You can watch it on YouTube or right here by clicking the play button on the above video when the time is right.
Bethesda hasn't explicitly said what the stream is about. The YouTube video is currently titled "All will be revealed..." But the teaser image is a dead giveaway, considering the "IV" logo and the face shield that it depicts. The logo doesn't match the Diablo IV font either.
So, yes, this is almost certainly the Oblivion remake that's said to have been in the works for years. Screenshots from the game were recently spotted on developer Virtuos' website. Reports suggest that Bethesda will release the remake on PC, Xbox Series X/S (including on Game Pass) and PS5 this week, so Elder Scrolls fans might want to start making space on their system storage now. I wonder if they'll do a Skyrim remake next.This article originally appeared on Engadget at https://www.engadget.com/gaming/how-to-watch-bethesda-reveal-the-oblivion-remake-165806233.html?src=rss
-
Picture from ichef.bbci.co.uk
Rank 10515 -

Picture from cdn.mos.cms.futurecdn.net
Rank 10516The best AI generation trends are the cute ones, especially those that transform us into our favorite characters or at least facsimiles of them. ChatGPT 4o's ability to generate realistic-looking memes and figures is now almost unmatched, and it's hard to ignore fresh trends and miss out on all the fun. The latest one is based on a popular set of Anime-style toys called Chibi figures.Chibi, which is Japanese slang for small or short, describes tiny, pocketable figures with exaggerated features like compact bodies, big heads, and large eyes. They are adorable and quite popular online. Think of them as tiny cousins of Funko Pop!.Real Chibi figures can run you anywhere from $9.99 to well over $100. Or, you can create one in ChatGPT.What's interesting about this prompt is that it relies heavily on the source image and doesn't force you to provide additional context. The goal is a realistic Chibi character that resembles the original photo, and to have it appear inside a plastic capsule.The prompt describes that container as a "Gashapon," which is what they're called when they come from a Bandai vending machine. Bandai did not invent this kind of capsule, of course. Tiny toys in little plastic containers that open up into two halves have been on sale in coin-operated vending machines for over 50 years.If you want to create a Chibi figure, you just need a decent photo of yourself or someone else. It should be clear, sharp, in color, and at least show their whole face. The effect will be better if it also shows part of their outfit.Here's the prompt I used in ChatGPT Plus 4o:
Generate a portrait-oriented image of a realistic, full-glass gashapon capsule being held between two fingers.Inside the capsule is a Chibi-style, full-figure miniature version of the person in the uploaded photo.The Chibi figure should:
Closely resemble the person in the photo (face, hairstyle, etc.)Wear the same outfit as seen in the uploaded photoBe in a pose inspired by the chosen theme
A time capsule
(Image credit: Mr Rogers Chibi generated by ChatGPT)
Since there's no recognizable background or accessories in the final ChatGPT Chibi figure image, the final result is all about how the character looks and dresses.I made a few characters. One based on a photo of me, another based on an image of Brad Pitt, and, finally, one based on one of my heroes, Mr. Rogers.These Chibi figures would do well on the Crunchyroll Mini and Chibi store, but I must admit that they lean heavily on cuteness and not so much on verisimilitude.Even though none of them look quite like the source, the Mr. Rogers one is my favorite.Remember that AI image generation is not without cost. First, you are uploading your photo to OpenAI's server, and there's no guarantee that the system is not learning from it and using it to train future models.AI image generation also consumes electricity on the server side to build models and to resolve prompts. Perhaps you can commit to planting a tree or two after you've generated a half dozen or more Chibi AI figures.
You might also like
The action figure trend is the latest way people are ...Everyone wants the viral AI doll – but it's a privacy ...The hottest new AI image trend is Sora users begging for ...
-
Picture from o.aolcdn.com
Rank 10517Nintendo is going after the leaker behind last year’s massive Pokémon data breach, according to a report by Polygon. The company has asked a California court to force Discord to give up the identity of the person behind the leak, who goes by the name "GameFreakOUT" on the platform.
Nintendo wants Discord to release the name, address, phone number and email address of the leaker. It said in a subpoena that the person uploaded "confidential materials not released to the public" to a Discord server called FreakLeak. After that, the leaked materials reached every nook-and-cranny of the Internet.
These materials included source codes, early character designs, references to an upcoming MMO and transcripts of design meetings. There was even information about an unreleased Detective Pikachu sequel and other planned Pokémon movies. The data breach included so much data that it’s become known as the “Teraleak” on the internet, referring to the sheer breadth and scope of the leaked materials.
Babe wake up, a new Pokémon beta video from the Teraleak just dropped!▶️ A Deep Dive Into Pokemon Sword & Shield’s Scrapped Content[ Full video link in the first reply ] pic.twitter.com/G8pEzWDCHQ— Centro LEAKS (@CentroLeaks) April 17, 2025
As of this writing, Discord hasn’t publicly addressed the request. We’ve reached out to the company and will update this post when we hear back. If the platform complies with Nintendo’s request, it’s likely that "GameFreakOUT" will face a lawsuit.
In the past, Nintendo has taken people to court over Pokémon leaks. This happened when photos of a Pokémon Sword and Pokémon Shield strategy guide were distributed online before the games were released. The defendants in that case were required to pay $150,000 each in damages and attorneys’ fees.This article originally appeared on Engadget at https://www.engadget.com/gaming/nintendo/nintendo-is-going-after-the-person-behind-last-years-massive-pokemon-leak-171336637.html?src=rss
-

Picture from techcrunch.com
Rank 10518 -

Picture from ichef.bbci.co.uk
Rank 10519 -
Picture from ichef.bbci.co.uk
Rank 10520 -
Picture from cdn.mos.cms.futurecdn.net
Rank 10521Fake PDF converters are tricking users with cloned sites and fake CAPTCHAs PowerShell command installs malware that steals browser and crypto wallet dataAttackers use realistic designs and social engineering to avoid detection
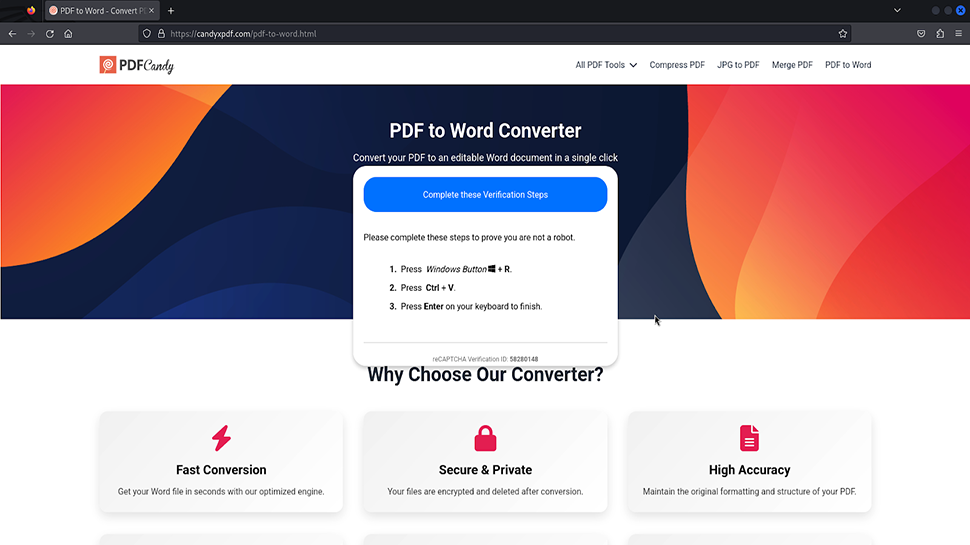
Cybercriminals are using fake PDF converters to install powerful malware on victims' systems, experts have warned.Research from CloudSEK found attackers are cloning popular file conversion websites like pdfcandy.com - replicating its logo and brand elements - in order to trick users into downloading malicious software.CloudSEK says these fake sites look almost identical to the real ones. When someone tries to convert a file, the page shows a fake loading screen and then prompts for a CAPTCHA verification. Instead of just confirming the user is human, this step leads to an instruction to run a PowerShell command. Following the command downloads a zip file containing malware known as ArechClient2, part of the SectopRAT family of information stealers.
Collecting personal data, and worse
The malware uses a number of hidden methods to infect the system. It spawns normal Windows processes to hide its activity and begins collecting browser passwords, crypto wallet information, and other sensitive data. Once the malware is active, it can quietly send stolen information back to the attackers, CloudSEK reports.The FBI has already warned that online file converters are becoming a popular way for criminals to spread their malware. CloudSEK’s research shows that attackers are improving their methods, cleverly blending realistic website designs with social engineering tricks in order to lower users' defenses.With online tools becoming part of everyday work and personal life, it’s important to know how to avoid these threats.
How to stay safe
(Image credit: Amazon India)
The best way to protect yourself is to avoid clicking random search results for online file converters. Always visit known official websites directly.In addition to that, always double-check the website address for small spelling changes that might be easy to miss.For a good starting point, check out our round up of the best PDF editors, and the best free PDF editors. We also recommend the best Adobe Acrobat alternatives.Staying cautious when uploading documents online can stop many of these attacks before they start.Keep your antivirus software up to date (you’re doing this anyway, right?) and scan any downloaded files before you open them. Installing browser extensions that block suspicious or dangerous sites can also help.If a website asks you to run PowerShell commands or download extra files after uploading a document, close the page immediately.Finally, if you think you’ve been tricked, disconnect the device from the internet right away, change all important passwords from a safe device, and let your bank or service providers know as soon as possible.
You might also like
Stay protected with the best endpoint protection tools aroundWe've also rounded up the best ransomware protection toolsAnd these are the best free PDF to Word tools you can use
-

Picture from ichef.bbci.co.uk
Rank 10522 -
Picture from o.aolcdn.com
Rank 10523Bluesky is adopting an official verification system after all. In an update, the company said it plans to grant blue checkmarks to “authentic and notable” accounts. It will also allow some “trusted organizations" to verify users as well.
The change is a notable shift for the upstart platform, which previously resisted the idea of centralized verification. Up to now, the company has relied on a domain-based verification system, which allows users to change their handles to match domains that they are associated with. But that approach was often criticized for being overly complicated and offering insufficient protection from impersonation.
These critiques have only amplified as Bluesky has grown in popularity and attracted more prominent users. For example, when former President Barack Obama joined Bluesky in recent weeks, his handle did not use a custom domain, which understandably led many users to question whether the account was authentic. Instead, individual Bluesky employees ended up publicly vouching that the account was legitimate
Under Bluesky’s new system, the company will proactively verify certain accounts and add a prominent blue checkmark to their profile. It’s not clear what criteria Bluesky will use for these badges or how it plans to verify users’ identities. Additionally, there will be a slightly different blue badge — one with “scalloped edges” — that certain “trusted organizations” can grant through a new “trusted verifiers” feature.
Bluesky
The New York Times is one such organization, and the newspaper will now be able to hand out blue checks to its journalists. Bluesky didn’t say what other organizations will be able to participate in the program, but added that it will review verification from third-parties in order to “ensure authenticity.”
Notably, Bluesky said that people and organizations are still “highly encourage(d)” to verify themselves via a custom domain. And it sounds like the new blue ticks may be in short supply, at least to start. “During this initial phase, Bluesky is not accepting direct applications for verification,” the company wrote in its announcement. “As this feature stabilizes, we’ll launch a request form for notable and authentic accounts interested in becoming verified or becoming trusted verifiers.”This article originally appeared on Engadget at https://www.engadget.com/social-media/bluesky-is-getting-blue-checkmarks-and-an-official-verification-system-173204662.html?src=rss
-

Picture from ichef.bbci.co.uk
Rank 10524 -

Picture from techcrunch.com
Rank 10525 -

Picture from ichef.bbci.co.uk
Rank 10526 -
Picture from o.aolcdn.com
Rank 10527Nearly four years after it was originally announced, Riot Games has finally shared a look at Valorant Mobile. The mobile version of the competitive shooter was developed by LightSpeed Studios and will launch in China first before coming to other countries and regions.
Valorant Mobile looks like it relies on a lot of onscreen buttons, but based on a brief gameplay video, the game otherwise seems pretty similar to its PC counterpart in terms of speed and intensity. LightSpeed Studios successfully adapted PlayerUnknown's Battlegrounds into PUBG Mobile, and Riot Games clearly believes the developer has managed to do the same with the originally mouse-based Valorant.
Coming to mobile has been in the works for Valorant for years, and makes a ton of sense given the current popularity of mobile first-person shooters like PUBG Mobile and Call of Duty: Warzone. This isn't the first time the game's precise gunplay has had to be adapted to a slightly more cumbersome control scheme, either. Valorant successfully made the jump to controllers when it launched on Xbox Series X/S and PlayStation 5 in 2024. Mobile controls aren't that much bigger of a hurdle in comparison.
Players in China can pre-register now to be ready for the next playtest, ahead of a more formal launch at some point in the future.This article originally appeared on Engadget at https://www.engadget.com/gaming/valorant-mobile-pre-registration-is-open-in-china-180132021.html?src=rss
-

Picture from ichef.bbci.co.uk
Rank 10528 -
Picture from ichef.bbci.co.uk
Rank 10529 -

Picture from techcrunch.com
Rank 10530 -

Picture from ichef.bbci.co.uk
Rank 10531 -
Picture from ichef.bbci.co.uk
Rank 10532 -
Picture from ichef.bbci.co.uk
Rank 10533 -
Picture from cdn.mos.cms.futurecdn.net
Rank 10534The FBI is warning about an ongoing scheme targeting victims of online fraudThe victims are encouraged to reach out to a person on Telegram, posing as the chief of IC3The person would try to gain access to the victims' financial accounts
Cybercriminals are preying on victims of online fraud, using their state of emotional distress to cause even more harm, the FBI has said, revealing it received more than a hundred reports of such attacks in the last two years.In the campaign, cybercriminals would create fake social media profiles and join groups with other victims of online fraud. They would then claim to have recovered their money with the help of the FBI's Internet Complaint Center (IC3). This makes the ruse credible, since IC3 is an actual division of the FBI and serves as a central hub for reporting cybercrime.Those who believe the claim are then advised to contact a person named Jaime Quin on Telegram. This person, claiming to be the Chief Director of IC3, is actually just part of the scheme. Quin will tell people who reach out that he recovered their funds and would then ask for access to their financial information, to steal even more money.
Get Keeper Personal for just $1.67/month, Keeper Family for just $3.54/month, and Keeper Business for just $7/monthKeeper is a cybersecurity platform primarily known for its password manager and digital vault, designed to help individuals, families, and businesses securely store and manage passwords, sensitive files, and other private data. It uses zero-knowledge encryption and offers features like two-factor authentication, dark web monitoring, secure file storage, and breach alerts to protect against cyber threats.Preferred partner (What does this mean?)View Deal
Getting in touch
This is just one example of how the scam works. The FBI says that initial contact from the scammers can vary.“Some individuals received an email or a phone call, while others were approached via social media or forums," it said. "Almost all complainants indicated the scammers claimed to have recovered the victim's lost funds or offered to assist in recovering funds. However, the claim is a ruse to revictimize those who have already lost money to scams."To minimize the risk of falling victim to these scams, you should only reach out to law enforcement through official channels. Furthermore, you should keep in mind that law enforcement (especially those in executive positions) will never reach out to you this way, especially not to initiate contact.Finally, the police will never ask for your password, financial information, or access to private services.Via BleepingComputer
You might also like
Key Strategies for financial institutions to combat fraudTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-

Picture from techcrunch.com
Rank 10535 -
Picture from techcrunch.com
Rank 10536 -
Picture from ichef.bbci.co.uk
Rank 10537 -
Picture from ichef.bbci.co.uk
Rank 10538 -
Picture from cdn.mos.cms.futurecdn.net
Rank 10539Bluesky, the upstart, decentralized social network that's offered an island of blue calm for those departing the tumultuous, dark waters of X (formerly Twitter), is finally introducing an official form of account verification. It will look familiar to those who spent time on old-school Twitter, but it does feature a few notable caveats.Up until today (April 22, 2025), there was no Bluesky-supported system for verifying an account or visual indication of verified status, and the microblogging social media platform was suffering from an imposter problem. Bluesky addressed this, in a way, by encouraging people to set up and use their own domain names to establish the veracity of an account.My account, for instance, is attached to lanceulanoff.com, a domain I've owned for years. Bluesky reports that some 270,000 accounts have linked their accounts to domains.Still, setting up a domain and connecting it to your Bluesky account is not a trivial matter. This new feature significantly simplifies the process.
A new check
(Image credit: Future)
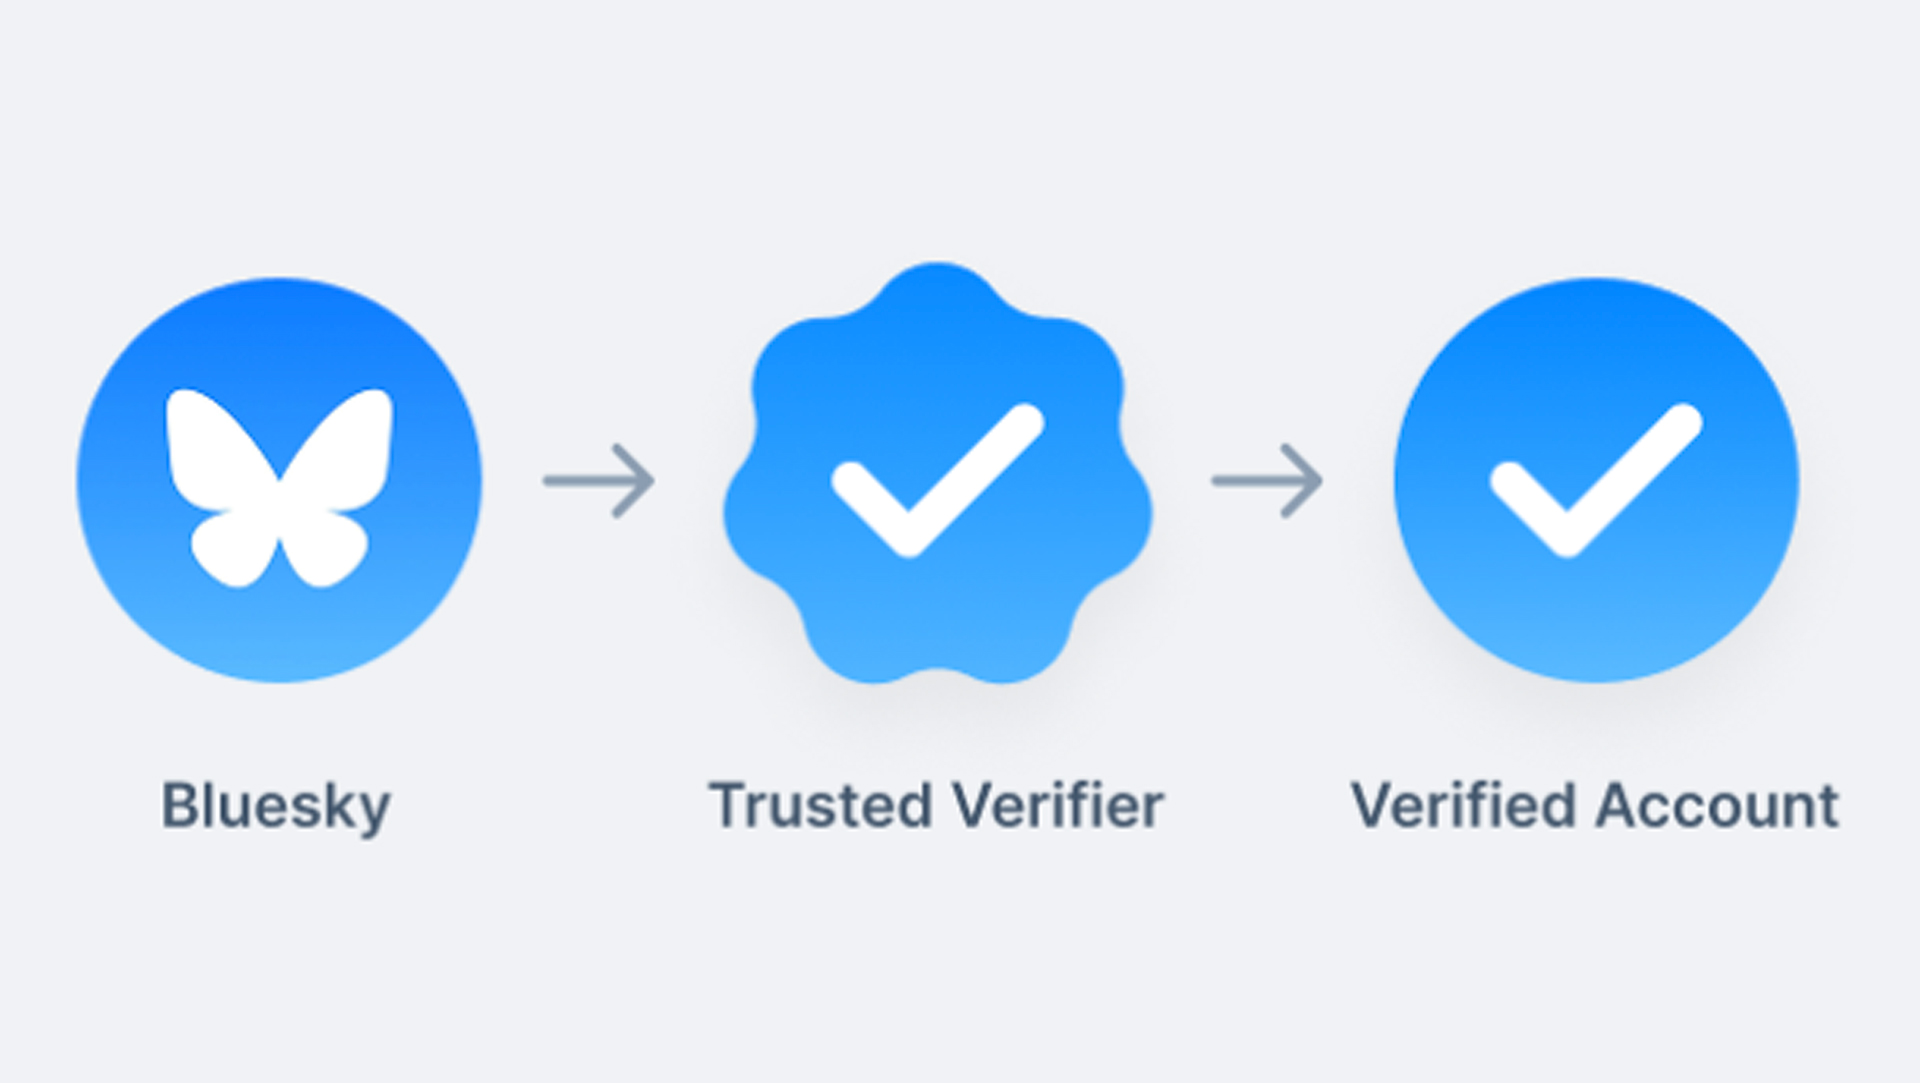
According to a new Bluesky blog post, there are now three levels of identity on the platform: the basic Bluesky account, a Trusted Verifier, and a Verified Account.The Trusted Verifier is interesting because it's a verified account that, with Bluesky's review, can verify other accounts. The example given is The New York Times' Bluesky account, which can then verify its journalists' accounts.Years ago, Twitter had something similar, where an entity like TechRadar could ask Twitter directly to verify some of its journalist employee accounts.It was not a popular feature among, for instance, celebrities and officials, who wondered (often on Twitter) why journalists needed verification. The topic of Blue Checks and verification on Twitter became so fraught that, for a time, Twitter's then-CEO Jack Dorsey stopped verifying accounts. When Elon Musk took over, he removed verifications from millions of accounts, only to return them some months later.
Who verifies who
Bluesky wrote that it is proactively verifying some "authentic and notable accounts," which will now have a white check in a blue circle.Trusted Verifiers will have a scalloped blue check to indicate their vaunted status. A tap on someone's verified status can show you which Trusted Verifier granted verification.It's not necessarily a foolproof system, as I think media companies might seek to verify all journalists in their camp, and Bluesky could push back against that. Or maybe Bluesky says yes, but at some point, "the notables" grow irritated because there are suddenly so many non-famous people with checks.One thing Bluesky is not supporting is "requests for verification." However, the social media platform is not ruling it out and has promised that as this system settles in and stabilizes, it will "launch a request form for notable and authentic accounts interested in becoming verified or becoming trusted verifiers."If you're wondering about the other decentralized social media platform, Threads, it adopts verifications directly from Instagram, another Meta property.It'll be interesting to see what Bluesky asks for in its future verification process and if any part of it will involve some form of ID.
You might also like
What is Bluesky? The new social media network explainedHow to switch to Bluesky from TwitterI wasted my day on Bluesky Social and no, I'm not sorry
-
Picture from techcrunch.com
Rank 10540 -
Picture from o.aolcdn.com
Rank 10541We know Cassian Andor is doomed. 2016's Rogue One makes clear he will meet an untimely death in a massive explosion. That sense of inevitable destruction lingered in the background of the first season of Andor, the prequel series that follows his journey from a low-rent criminal to a rebel spy. But his fate is even more crushing in Andor's second (and final) season, where the cost of fighting against the seemingly all-powerful Empire chips away at his soul.
"Rebellions are built on hope," was an iconic line from Rogue One, first uttered by Andor and then repeated triumphantly by that film's lead, Jyn Erso. In the streaming series' second season, we see how that idea is formed and inspires many people. Rebellions aren't just about massive space battles, and Death Star trench runs. They don't rely on an untrained kid hopping into a spaceship and scoring a major victory thanks to the Force and destiny. Rebellions start with small decisions by normal people, and through collective action they evolve into something powerful enough to take down empires. Read into that what you will.
Lucasfilm Ltdâ¢
Andor always seemed like an odd series for Disney, which spent the last decade milking the Star Wars franchise for all it's worth. Created by Tony Gilroy, the Bourne Identity screenwriter who reportedly swooped in to save Rogue One at the last minute, Andor has no lightsabers and minimal references to the Force. While it's filling in the gaps for a storyline that leads to A New Hope, the series also feels refreshingly free of the stifling mythology that has plagued shows like The Mandalorian and Ahsoka (and Boba Fett, and Obi-Wan Kenobi). Andor takes its time, building up its characters and laying out complex ideas, instead of rushing between action set pieces. It's Star Wars for grownups, something I never thought we'd see for a franchise so devoted to kids.
In season one, we're introduced to Andor as he's searching for his sister, who disappeared years ago. After being targeted by two local police officers, he ends up killing them both and is forced to hide out in his home planet of Ferrix. There he meets up with his friend Bix (Adria Arjona), who is working for Luthen Rael, a mysterious man who has devoted his life to taking down the Empire. It doesn't take long before Luthen sees potential in Andor, and begins to court him for his rebel cause.
Lucasfilm Ltdâ¢
Minor spoilers ahead for Andor season two.
Taking place over the course of a few years (and counting down to the Battle of Yavin, where the Death Star was destroyed in A New Hope), season two follows Andor and Bix as they delve further into the rebellion. Bix is still recovering from the events of the first season, where she was imprisoned and tortured. And Andor splits his time caring for Bix and going on spy missions to help rebels on other planets.
I won't say too much about what happens in the season specifically, but in general it builds on everything that made Gilroy's first stab such a refreshing Star Wars entry. We see how the heartless machinations of the Empire affect real people, and how it can push entire populations to fight against tyranny. Small moments, like a hotel bellhop revealing his true thoughts about the Empire to Andor, can lead to more profound acts of rebellion.
Lucasfilm Ltdâ¢
Star Wars has always been about the battle between good and evil. But Andor breaks down what that means for ordinary people, not hyper-powerful space wizards with laser swords. An average citizen could be killed on the spot if they decide to speak up against the Empire. Or, with self-preservation in mind, they could keep their heads down or even volunteer to be a cog in the fascist machine. Not everyone can be Han Solo (though Andor himself is a bit close). But when living under an authoritarian regime, there comes a time for everyone to draw a line. Resist, or lose your soul.
Andor also spends plenty of time on Senator Mon Mothma (Genevieve O'Reilly) before she eventually becomes the leader of the Rebel Alliance. We see her dealing with the difficulty of funding Luthen's rebel activities, especially as they lead to explosive outcomes. But after the Empire massacres thousands of civilians on the planet Ghorman, an event that’s been referenced in recent Star Wars books, Mothma and other rebel leaders conclude that violent rebellion is the only way to fight back against the fascist Empire.
Lucasfilm Ltdâ¢
"The Empire has been choking us so slowly, we're starting not to notice. The time has come to force their hand," Luthen tells Senator Mothma in Andor's first season. When she notes that people will suffer, he replies "That's the plan. You're not angry at me. I'm just saying out loud what you already know. There will be no rules going forward. If you're not willing to risk your conscience, then surrender and be done with it."
Even though this is Andor's final season, I have a feeling this series will live on in viewer's minds far longer than whatever the hell happened in The Book of Boba Fett. It forces you to think about how the Empire directly affects everyone, from civilians on remote planets to the bureaucratic stooges devoting their lives to fascism. In many ways, it's practically a blueprint for rebellion. And not to put too much on a Disney TV show, but that feels like something we could use right now.This article originally appeared on Engadget at https://www.engadget.com/entertainment/tv-movies/andor-season-2-review-a-star-wars-miracle-an-ode-to-rebellion-190057159.html?src=rss
-
Picture from techcrunch.com
Rank 10542 -
Picture from o.aolcdn.com
Rank 10543The Federal Trade Commission has decided to take formal action against ride-hailing service Uber over what it describes as "deceptive billing and cancellation practices." The FTC's lawsuit, filed on Monday, specifically takes issue with the Uber One service, which lets subscribers earn cash back on rides, get free deliveries and avoid cancellation fees.
According to the FTC, Uber made it easy for subscribers to join Uber One, but much harder to cancel. "Users can be forced to navigate as many as 23 screens and take as many as 32 actions to cancel," the commission claims. The company also reportedly charged some users before their bill their free trial was up, and misrepresented the savings Uber One offered by not taking its subscription fee into account.
The lawsuit says that Uber's actions violated the FTC Act and the Restore Online Shoppers' Confidence Act, which "requires online retailers to clearly disclose the terms of the service they are selling, obtain consumers' consent before charging them for a service and provide a simple way to cancel a recurring subscription."
Uber intends to fight the lawsuit and believes that the FTC has misrepresented the facts in some key ways. The company says that it "does not sign up or charge consumers without their consent" and that subscription cancellations can happen in-app, at any point. Uber does acknowledge that subscriptions previously had to be cancelled 48 hours before a charge through the company's support team, but that's apparently no longer the case.
Despite the best efforts of tech executives, the Trump administration has maintained a level of animosity towards tech companies. New FTC chair Andrew Ferguson suggested that censorship would be a major concern for the FTC under President Donald Trump, but the commission is still moving forward with an antitrust case against Meta, for example. The possibility for the (technically) independent organization to be wielded as a weapon by Trump feels a lot more likely without any Democrat members.This article originally appeared on Engadget at https://www.engadget.com/big-tech/ftc-sues-uber-over-claims-the-company-makes-subscriptions-hard-to-cancel-191552906.html?src=rss
-
Picture from techcrunch.com
Rank 10544 -

Picture from techcrunch.com
Rank 10545 -
Picture from cdn.mos.cms.futurecdn.net
Rank 10546Synology’s 2025 Plus range only works with certain hard drivesIt says this is for lower failure rates and compatibility issuesOlder models won’t be affected by this new policy
Taiwanese NAS-maker Synology has confirmed a new policy that requires Synology-branded hard drives to be used for full compatibility within its 2025 Plus series of network-attached storage (NAS) devices.From launch, the policy states Synology-branded hard drives will need to be used, but the company promises to “update the Product Compatibility List as additional drives can be thoroughly vetted in Synology systems,” a company spokesperson said(via Ars Technica).In the meantime, this could spell out reduced choice and increased cost for customers, with potential sustainability issues stemming from users’ inability to use hard drives they might already have, rendering them unusable.
Synology NAS devices hard drives
Synology has nine products in its Plus range, supporting all the way up to 24 hard drives, however users will be required to use approved storage drives only.The company said that “Synology systems are at less risk of drive failure and ongoing compatibility issues.”Chad Chiang, the Managing Director of Synology’s Germany and UK businesses, noted: “With our proprietary hard disk solution, we have already seen significant benefits for our customers in various deployment scenarios.”Despite the change for 2025-onward models, the company confirmed that older models sold up to and including 2024 (excluding XS Plus series and rack models) remain unchanged.Interestingly, Synology doesn’t manufacture its own hard drives, instead choosing to rebrand models from popular brands like Toshiba and Seagate.This could be good news, indicating the possibility that further Toshiba and Seagate models might appear on the approved list of third-party drives at a later date, however it could also mean that drives from other brands might be less likely to appear on the list.Of course, this is speculation only, but we’ve contacted Synology for further details in the hope that we can get access to a list of pre-approved third-party drives.
You might also like
We’ve listed the best NAS hard drivesKeep your data online with the best cloud storage solutionsPopular NAS vendor issues emergency patch against potentially highly damaging vulnerabilities — here's what you need to know
-
Picture from techcrunch.com
Rank 10547 -
Picture from ichef.bbci.co.uk
Rank 10548 -
Picture from ichef.bbci.co.uk
Rank 10549 -
Picture from o.aolcdn.com
Rank 10550The American Civil Liberties Union is suing to find out exactly what information the so-called Department of Government Efficiency has accessed from federal agencies. The civil rights organization submitted a Freedom of Information Act request to several goverment departments in February; it is now suing to get responses from the Social Security Administration and the Department of Veterans Affairs. The SSA denied the group's request for expedited processing and has not responded to the ACLU's appeal, while the VA did not act on the FOIA request, according to the press release announcing the lawsuit.
The ACLU requested any records that would show whether DOGE members have accessed databases that contain personally identifying information about citizens. The request also seeks information about whether AI is being used to analyze government data.
"The federal government cannot dodge accountability by ignoring our lawful demands for transparency," said Nathan Freed Wessler, deputy director of the Speech, Privacy and Technology Project within the ACLU. "The American people have an urgent need to know if their private financial, medical and personal records are being illegally accessed, analyzed or weaponized by Trump's unaccountable team of unvetted outsiders. This is doubly true for our seniors and veterans, who are at particular risk if their data has been accessed illegally."
DOGE, a group headed by Elon Musk, has been leading the move to cut jobs across federal agencies, including those that oversee Musk's business endeavors. Although there have been other lawsuits trying to prevent people who are not civil servants from accessing sensitive government data, other reports claim DOGE members have been trying to circumvent court orders that limit their reach.This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/aclu-sues-two-federal-agencies-for-transparency-around-doge-activity-195916390.html?src=rss


