News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from static.independent.co.uk
Rank 80201 -

Picture from static.independent.co.uk
Rank 80202 -

Picture from static.independent.co.uk
Rank 80203 -
Picture from ichef.bbci.co.uk
Rank 80204 -

Picture from static.independent.co.uk
Rank 80205 -

Picture from static.independent.co.uk
Rank 80206 -

Picture from static.independent.co.uk
Rank 80207 -

Picture from static.independent.co.uk
Rank 80208 -

Picture from static.independent.co.uk
Rank 80209 -

Picture from static.independent.co.uk
Rank 80210 -

Picture from static.independent.co.uk
Rank 80211 -

Picture from static.independent.co.uk
Rank 80212 -

Picture from static.independent.co.uk
Rank 80213 -
Picture from static.independent.co.uk
Rank 80214 -
Picture from cdn.mos.cms.futurecdn.net
Rank 80215The recent ransomware attack on the retailer, Marks and Spencer (M&S) is a stark reminder of just how exposed modern businesses are to cyber threats, not only within their own walls, but also through the very partners and suppliers they rely on for their daily operations.While M&S was not breached directly, the vulnerability of a third-party supplier provided an unintended entry-point that ultimately impeded operations, disrupted logistics and wiped hundreds of millions off its market value, further underscoring the shared responsibility of ensuring security across modern digital ecosystems in a business.The cyberattack wasn’t just a simple smash-and-grab, rather it was a calculated, multi-stage operation by notorious cybercrime group, Scattered Spider. It worked because the group created a perfect storm consisting of sophisticated phishing tactics, deft social engineering and a leveraged a simple supply chain link that wasn’t toughened up to today’s resilience standards.The brunt of it is that it is no longer enough to protect a single business’s cyber walls. In a hyperconnected ecosystem, the weakest supplier is the most vulnerable point and threat actors know it.How the attack workedDetails emerging from the M&S breach suggest that the threat actors used phishing tactics to gain their initial foothold into a supplier’s systems. While this is not confirmed in this particular case, it does fall in line with FBI reports that email is the primary starting-point for 90% of phishing incidents. Through impersonation and manipulation, the attackers convinced IT personnel at the supplier to reset authentication credentials, essentially handing over the keys to the digital kingdom.This method of exploitation wasn’t purely technical, rather deeply human. More commonly known as social engineering amongst cyber professionals, this tactic relies on psychological manipulation, exploiting trust, urgency or confusion to trick targets into compromising their own business’s security. While the supplier’s IT staff, henceforth dubbed ‘innocent insiders’, did not intend to harm, unfortunately and unintentionally they gave the attackers the access they needed, all in a moment of misjudgment.Once the foothold was established, the attackers were able to deploy the ransomware and subsequently disrupt food logistics, shutter operations, and inflict an expected £300 million hit to operating profits. This led to over £750 million being erased from M&S’s market capitalization in the fallout. While the scale of this incident is exceptional, it reflects a broader trend in the sector. In fact, according to Trustwave’s recent research on the retail cyber threat landscape, the average cost of a breach in the industry is approximately £2.6 million, underscoring just how financially damaging these incidents can be, even at baseline.Despite this, it should be recognized that M&S’s swift decision to take its website, mobile app, contactless payment systems, and Click & Collect services offline demonstrates a responsible containment strategy. While this caused disruption to consumers, it aligns with best-practice incident response protocols aimed at halting further spread and preserving customer trust.The rise of third-party riskThis incident is not unique to M&S. What makes it particularly instructive is how clearly it illustrates the growing threat posed by third party risk.It is no secret that most organizations today operate within sprawling digital ecosystems, relying on dozens, sometimes even hundreds, of external vendors for everything from cloud hosting and IT services to logistics and customer support. While this interdependence drives forward efficiency and innovation, it also significantly expands the attack surface, within which cybercriminals can operate successfully.Despite growing awareness, supplier security is still too often treated as a secondary concern, either addressed during onboarding or relegated to contractual obligations. But in today’s threat landscape, it’s essential that supplier networks be held to the same standards of resilience as internal operations. This means adopting continuous oversight, setting clear access controls, and treating cyber assurance as an ongoing process rather than a one-off audit.Lessons from the breachAnother thing that was laid bare as a result of this cyberattack, and something businesses need to be keenly aware of, is that even the most well intentioned employee can be manipulated. To defend against this threat, cybersecurity training, especially on common phishing tactics and social engineering methods in any given industry, is non-negotiable. To supplement this effort, simulations and scenario-based drills can be used as these help employees better recognize red flags in the system and how to respond appropriately.A simple, yet effective method to prevent unauthorized access is to implement multifactor authentication (MFA) across all systems. According to Microsoft, 99% of the compromised Microsoft accounts in the M&S breach did not have MFA enabled. In addition to this, the principle of least privilege must be followed to ensure that employees and third parties alike only have the access that is absolutely required. This ensures that even if a threat actor gains access to an organization's systems, they are unable to move laterally within the network.In fact, to truly limit the spread of threats once the hacker has already gained access, businesses must embrace network segmentation. This is a cybersecurity practice that divides a network into smaller, isolated sections, each with its own access controls and security protocols. One can think of this as compartmentalizing a building where, instead of giving every employee a master key to every room, the access is restricted so people can only enter those areas that are necessary for their jobs.Beyond internal defenses, organizations must also work collaboratively with their suppliers to enhance overall security of their vendor network. This requires knowing exactly what data a vendor has access to, understanding how they manage security and integrating them within the core business’s awareness and response plans. Additionally, threat intelligence sharing, joint training exercises and clear incident response plans can transform supplier networks from a liability into an organization's first line of defense.The final line of defense, especially in a ransomware scenario is having a robust backup and recovery strategy in place. Threat actors employing ransomware tactics often target backup systems to prevent quick recovery. With this in mind, backups need to be stored offline or in immutable environments, which cannot be changed or encrypted by attackers. To ensure that restoration works in practice and not just in theory, regular testing of the backups is another key step in bolstering an organization's cyber defense posture.The bottom lineUltimately, the M&S incident is a real-world case study of the operational fragility that can arise when cybersecurity isn’t fully embedded across the supply chain. It also provides a powerful lesson for the organizations across various sectors that resilience must extend beyond internal networks and into the broader digital ecosystem. In a world where every transaction, delivery, and customer interaction relies on technology, effective defense demands both strategic investment and human vigilance, both within the business and across its partners.Train up with the best online cybersecurity courses.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-
Picture from ichef.bbci.co.uk
Rank 80216 -

Picture from static.independent.co.uk
Rank 80217 -

Picture from static.independent.co.uk
Rank 80218 -
Picture from static.independent.co.uk
Rank 80219 -

Picture from static.independent.co.uk
Rank 80220 -

Picture from static.independent.co.uk
Rank 80221 -

Picture from static.independent.co.uk
Rank 80222 -

Picture from static.independent.co.uk
Rank 80223 -

Picture from static.independent.co.uk
Rank 80224 -

Picture from ichef.bbci.co.uk
Rank 80225 -

Picture from static.independent.co.uk
Rank 80226 -

Picture from static.independent.co.uk
Rank 80227 -

Picture from static.independent.co.uk
Rank 80228 -

Picture from static.independent.co.uk
Rank 80229 -

Picture from image.cnbcfm.com
Rank 80230 -

Picture from cdn.mos.cms.futurecdn.net
Rank 80231Kioxia has added a 245.76TB SSD to its LC9 seriesIt is the biggest SSD ever launched, and is already being sampled to clientsSolidigm, Phison, Dapustor, Samsung and Sandisk are the other big contenders in this categoryJapanese SSD vendor Kioxia has unveiled a 245.76TB NVMe SSD, the LC9, which is squarely aimed at enterprise clients looking for the highest capacity available.Capable of holding more than 52,000 DVD movies, it is the largest SSD ever launched, at twice the capacity of the next biggest SSD, the Solidigm D5-P5336.The LC9 is available in legacy 2.5-inch as well as E3.L form factor. A smaller 122.88TB SSD can be ordered in a more compact E3.S form factor. Kioxia didn’t provide more details other than it is a PCIe 5.0 product offering a wide range of security options (SIE, SED, FIPS SED etc) and support for OCP specs.Supersized SSD are essential for AIWe don’t know what the warranty or endurance (measured in drives written per day) are but we do know that the storage device uses a proprietary NAND solution, a 32-die stack of 2 Tb BICS FLASH QLC 3D flash memory; that’s one chip containing 8TB of storage.Kioaix has confirmed the LC9 will make a formal debut at the Future of Memory and Storage 2025 conference, and some customers will have samples soon.Generative AI has put GPUs and compute squarely in the limelight but storage (or system memory) is rarely mentioned and yet pivotal to any AI success story.As Kioxia puts it, GAI “places unique demands on storage, including the need to store vast datasets for training large language models (LLMs), and to create embeddings and vector databases that support inference through retrieval augmented generation (RAG)”.And we can thank AI for being the catalyst in the current storage race. For the best part of a decade, Exadrive’s 100TB 2.5-inch SSD was the storage champion but since then Solidigm, Phison, Dapustor and Samsung, have showcased or launched 122.88TB SSDs.Sandisk, Kioxia’s partner also confirmed it will launch a 256TB SSD in 2026 and a 512TB SSD in 2027. It is worth highlighting all these drives are geared towards hyperscalers and the enterprise market and will compete against hard drives like Seagate’s 36TB Exos M.Consumers will have to contend with 8TB SSDs, currently the largest capacity for mainstream buyers, a glass ceiling that hasn’t been shattered for the past five years and unlikely to change for the foreseeable future.You might also likeThese are the best NAS devices aroundUK police arrest four following cyberattacks on M&S, Co-op, HarrodsWe've rounded up the best cloud storage platforms on offer
-
Picture from ichef.bbci.co.uk
Rank 80232 -
Picture from ichef.bbci.co.uk
Rank 80233 -

Picture from ichef.bbci.co.uk
Rank 80234 -

Picture from static.independent.co.uk
Rank 80235 -

Picture from image.cnbcfm.com
Rank 80236 -
Picture from cdn.mos.cms.futurecdn.net
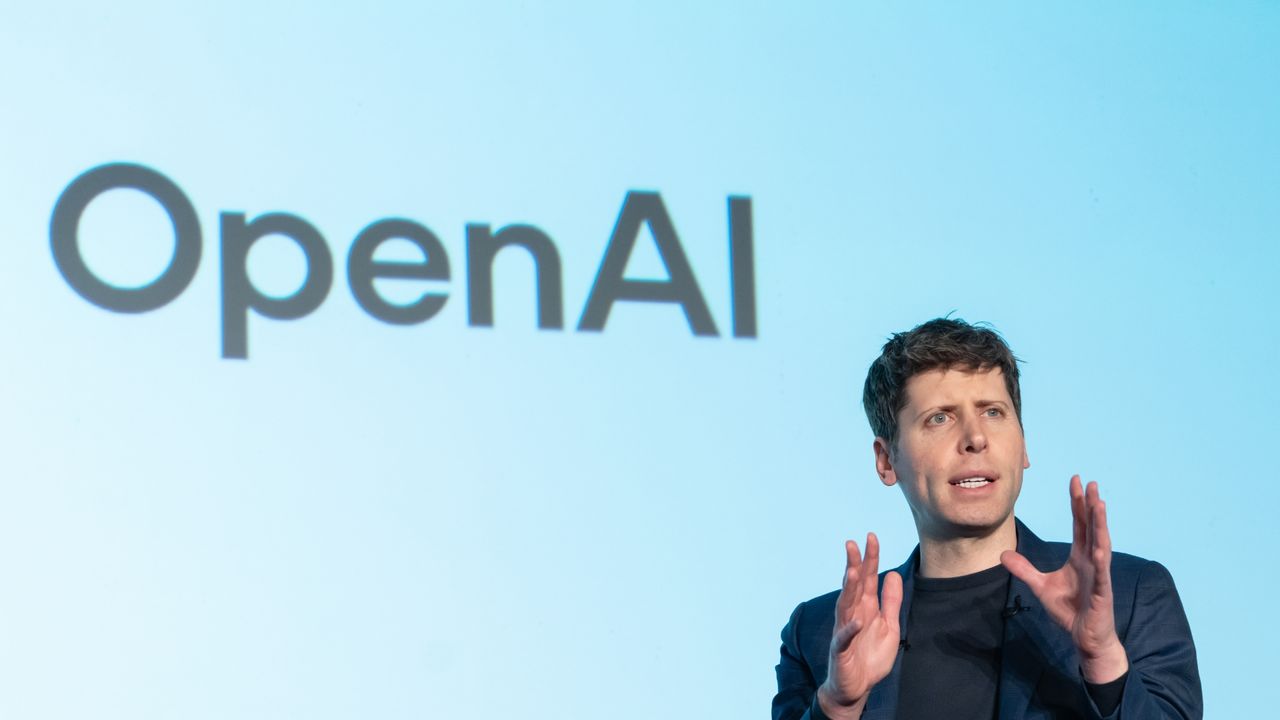
Rank 80237OpenAI signs wide-ranging deal with the UK government - with AI coming to more of our everyday livesUK Government signs major deal with OpenAI to deploy more AIGPT already powers Humphrey and Consult services, with more to comeOpenAI is also expanding its UK officesOpenAI and the UK Government have signed a Memorandum of Understanding as part of a plan to "maintain a world-leading UK AI ecosystem rooted in democratic values."The deal will see OpenAI explore investments in UK AI infrastructure, including data centers and so-called AI Growth Zones, which could level the playing ground across the UK with sites in Scotland and Wales.Through the Memorandum of Understanding, the UK Government hopes to deploy AI across justice, defence, education and public services to improve efficiency.UK Government doubles down on AIOpenAI's technology already forms the basis of a number of UK Government tools, including the ChatGPT-enhanced Humphrey for civil service workers and the GPT 4o-enhanced Consult for policy making.UK Technology Secretary Peter Kyle welcomed the collaboration with the world-leading AI company: "AI will be fundamental in driving the change we need to see across the country – whether that’s in fixing the NHS, breaking down barriers to opportunity or driving economic growth.""Britain has a strong legacy of scientific leadership and its government was one of the first to recognise the potential of AI through its AI Opportunities Action Plan," OpenAI CEO Sam Altman added.The UK has already pledged to invest "up to £500 million" to support sovereign AI, and has broader plans outlined in its AI Opportunities Action Plan which states the UK is the third-largest AI market globally behind the US and China.Looking ahead, AI Growth Zones will facilitate the construction and deployment of AI centers via priority access to sustainable energy sources and a combination of public and private partnerships.More broadly, OpenAI also plans to increase its presence in the UK by expanding its office footprint in London – its first international office.You might also likeThe best AI tools and best AI writers can help you boost productivityAccess the most powerful chips via the best cloud computing providersGoogle Cloud and UK Government reveal major push to end "ball and chain" legacy tech
-

Picture from cdn.mos.cms.futurecdn.net
Rank 80238The DC Universe's (DCU) Wonder Woman movie has found its lead writerIt's the same scribe who penned the screenplay for SupergirlDC Studios co-chief James Gunn has confirmed the news on social mediaJames Gunn has confirmed who has been hired to write the Wonder Woman movie that's set in the DC Universe (DCU).Taking to Threads yesterday (July 21), Gunn revealed that reports suggesting Ana Nogueira had been tapped to write the untitled Wonder Woman film were true. The Wrap was the first to claim Nogueira had boarded the DC Studios film, with The Hollywood Reporter later indicating its sources had heard the same.Gunn posted on Threads to confirm Nogueira's hiring (Image credit: James Gunn/Threads)The forthcoming Diana Prince-starring flick, which Gunn first hinted at in mid-May, is the second movie Nogueira will tackle for DC Studios. Her first writing credit came in the form of the script for Supergirl: Woman of Tomorrow, which has since been renamed Supergirl by Gunn. You can read more about that project, including its release date and confirmed cast, in my ultimate guide on Supergirl.Nogueira is also believed to be taking a stab at the screenplay for a live-action Teen Titans Go! adventure on the big screen. The Wrap claims it's still in development, but it's unclear if it'll be set in the DCU.Nogueira's hiring comes hot on the heels of reports that Gunn and DC Studios co-head Peter Safran are fast-tracking a film starring the iconic metahuman.Last month, Gunn announced a Wonder Woman movie was being worked on and fans immediately picked out a recent Star Wars actor who'd be perfect to play her.So, who will play the Amazonian in the DCU? Gunn has declared nobody is currently in the running to portray the eponymous Themysciran, with the former Marvel filmmaker saying as much on a July 18 edition of the Happy Sad Confused podcast. Gunn and Safran haven't found a director, either, so the pair will need to answer these questions – i.e. who'll direct Wonder Woman and who'll star in it – soon if they want to stop gossip columns from churning out all kinds of rumors.Nobody has been cast as the DCU's version of Diana Prince yet (Image credit: DC Comics)In another recent interview, this time with Rolling Stone, Gunn also clarified that, despite his wish to usher Prince into his cinematic universe, the DCU Chapter One flick wasn't necessarily being prioritized above other projects."I don’t know what they [industry insiders] mean by fast-tracking," he opined. "I’ve always had Wonder Woman as a priority, but we got the first few things started, and there’s some other things that are really close to green-lighting. Like, there’s a television show that I hope that we’re going to be green-lighting in the next few days."So, now a little time has passed, and we really need Wonder Woman and we really need Batman, because they’re so important to us. And so, it’s become a little bit more like going to everybody at DC and being like 'we need to figure this out'."We have good writers on Wonder Woman and we just have to make sure it’s working and they have to not be somebody who’s going to take two years to write a script."Considering Gunn says "writers", Nogueira seems to be co-penning the script with at least one other scribe. For now, Gunn isn't saying who that individual is, but I'm sure we'll learn more as development continues on this 'Gods and Monsters' production.You might also likeHere's how to watch the DC movies in orderFirst poster for Supergirl reveals near-full look at the DC comic book hero's outfit – and puts a rebellious spin on Superman's 'look up' taglineSuperman's most surprising cameo has got me asking 3 big questions about James Gunn's next DCU project
-

Picture from ichef.bbci.co.uk
Rank 80239 -

Picture from static.independent.co.uk
Rank 80240 -

Picture from static.independent.co.uk
Rank 80241 -

Picture from static.independent.co.uk
Rank 80242 -

Picture from static.independent.co.uk
Rank 80243 -
Picture from static.independent.co.uk
Rank 80244 -

Picture from static.independent.co.uk
Rank 80245 -

Picture from ichef.bbci.co.uk
Rank 80246 -

Picture from static.independent.co.uk
Rank 80247 -

Picture from static.independent.co.uk
Rank 80248 -

Picture from static.independent.co.uk
Rank 80249 -

Picture from static.independent.co.uk
Rank 80250