News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from assets2.cbsnewsstatic.com
Rank 67351 -

Picture from assets1.cbsnewsstatic.com
Rank 67352 -

Picture from cdn.mos.cms.futurecdn.net
Rank 67353A ransomware attack is a nightmare scenario for any organization. It’s disruptive, costly, and often deeply damaging to your reputation. How you respond in the first 24 hours can make all the difference between containment and catastrophe. In those critical moments, fast and informed action is essential. Not just to mitigate harm, but to enable recovery and identify root causes.Whether you’re facing a live breach or want to prepare your response strategy in advance, here’s what needs to happen in the vital first 24 hours.Step one: confirm the attack and isolate systemsThe moment ransomware is suspected, the priority is to confirm what’s happened. Ransomware doesn’t always announce itself with a dramatic pop-up screen. It may begin quietly, encrypting files and spreading laterally across your network. Early signs might include inaccessible files, failed logins, or unusual outbound traffic.Once confirmed, isolate affected systems from the network immediately. Time is of the essence—ransomware often seeks to maximize damage by spreading across shared drives and cloud platforms. Disconnecting devices, disabling Wi-Fi and VPNs, and blocking access at the firewall level are essential measures to prevent further infection.Having a cybersecurity team on standby allows for experts to provide step-by-step guidance in real time, helping you make the right moves to contain the threat without destroying forensic evidence. Panic can lead to mistakes. Having a calm, expert-led approach ensures you stay focused and strategic.Step two: notify internal stakeholders and assemble your response teamRansomware response is not just an IT issue—it’s a business-wide challenge. Once containment is underway, inform key internal stakeholders, including executive leadership, legal, compliance, and communications teams. Appoint a central response lead, ideally from your crisis management team, who can coordinate efforts and make key decisions quickly.If you’ve already established an incident response plan, now is the time to activate it.Step three: secure backups and avoid engaging attackersIt may be tempting to click the ransom note or initiate contact with attackers to understand their demands. This is strongly advised against.Not only does it carry legal and ethical risks, but it may compromise your recovery options or make you more vulnerable to secondary attacks. Instead, secure all backups and logs. Identify when the attack began, which systems are affected, and what data may be at risk. This information will be crucial for both remediation and regulatory reporting.Having an expert partner will improve this process, by providing rapid forensic support to help assess the impact by identifying indicators of compromise (IOCs), tracing the attack vector, and determining the attacker’s dwell time. This information can also help you understand if data exfiltration occurred—an increasingly common element of modern ransomware.Step four: report the incident and consider legal obligationsDepending on your industry and location, you may have regulatory or legal requirements to report a ransomware incident. This could include notifying the Information Commissioner’s Office (ICO), your industry regulator, or affected third parties.It’s important not to delay these conversations. Having clear documentation and technical insights to back up your reporting will help this process run smoothly.Step five: begin recovery with expert guidanceOnce the ransomware is contained and systems are stabilized, it’s time to begin recovery. This involves more than just restoring files from backup. You must ensure the attacker’s access is removed, vulnerabilities are patched, and your environment is safe to bring back online.This is where a trusted partner makes all the difference. Incident response specialists will work alongside IT and cyber teams to validate clean systems, conduct a secure restoration, and put new protections in place. Your business shouldn’t just bounce back, it should come back stronger.Why speed and expertise matterThe damage caused by ransomware isn’t just financial—it’s operational, reputational, and often long-lasting. The quicker and more effectively you respond, the more you reduce the long-term impact.Cyber security firms offer different ways to ensure organizations are ready to face ransomware. This includes emergency incident response, where teams can rapidly deploy to help take control, contain the threat, and recover operations. Whether remote or on-site. Another option is to hold an incident response retainer, this is designed for preparedness. Retainer services give you guaranteed access to expert responders when you need them most. With predefined SLAs, threat intelligence, and environment familiarity, these tools can help businesses respond faster and more effectively.Prepare now, respond better laterThe first 24 hours of a ransomware attack are often chaotic - but they don’t have to be. With the right preparation and expert support, you can act swiftly, reduce damage, and return to normal operations with confidence. When minutes matter, experience is your strongest defense.We've featured the best encryption software.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-

Picture from static.independent.co.uk
Rank 67354 -

Picture from static.independent.co.uk
Rank 67355 -

Picture from static.independent.co.uk
Rank 67356 -

Picture from static.independent.co.uk
Rank 67357 -

Picture from static.independent.co.uk
Rank 67358 -

Picture from static.independent.co.uk
Rank 67359 -

Picture from static.independent.co.uk
Rank 67360 -

Picture from assets2.cbsnewsstatic.com
Rank 67361 -
Picture from assets3.cbsnewsstatic.com
Rank 67362 -

Picture from assets2.cbsnewsstatic.com
Rank 67363 -

Picture from image.cnbcfm.com
Rank 67364 -

Picture from static.independent.co.uk
Rank 67365 -
Picture from sc.cnbcfm.com
Rank 67366 -
Picture from cdn.mos.cms.futurecdn.net
Rank 67367It doesn't matter how large your organization is, you are at risk and sooner or later cyber criminals will try to attack you. It’s not a matter of whether your organization will face a security incident but when. That's why a robust incident response plan is crucial.So, what elements should your incident response plan include to be truly effective?The key components of an effective Incident Response PlanStructure: well-structured and straightforwardSimplicity and structure are your allies when creating an incident response plan. A complicated plan will only create confusion. Use charts, bullet points, and clear language to make it easily understandable.Utilizing templates and frameworksMany organizations opt to use established frameworks ISO standards as templates for their plans. These frameworks offer a structured approach, providing sections and subsections that cover all essential areas, from governance to technical responses. By using a recognized framework, you not only ensure completeness but also facilitate easier communication with external parties who may be familiar with the framework.Roles and responsibilities:Who's in Charge? An Incident Response Team (IRT), typically led by a Chief Information Security Officer (CISO), should be designated to take charge during an incident. The plan should also specify roles and responsibilities for each stakeholder, from IT personnel to legal advisors.Budget: allocate funds wiselyBudget considerations must be part of the planning process. Allocate sufficient funds for personnel, technologies, and training. This allocation should be proportional to the organization's size and risk profile.Small businesses might not have the same resources as larger corporations. A good incident response plan for a small business should be scaled to their specific needs, focusing on the most critical assets and functions. It should prioritize simplicity, clarity, and actionable steps that can be taken with limited cybersecurity personnel.Challenges in implementing an Incident Response Plan and how to overcome them? Whilst implementing an incident response plan, various challenges may arise. One example of this could be ensuring all team members are fully trained and understand their roles within the plan. Another challenge might be maintaining the plan's effectiveness over time. To overcome these challenges companies should enforce regular training sessions, continuous plan updates based on new threats and lessons learned from past incidents, and ensuring clear communication channels within the organization.Measuring the effectiveness of an Incident Response Plan? The effectiveness of an incident response plan can be measured through regular testing, such as tabletop exercises or live drills, to ensure team readiness. Additionally, metrics like the time to detect, respond to, and recover from incidents can provide insights into the plan's effectiveness. Continuous improvement based on these metrics and feedback from incident post-mortems is crucial for maintaining a robust incident response capability.Detection, reporting, and identification proceduresProactive Monitoring Systems - Your first line of defense is detecting an incident quickly. Invest in advanced monitoring systems and allocate personnel to supervise them round the clock.Reporting and identificationStreamline reporting protocols so that incidents can be rapidly identified and acted upon. Simplicity is key here, ensuring even the least technical person can report a problem.Communication strategies: internal and externalThe importance of good PRPublic Relations (PR) and your marketing team (if you have one) play a pivotal role in managing perceptions during an incident. Transparent, timely communication can mitigate panic, control misinformation, and maintain your organization's reputation.Internal communication flowInternal stakeholders need to be in the loop as well. Have a plan to keep everyone from top management to the frontline workers informed.External communication planCustomers, partners, suppliers, and sometimes the media will require timely and accurate updates. Your plan should specify who communicates this information, how, and when. A failure to report an incident to customers can land you in hot water with regulators and impact your reputation.Containment, eradication, and recovery guidelinesImmediate and long-term containmentAfter identifying an incident, containment is the first priority. Your plan should have procedures for immediate and long-term containment actions, such as isolating affected systems or updating security protocols.Eradication and recoveryThe plan must spell out how to find the root cause of an incident and eliminate it. It should also outline the steps to restore and validate system functionality for business operations to resume.Training, exercises, and cyber insurancePerforming cyber incident exercisesRegularly scheduled simulated attack scenarios help keep your team prepared and your strategy up to date. It’s crucial for identifying gaps in your plan and rectifying them.Some notable security testing services include penetration testing, red team testing, vulnerability assessments, and cyber security risk assessments.The role of cyber insuranceCyber insurance can be a lifesaver, covering costs that can range from legal fees to ransom payments. Your incident response plan should clearly state how and when to engage your cyber insurance coverage.Dos and don'ts: best practices and pitfallsDos- Train staff regularly- Update plans frequently- Communicate transparently- Analyze and learn from every incidentDon'ts- Ignore early warning signs- Underestimate the importance of employee training- Neglect to update stakeholders- Fail to adapt your strategy post-incidentThe role of training, simulations, and cyber insurance are also crucial. Remember, a good plan is dynamic, so always be ready to adapt and evolve. By incorporating these elements, your organization will not just be preparing for the worst-case scenario but also building a resilient and secure operational environment for the future.We've featured the best ransomware protection.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-
Picture from cdn.mos.cms.futurecdn.net
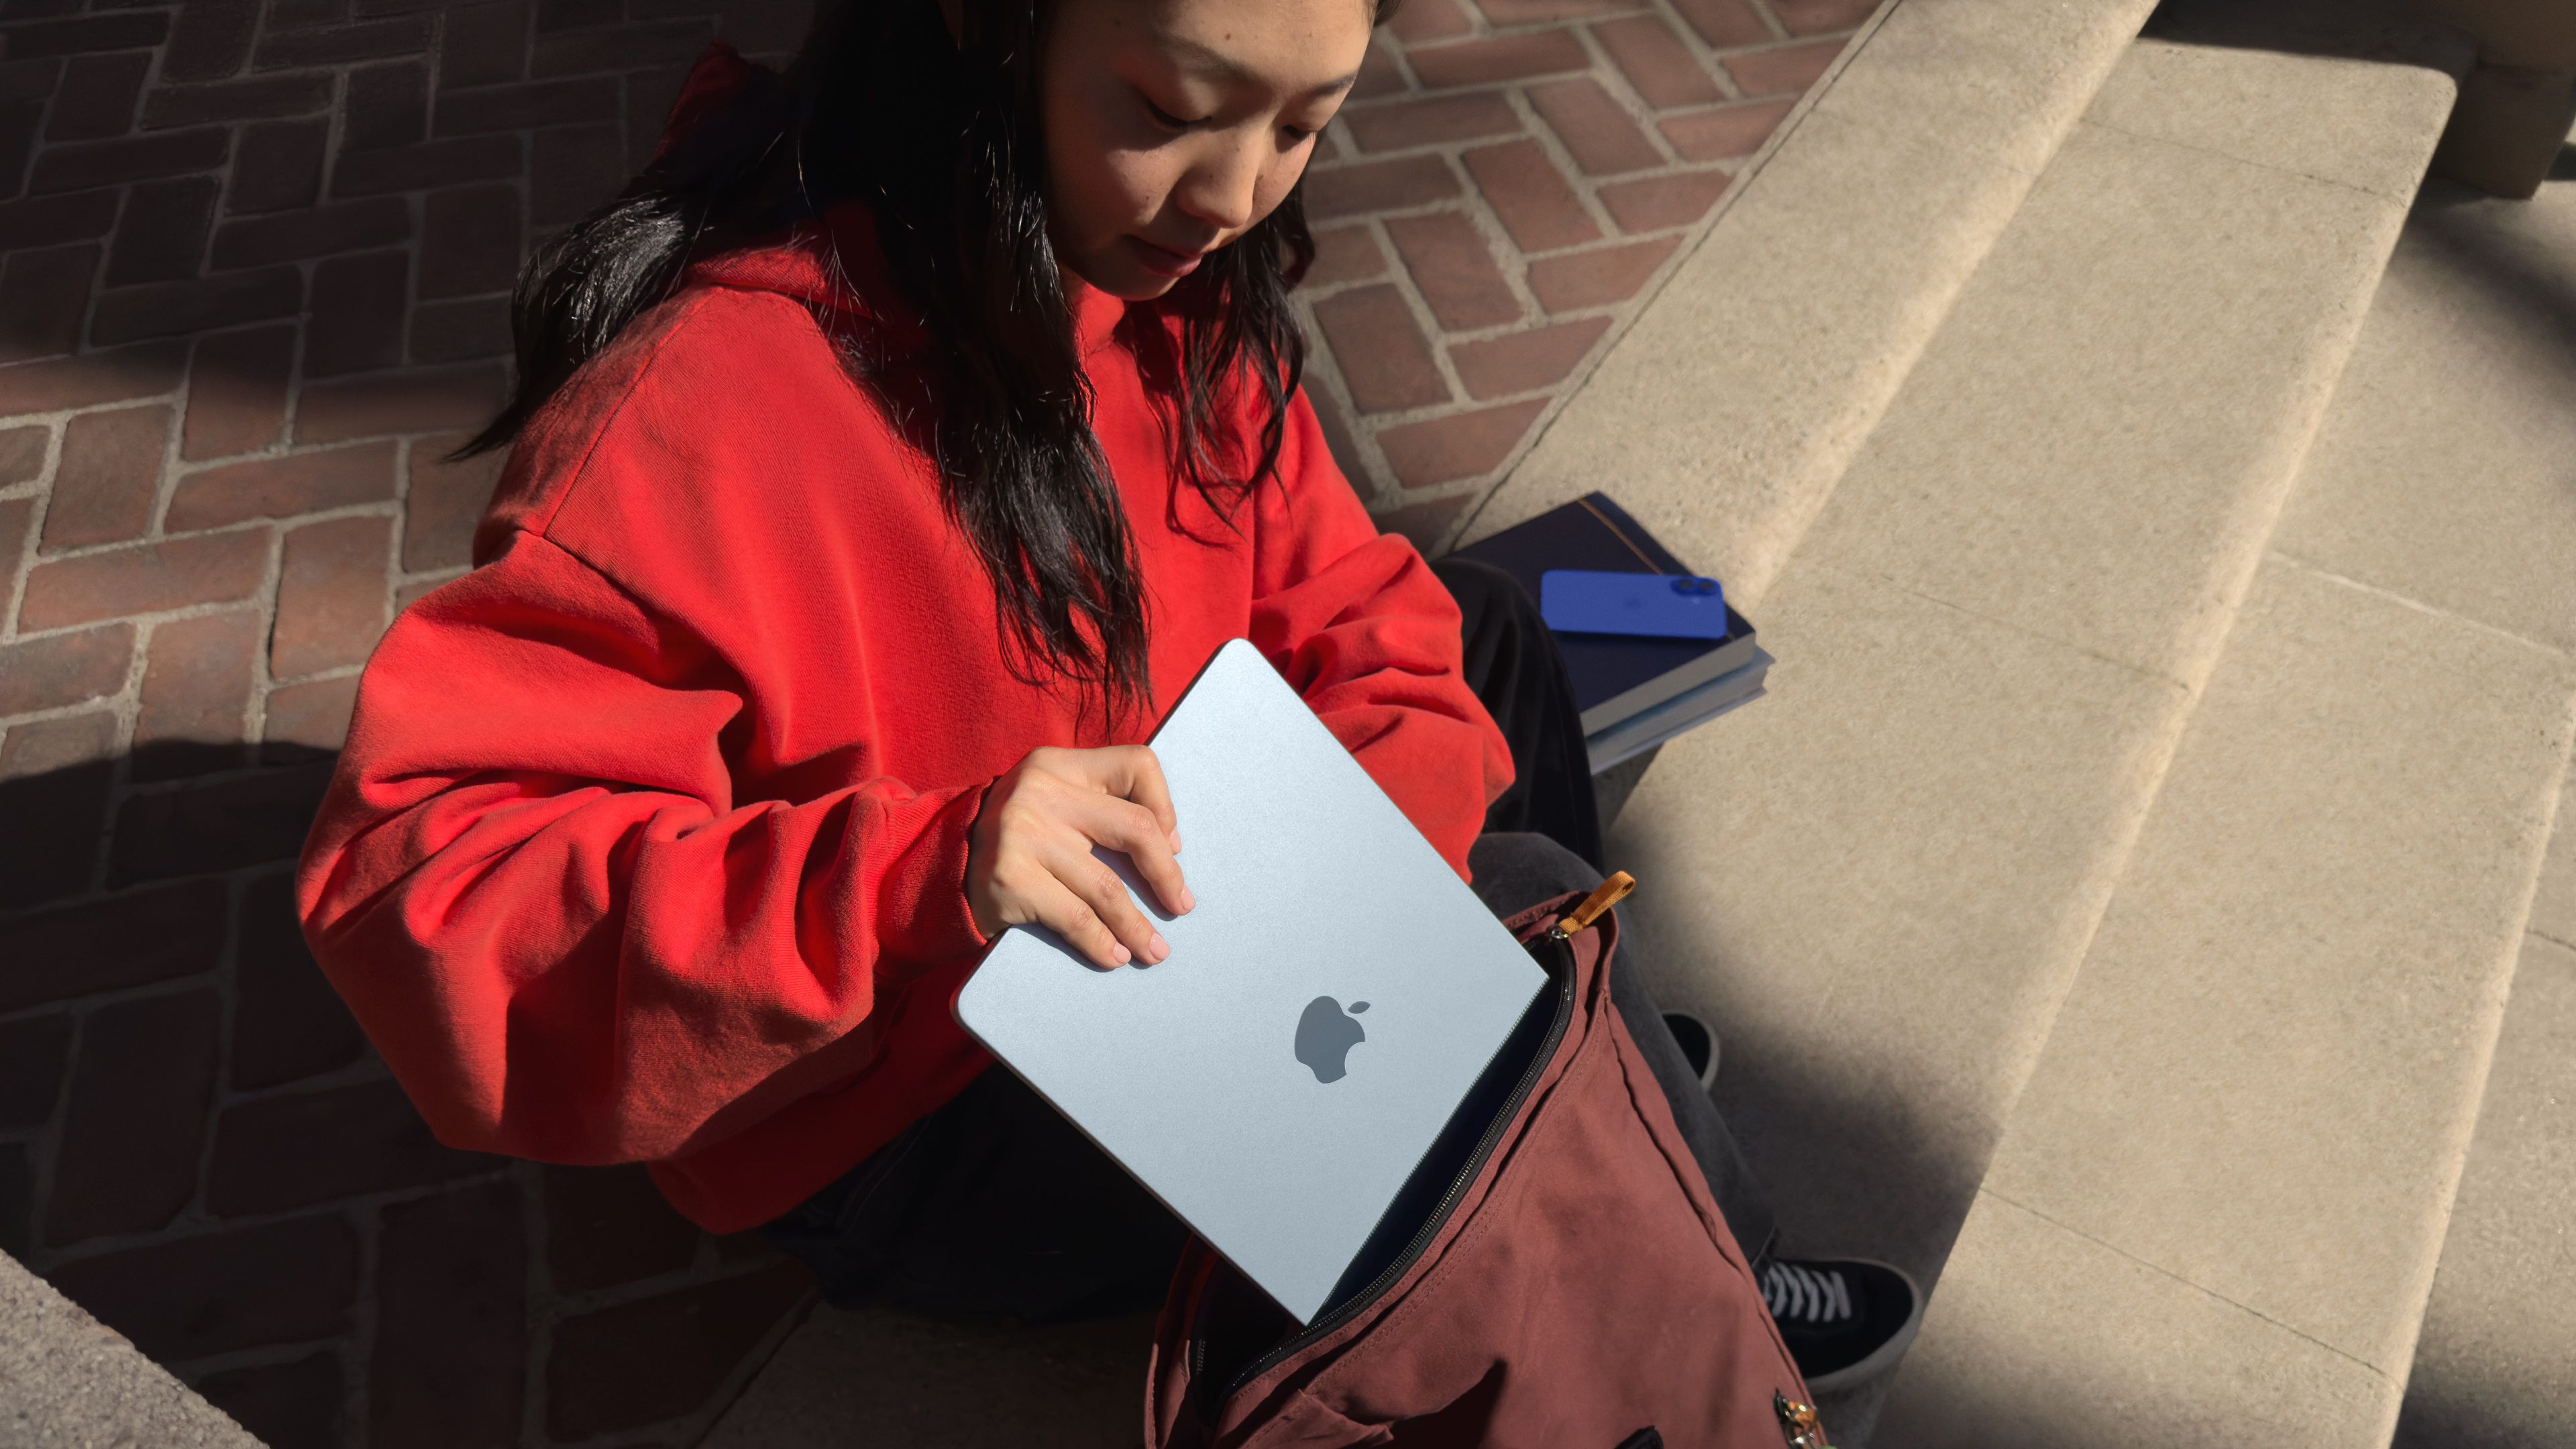
Rank 67368Apple could be working on a system to update Macs while they're still boxedThis is based on clues in the latest developer beta of macOS 26Such a system is already used with iPhones, though it's not clear how Apple would get this to work with MacsApple's Macs could leave the shelf with a fully up-to-date installation of macOS on board in the future, preventing any need for a day-one update from the buyer, if clues in the latest developer beta are any indication.9 to 5 Mac reports that the macOS Tahoe 26 beta 3 contains the groundwork (initial references and code) for such a system, which is already in place for the iPhone.It's called Presto and it allows boxed iPhones to be updated to the very latest version of iOS by retailers - without removing the hardware from its sealed package - if the devices need an update beyond the version of the operating system they shipped with.This saves the customer the trouble of applying an update right out of the gate, which is incredibly convenient.The Presto hardware itself is a rack with six bays that can have six iPhones placed within. It uses wireless technologies to switch the phones on, update them, then turn them off. (MagSafe and NFC to turn the devices on, by all accounts, and Wi-Fi to pipe the actual update through.)Analysis: Boxing clever(Image credit: Apple)If Macs are going to get the benefit of having fully up-to-date software when they're taken home by the buyer, it begs the question: how is Apple going to pull this off with laptops and PCs? The system might have to work very differently for a bigger piece of hardware, and Macs don't have NFC either - so it's not clear how the sealed PC could be triggered to power on in its box (and off again afterwards).9to5Mac suggests that maybe Apple could add NFC back to its macOS devices, or that perhaps a different mix of wireless tech could be used with Macs. Whatever the case, it's not clear how Apple would pull this off as it does with iPhones, but it may require a substantially different spin on the concept.Furthermore, just because a potential feature is spotted in the background of beta software doesn't mean it'll ever come to fruition. That said, the presence of the code here does indicate that this is at least something Apple is seriously considering - watch this space, I guess.You might also like...macOS Tahoe 26 - here's everything you need to know about all the new featuresNew Windows 11 update delivers a host of new features and fixes - here are 4 things I'm looking forward toNo, Windows 11 PCs aren't 'up to 2.3x faster' than Windows 10 devices, as Microsoft suggests – here's why that's an outlandish claim
-

Picture from techcrunch.com
Rank 67369 -

Picture from static.independent.co.uk
Rank 67370 -

Picture from static.independent.co.uk
Rank 67371 -

Picture from assets1.cbsnewsstatic.com
Rank 67372 -

Picture from assets2.cbsnewsstatic.com
Rank 67373 -

Picture from assets2.cbsnewsstatic.com
Rank 67374 -

Picture from assets2.cbsnewsstatic.com
Rank 67375 -

Picture from static.independent.co.uk
Rank 67376 -
Picture from static.independent.co.uk
Rank 67377 -

Picture from static.independent.co.uk
Rank 67378 -

Picture from static.independent.co.uk
Rank 67379 -

Picture from static.independent.co.uk
Rank 67380 -

Picture from static.independent.co.uk
Rank 67381 -

Picture from assets3.cbsnewsstatic.com
Rank 67382 -
Picture from ichef.bbci.co.uk
Rank 67383 -

Picture from ichef.bbci.co.uk
Rank 67384 -

Picture from static.independent.co.uk
Rank 67385 -

Picture from assets1.cbsnewsstatic.com
Rank 67386 -

Picture from image.cnbcfm.com
Rank 67387 -

Picture from static.independent.co.uk
Rank 67388 -

Picture from static.independent.co.uk
Rank 67389 -

Picture from static.independent.co.uk
Rank 67390 -
Picture from assets3.cbsnewsstatic.com
Rank 67391 -

Picture from assets1.cbsnewsstatic.com
Rank 67392 -

Picture from cdn.mos.cms.futurecdn.net
Rank 67393Apple TV+ has released the first trailer for The Morning Show season 4, which confirms that the hit workplace drama will return to the streaming service on September 17. While details of the new TV show are largely kept under wraps, we know there’s been a time jump since the season 3 ending, picking up after the UBA-NBN merger was finalized.After Bradley (Reese Witherspoon) turned herself into the FBI for concealing evidence about her brother’s actions on the January 6th insurrection, Alex (Jennifer Aniston) broke off her relationship with Paul (Jon Hamm) for having Bradley tailed in the lead-up to the season 3 finale. While their bond is strong, Alex and Bradley’s careers have never been further apart… and that sets us up for some riveting drama in season 4.As the trailer explains, new episodes will be focused on the “truth coming out”, and that means more tension behind the camera than there is in front. Frankly, that’s exactly the type of scandal we want to see, and one new character (blink and you’ll miss her) could well be at its beating heart.Marion Cotillard gets first look in The Morning Show season 4 trailerEnter Oscar winner and all-around incredible talent Marion Cotillard, who’s set to play Celine Dumont in The Morning Show season 4. You can catch her 48 seconds into the trailer, seen telling Alex through a glass window, “I like to know who’s an ally and who’s a liability.”All we know for certain is that Celine is a “savvy operator from a storied European family,” though it’s unclear if she’s friend or foe to Alex and Bradley. It almost doesn’t matter for two reasons: firstly, any bad blood is going to make amazing TV for us, and secondly, any time Cotillard is on screen is one to appreciate.If you were to ask me, Cotillard is one of those actresses who is supposedly beloved by Hollywood, but completely underutilised. After her Best Actress Academy Award win for playing Edith Piaf in La Vie en Rose in 2008, her career-defining leading roles have been few and far between. We had Inception in 2010, 2011’s Contagion and about a million Chanel perfume commercials, but her global reign ran undeservedly cold.The Morning Show has made a smart move with this casting, and fans are about to reap all the benefits. Beautifully toeing the line between seductive and mysterious, Cotillard’s suspense in any scene holds us in the palm of our hands. She’s as charismatic as she is aloof, all of which feeds into absolutely delicious merger drama in September. Basically, if you don’t know, get to know.As the weeks tick by in the meantime, we’re sure to be drip-fed tasty morsels of what we can expect from The Morning Show season 4 when it drops. In the meantime, I’ll be happy with the fantasy that Cotillard’s casting could change the game for good.You might also likeI'm delighted Slow Horses has been renewed for season 7, but now I'm worried about the future of my favorite Apple TV+ showAll the ways you can get an Apple TV+ free trial in 20253 new Apple TV+ shows you should stream in July 2025
-
Picture from static.independent.co.uk
Rank 67394 -
Picture from ichef.bbci.co.uk
Rank 67395 -
Picture from ichef.bbci.co.uk
Rank 67396 -

Picture from static.independent.co.uk
Rank 67397 -

Picture from static.independent.co.uk
Rank 67398 -
Picture from static.independent.co.uk
Rank 67399 -

Picture from assets2.cbsnewsstatic.com
Rank 67400