News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-
Picture from static.independent.co.uk
Rank 62651 -
Picture from cdn.mos.cms.futurecdn.net
Rank 62652Looking for a different day?A new NYT Connections puzzle appears at midnight each day for your time zone – which means that some people are always playing 'today's game' while others are playing 'yesterday's'. If you're looking for Thursday's puzzle instead then click here: NYT Connections hints and answers for Thursday, July 3 (game #753).Good morning! Let's play Connections, the NYT's clever word game that challenges you to group answers in various categories. It can be tough, so read on if you need Connections hints.What should you do once you've finished? Why, play some more word games of course. I've also got daily Strands hints and answers and Quordle hints and answers articles if you need help for those too, while Marc's Wordle today page covers the original viral word game.SPOILER WARNING: Information about NYT Connections today is below, so don't read on if you don't want to know the answers.NYT Connections today (game #754) - today's words(Image credit: New York Times)Today's NYT Connections words are…DRIVER LICENSELOUISIANATRENDYGREENLIGHTINDIANABRITISH MAGAZINEIDAHOINCHMUSICAL NOTEOKLAHOMALOS ANGELESFREUDIAN CONCEPTRECOGNIZEINSIDEMEDIOCRELANTHANUMNYT Connections today (game #754) - hint #1 - group hintsWhat are some clues for today's NYT Connections groups?YELLOW: The ego and the…GREEN: Not outBLUE: Do, Re, Mi, Fa, Sol…PURPLE: Universal shorthand for approvalNeed more clues?We're firmly in spoiler territory now, but read on if you want to know what the four theme answers are for today's NYT Connections puzzles…NYT Connections today (game #754) - hint #2 - group answersWhat are the answers for today's NYT Connections groups?YELLOW: WHAT “ID” MIGHT REFER TO:GREEN: WHAT “IN” MIGHT REFER TOBLUE: WHAT “LA” MIGHT REFER TOPURPLE: WHAT “OK” MIGHT REFER TORight, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON'T WANT TO SEE THEM.NYT Connections today (game #754) - the answers(Image credit: New York Times)The answers to today's Connections, game #754, are…YELLOW: WHAT “ID” MIGHT REFER TO DRIVER LICENSE, FREUDIAN CONCEPT, IDAHO, RECOGNIZEGREEN: WHAT “IN” MIGHT REFER TO INCH, INDIANA, INSIDE, TRENDYBLUE: WHAT “LA” MIGHT REFER TO LANTHANUM, LOS ANGELES, LOUISIANA, MUSICAL NOTEPURPLE: WHAT “OK” MIGHT REFER TO BRITISH MAGAZINE, GREENLIGHT, MEDIOCRE, OKLAHOMAMy rating: HardMy score: FailNo idea what was going on at all here. Let's start again tomorrow, eh?Okay, fair enough, you can spend a few minutes wallowing in my despair, because I was all at sea with today's Connections. None of the words seemed to have any connection at all and I was reduced to randomly placing words together in the blind hope that some might be correct.Reader, they were not – and I duly crashed out.That said, I do take some issue with this as a Connections puzzle, clever though it was. The groups are supposed to get easier – but that really wasn't the case here. All of them, from yellow to purple, are equally tough – there's no difficulty curve to it at all. Sure, throw in one or even two of these 'what a two-letter-word can mean' groups, but not four of them in one.But maybe that's just sour grapes on my part. Anyway, tomorrow will be easier, right? Right?How did you do today? Let me know in the comments below.Yesterday's NYT Connections answers (Thursday, July 3, game #753)YELLOW: CORRESPONDENCE CONTACT, DEALINGS, EXCHANGE, INTERACTIONGREEN: AIRPORT BOARD INFO ARRIVAL, DESTINATION, FLIGHT, GATEBLUE: PRO ATHLETE DATA COLLEGE, NUMBER, POSITION, TEAMPURPLE: FARMERS' THINGS ALMANAC, INSURANCE, MARKET, TANWhat is NYT Connections?NYT Connections is one of several increasingly popular word games made by the New York Times. It challenges you to find groups of four items that share something in common, and each group has a different difficulty level: green is easy, yellow a little harder, blue often quite tough and purple usually very difficult.On the plus side, you don't technically need to solve the final one, as you'll be able to answer that one by a process of elimination. What's more, you can make up to four mistakes, which gives you a little bit of breathing room.It's a little more involved than something like Wordle, however, and there are plenty of opportunities for the game to trip you up with tricks. For instance, watch out for homophones and other word games that could disguise the answers.It's playable for free via the NYT Games site on desktop or mobile.
-

Picture from ichef.bbci.co.uk
Rank 62653 -
Picture from static.independent.co.uk
Rank 62654 -
Picture from cdn.mos.cms.futurecdn.net
Rank 62655We’re living in a world of relentless uncertainty. For compliance teams, this uncertainty normally only means one thing - cybersecurity risk. Against this backdrop, you might think that the volatility of the global economic landscape would be the primary cause of compliance issues for firms this year. But does this environment in fact increase the danger of other risks?In March this year, our report gauged the opinions of 300 regulatory leaders from around the world on global trends involving market abuse and trade surveillance. One of the key findings was that the majority (64%) of regulatory professionals said cybersecurity risks were most likely to cause compliance issues in the next year. Next up was, unsurprisingly, global economic uncertainty (58%), followed by increasing regulatory complexity.Given that a lot has happened already this year, does this ranking remain the same? Or are other market drivers playing a bigger role than expected?The role of tech-driven risks AI, of course, lies at the heart of tech-driven risks. It has become both compliance’s enemy and ally. While AI trading models are designed to optimize for profit and increase efficiency, their rapidly accelerating sophistication means that they have the potential to become increasingly unpredictable. As AI-driven trading strategies interact with one another, market movements become harder to control and forecast. This is just one of the reasons why the benefits of AI tools also bring significant risks.These dangers explain why proprietary trading firms, who rely on high-frequency, algorithmic trading strategies, were especially concerned by tech-driven risks, with 70% of respondents picking it as a key issue for this year.Simultaneously, however, AI is becoming a great aide to compliance teams. Effective surveillance now depends on machine learning and AI to detect nuanced and initially obscure connections between instruments, firms or markets. These insights can support compliance professionals in detecting increasingly sophisticated forms of market abuse, while also reducing false positive alerts – a major resource-drain on monitoring teams.Of course tech-driven risks aren’t just limited to AI. Off-channel electronic communications (eComms), where employees communicate via unmonitored apps like WhatsApp or Signal, present major compliance risks, while the increase in regulatory clarity around digital assets, such as the second part of EU’s MiCA regulation which came into force in December 2024, means their journey towards the mainstream is only likely to accelerate.What’s true, however, is that global uncertainty heightens these risks.How global unpredictability aligns with increasing regulatory action Global economic unpredictability has undoubtedly been the story of 2025 so far. US trade tariffs, geopolitical conflicts, supply chain disruption and economic volatility have created a trading environment where the next move can be impossible to ascertain. But it’s also the case that this uncertainty is becoming more accepted, with regulators and firms adapting to ensure they are set up to withstand any unexpected twists and turns in the market.So how do firms mitigate against this uncertainty from a regulatory perspective? One approach is to ensure you have stringent and robust trade surveillance controls in place. Over the last few years, instead of predominantly levying fines for abuse, regulators have been focusing on insufficient eComms recordkeeping and trade surveillance systems and controls.Our report illustrated how trade and eComms surveillance fines accounted for over three quarters ($1.4 billion) of total enforcement action in 2024. There has also been a widening of who global regulators have been targeting, with firms of all sizes – not just the tier one banks – being handed stiff financial penalties.Why robust trade surveillance controls underpin compliance Some events are impossible to predict. Global uncertainty is always a factor, so robust controls are needed to mitigate risk and maintain compliance. Current compliance technology is already advancing to manage this rising range of risks, with features such as conditional parameters that can adapt to market volatility and liquidity, or sandbox environments to test new configurations in a controlled, low-risk setting. These developments are a crucial step in building systems that can respond to the complexities of risk in today’s markets and ensure firms can keep on top of regulatory requirements.With eComms and trade surveillance coming under particularly intense regulatory scrutiny, the compliance strategies that integrate trade and eComms data together are the ones best placed to manage risks this year. While trade data offers quantifiable evidence of suspicious activity, the intent behind it often lies in communications data. By adopting such an integrated approach, compliance teams can spot abuse that might not otherwise be apparent and build comprehensive cases.Controlling the uncontrollable It’s too early to call what risks are causing the most compliance issues this year. But there is no question the three areas highlighted by regulatory professionals in our report align with the current compliance reality. Rather than weighting one risk above another, however, what compliance strategy calls for more and more is the need for an integrated and holistic approach that accounts for the relationships between these risks.Of course, it is necessary to have an awareness of what risks are a particular problem at a given time. But an integrated approach can bring to light risks that would otherwise remain hidden. Above all, what it comes down to is control: when outside events are deeply unpredictable, regulatory processes and systems that are robust, well designed and executed efficiently are worth their weight in gold.We list the best IT Automation software.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-

Picture from static.independent.co.uk
Rank 62656 -

Picture from static.independent.co.uk
Rank 62657 -

Picture from static.independent.co.uk
Rank 62658 -

Picture from static.independent.co.uk
Rank 62659 -

Picture from static.independent.co.uk
Rank 62660 -

Picture from static.independent.co.uk
Rank 62661 -

Picture from static.independent.co.uk
Rank 62662 -

Picture from static.independent.co.uk
Rank 62663 -
Picture from assets3.cbsnewsstatic.com
Rank 62664 -

Picture from assets1.cbsnewsstatic.com
Rank 62665 -

Picture from assets2.cbsnewsstatic.com
Rank 62666 -

Picture from cdn.mos.cms.futurecdn.net
Rank 62667EA is taking Anthem offline permanently in JanuaryThe online-only game will be taken off EA Play next monthPremium currency is also unavailable to purchase as of nowBioware's third-person shooter Anthem is the latest in a long line of online-only games to receive a death sentence, as publisher EA will be taking the game offline next year.As reported by IGN, Anthem will effectively cease to exist on January 12, 2026, when the game's server will be taken offline. Anthem requires an online connection to play, meaning this will render the game permanently unplayable.As of right now, EA has removed the ability to purchase premium currency in the game, and it's scheduled to be delisted from EA Play next month, on August 15. Players who already own the game - or who purchased it before that August date - will still get to play it before its closure in January.While EA insists its decision to shelve Anthem didn't incur any job cuts, the company did lay off an unspecified number of Bioware staff back in January, including several veteran Dragon Age series developers. This was, apparently, a decision made in order to refocus efforts on the upcoming Mass Effect game.Anthem was never the stone-cold success EA perhaps wanted it to be, with much critique levied at its bland story and repetitive gameplay. But as an always-online PvE shooter outside of the MMORPG space, it was arguably one of the first of its kind when it launched back in 2019. Though it's fair to say it was already being overlooked in favor of popular multiplayer games like Destiny 2, Overwatch, and, of course, Fortnite.Also check out...PS5 hit Helldivers 2 makes history as the first PlayStation-published game to get an Xbox releaseRomero Games has lost funding for its next, unannounced game, with one staffer claiming the 'whole studio' has been laid off due to Microsoft cutsPhil Spencer somehow thinks that Xbox has 'never looked stronger' as multiple games are canceled
-

Picture from static.independent.co.uk
Rank 62668 -

Picture from static.independent.co.uk
Rank 62669 -

Picture from static.independent.co.uk
Rank 62670 -
Picture from ichef.bbci.co.uk
Rank 62671 -
Picture from cdn.mos.cms.futurecdn.net
Rank 62672Three zero-day flaws in Ivanti CSA solutions were abused to grab login credentialsThe group likely sold the access to French government devicesResearchers are attributing the attacks to Chinese state-sponsored miscreantsIn late 2024, Chinese state-sponsored threat actors abused multiple zero-day vulnerabilities in Ivanti Cloud Services Appliance (CSA) devices to access French government agencies, as well as numerous commercial entities such as telcos, finance, and transportation organizations.The news was recently confirmed by the French National Agency for the Security of Information Systems (ANSSI), which noted threat actors were abusing three security vulnerabilities in Ivanti CSA devices: CVE-2024-8963, CVE-2024-9380, and CVE-2024-8190.All three were zero-days at the time, and all were used to steal login credentials and establish persistence on target endpoints. Apparently, the miscreants were deploying PHP web shells, modifying existing PHP scripts to inject web shell capabilities, and installing kernel modules that served as a rootkit.Get 55% off Incogni's Data Removal service with code TECHRADAR Wipe your personal data off the internet with the Incogni data removal service. Stop identity thievesand protect your privacy from unwanted spam and scam calls.View DealSelling accessThe attacks were attributed to a group tracked as Houken which, in the past, was seen actively exploiting vulnerabilities in SAP NetWeaver to drop a variant of GoReShell backdoors called GOREVERSE.This group, the researchers claim, bears many similarities to an entity tracked by Google’s Mandiant team as UNC5174."While its operators use zero-day vulnerabilities and a sophisticated rootkit, they also leverage a wide number of open-source tools mostly crafted by Chinese-speaking developers," French researchers said. "Houken's attack infrastructure is made up of diverse elements -- including commercial VPNs and dedicated servers."Apparently, Houken isn’t exclusively focused on western targets. In the past, it was observed targeting a wide range of government and education organizations in Southeast Asia, China, Hong Kong, and Macau.For Western targets, they were mostly focused on government, defense, education, media, and telecommunications.It is also worth mentioning that in the French case, it is likely that there were multiple threat actors involved, with one group acting as an initial access broker, and a separate group purchasing that access to hunt for valuable intelligence and other sensitive data.Via The Hacker NewsYou might also likeCritical Ivanti Cloud Service Appliance flaw exploited in the wildTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-
Picture from ichef.bbci.co.uk
Rank 62673 -

Picture from ichef.bbci.co.uk
Rank 62674 -
Picture from static.independent.co.uk
Rank 62675 -

Picture from static.independent.co.uk
Rank 62676 -

Picture from static.independent.co.uk
Rank 62677 -
Picture from assets3.cbsnewsstatic.com
Rank 62678 -
Picture from static.files.bbci.co.uk
Rank 62679 -

Picture from static.independent.co.uk
Rank 62680 -

Picture from static.independent.co.uk
Rank 62681 -

Picture from static.independent.co.uk
Rank 62682 -

Picture from static.independent.co.uk
Rank 62683 -

Picture from static.independent.co.uk
Rank 62684 -

Picture from static.independent.co.uk
Rank 62685 -
Picture from cdn.mos.cms.futurecdn.net
Rank 62686Okta warns GenAI tool v0.dev is being exploited to build phishing sitesThe malicious sites are being hosted on Vercel infrastructure to appear more legitimateAI tools are also commonly citing false URLs, putting unsuspecting users at risk of attacksNew Okta research has revealed how threat actors are using Vercel's v0.dev to build realistic phishing sites which mimic legitimate sign-in pages, with researchers successful reproducing the alleged technique to prove its feasibility.v0.dev allows users to create web interfaces from simple, natural language prompts, which researchers say is concerning because the technology has now been proven to lower the technical barrier for phishing attacks and other types of cybercrime.Although Vercel and Okta have worked together to restrict access to known sites, many argue there's very little that can be done to prevent such attacks now AI tools have become so widespread.GenAI is now creating phishing sitesOkta found the fake phishing sites to be impersonating company logos and other assets to reduce detection by unsuspecting victims, with the sites hosted on Vercel's infrastructure to appear more legitimate. Microsoft 365 and fake crypto sites were among the most popular.The open source availability of v0.dev clones and guides on GitHub has also broadened access to these capabilities for less experienced developers and attackers.Okta is recommending that all users set up multi-factor authentication on supported accounts, binding authenticators to original domains via tools like Okta FastPass to ensure that fake sites don't get access to your credentials."Organizations can no longer rely on teaching users how to identify suspicious phishing sites based on imperfect imitation of legitimate services," Okta's researchers noted.Companies should also update their cybersecurity training programs to address risks from AI-generated phishing attacks and social engineering.The news comes soon after another report revealed around one-third of GenAI chatbot responses containing login URLs were false, with attackers registering false domains that are cited by tools like ChatGPT to establish their own phishing campaigns.You might also likeProtect your digital footprint by installing the best VPNsConsider using the best password managers and best authenticator appsAI is making phishing emails far more convincing with fewer typos and better formatting: Here's how to stay safe
-

Picture from static.independent.co.uk
Rank 62687 -

Picture from static.independent.co.uk
Rank 62688 -

Picture from static.independent.co.uk
Rank 62689 -
Picture from ichef.bbci.co.uk
Rank 62690 -

Picture from static.independent.co.uk
Rank 62691 -

Picture from static.independent.co.uk
Rank 62692 -

Picture from static.independent.co.uk
Rank 62693 -
Picture from cdn.mos.cms.futurecdn.net
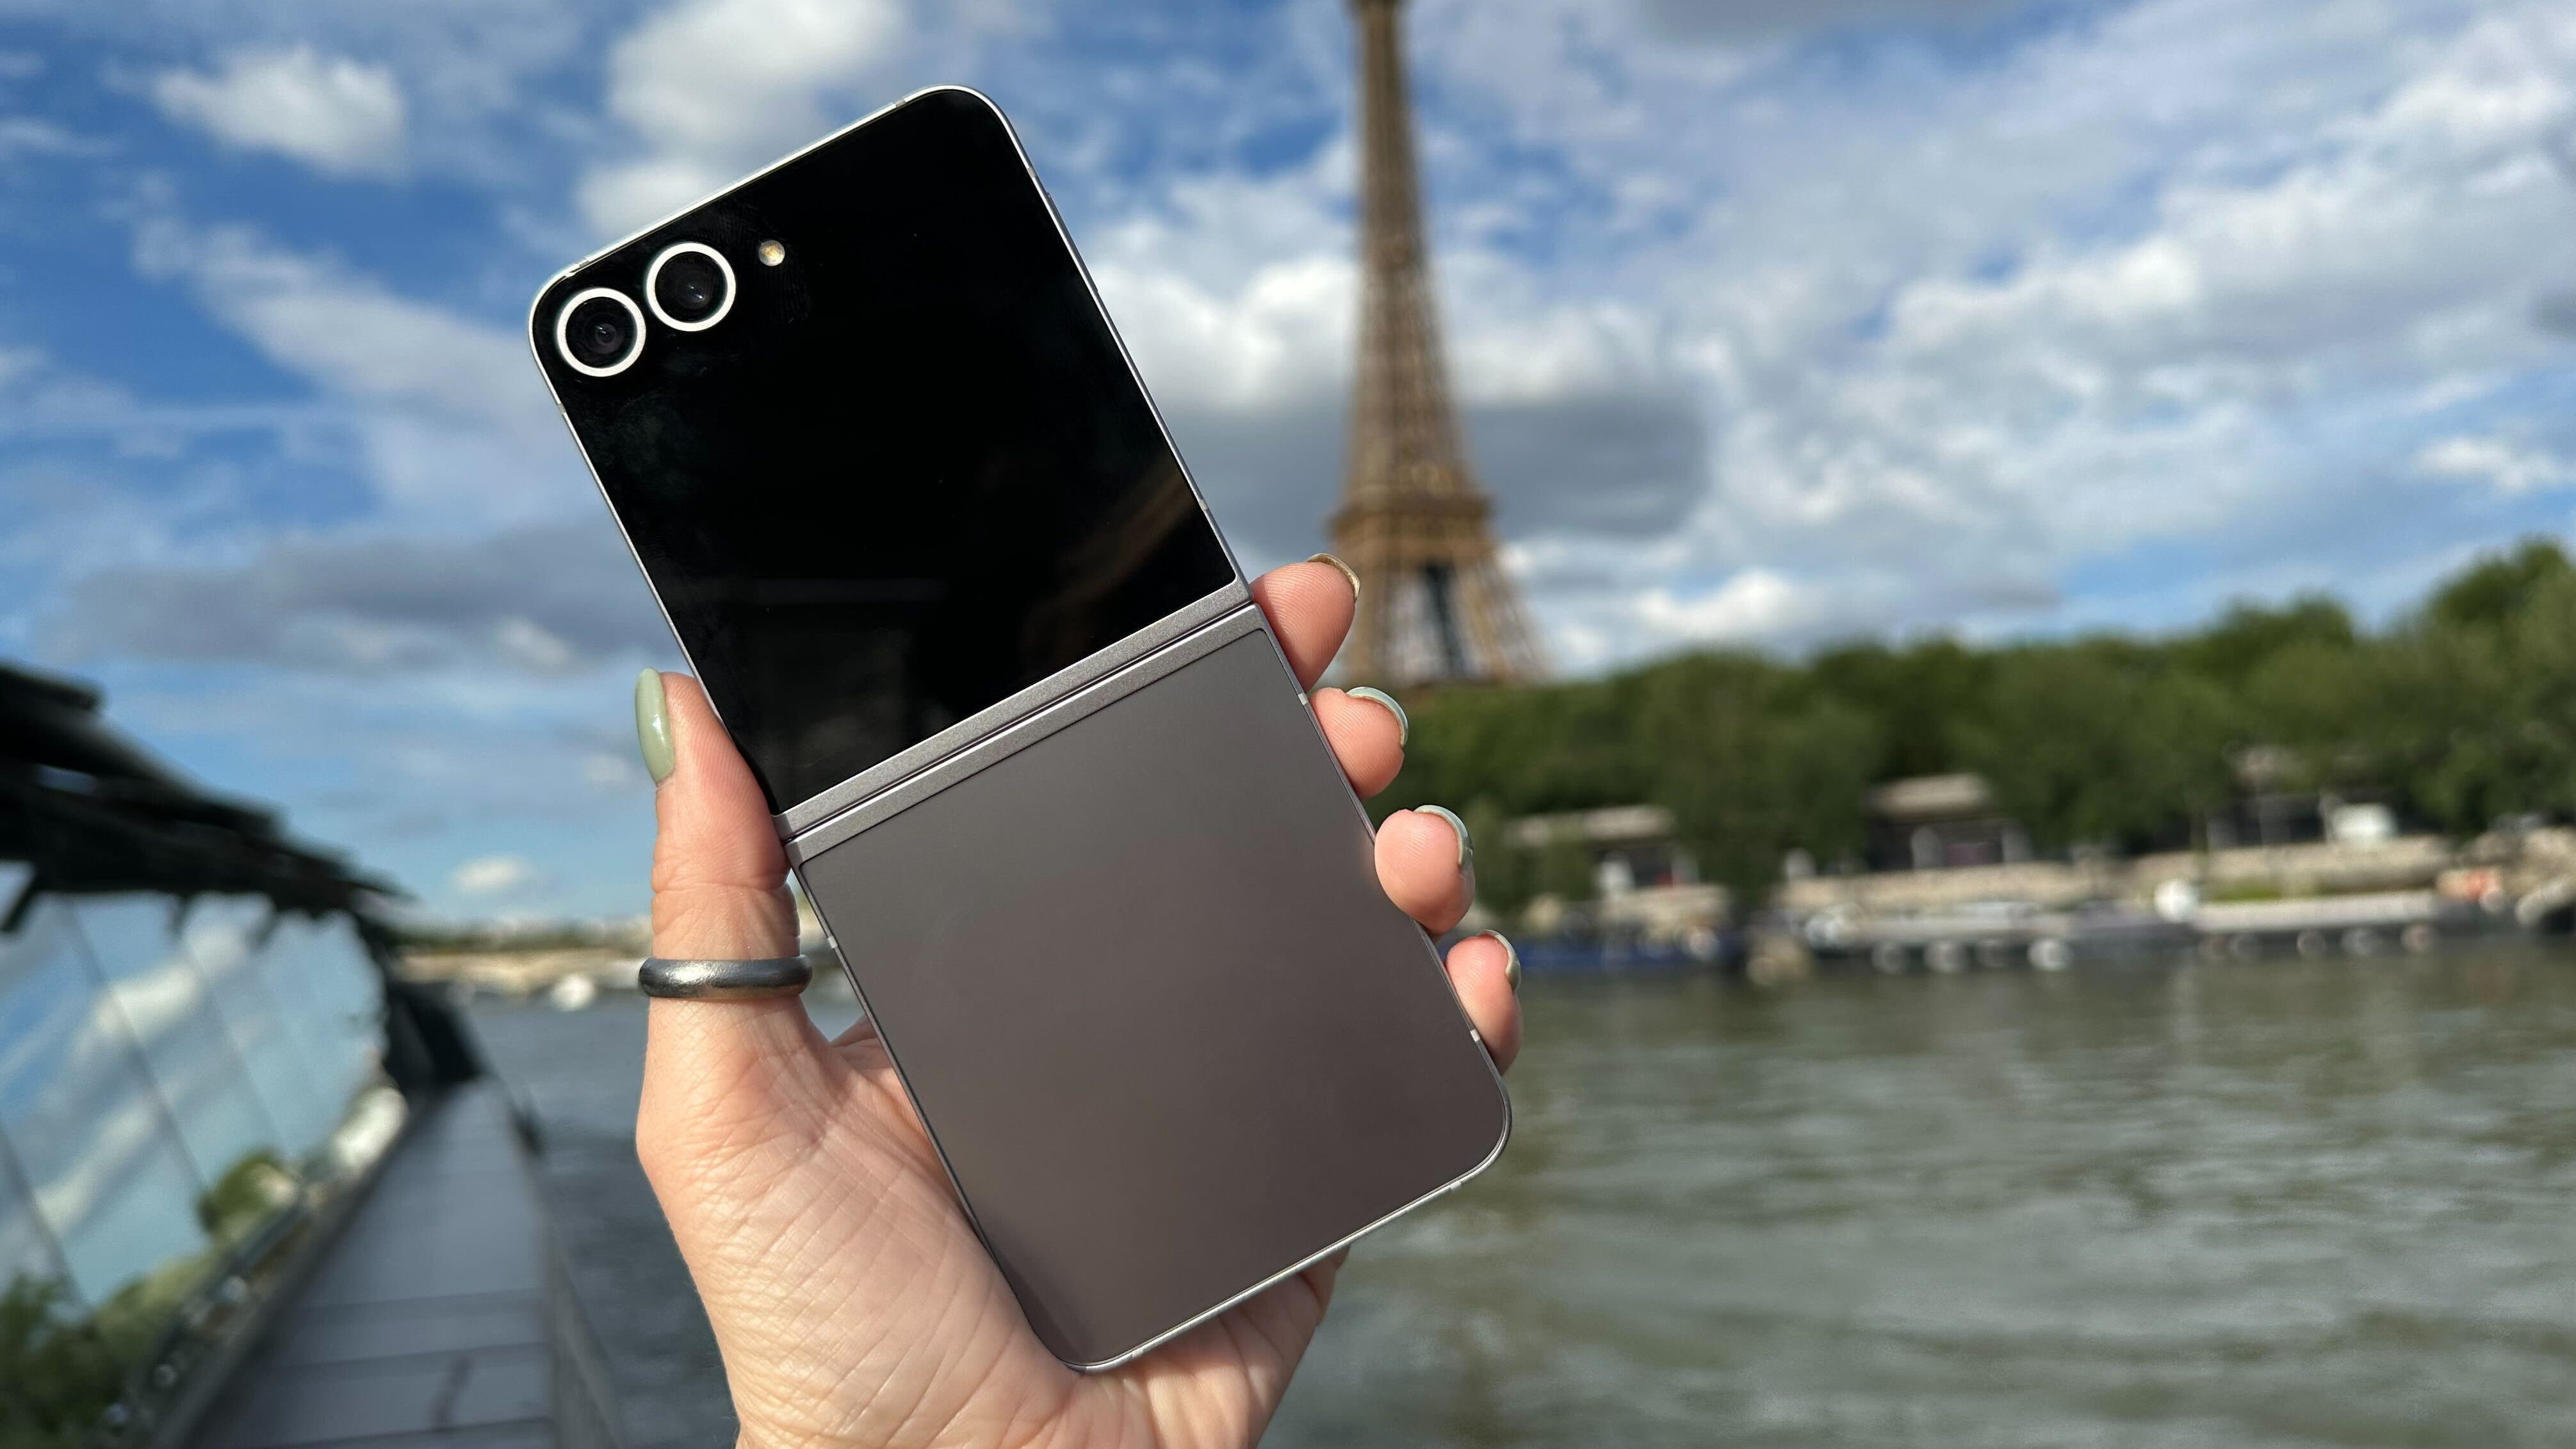
Rank 62694Samsung has accidentally revealed storage and RAM amounts for the Galaxy Z Fold 7, Galaxy Z Flip 7, and Z Flip 7 FEThe Galaxy Z Fold 7 will seemingly come with more RAM than its predecessor in the top configurationA leak has also shown off some Z Fold 7 and Z Flip 7 cases, some of which have magnetsDespite Samsung’s best efforts to stop them, phone leaks are inevitable, but usually, it’s leakers intentionally sharing details rather than the manufacturer accidentally doing so.In the case of the Samsung Galaxy Z Flip 7 and Samsung Galaxy Z Fold 7, though, we’ve now encountered two accidental leaks from Samsung itself.The first was the sharing of some colors on Samsung’s Irish website, and now leaker Roland Quandt has spotted a terms and conditions document on a Turkish Samsung site, which mentions RAM amounts and storage capacities for these upcoming phones.The document states that the Galaxy Z Fold 7 comes with 12GB of RAM paired with either 256GB or 512GB of storage, and that there's also a 16GB version with 1TB of storage. Those storage capacities are the same as the Samsung Galaxy Z Fold 6, but in all cases, that phone comes with 12GB of RAM, so at the top end, you should be able to get more with the Z Fold 7.The Flip 7 and the Flip 7 FENext up, the Samsung Galaxy Z Flip 7 is listed as having 12GB of RAM and a choice of either 256GB or 512GB of storage. Those are the same specs as the Samsung Galaxy Z Flip 6.There are also Galaxy Z Flip 7 FE specs listed here, with the phone said to have 8GB of RAM and come in a choice of 128GB or 256GB of storage.Since this all comes directly from a Samsung site, these details are almost certainly accurate, but we still can’t be 100% certain until Samsung announces the specs on July 9 – and it’s possible, too, that some regions will have different configurations to others.Magnetic charging could require a caseA Samsung Galaxy Z Flip 7 case with magnets built in (Image credit: Android Headlines)In any case, we’ve also now seen leaked case renders for the Galaxy Z Flip 7 (shared by Android Headlines) and Galaxy Z Fold 7 (shared by NieuweMobiel).These don’t reveal much about the phones that we haven’t already seen or heard, but it’s worth noting that some of the cases include magnets, which means that these phones will probably both have the same magnetic charging support as the Samsung Galaxy S25 series.Specifically, you’ll probably be able to magnetically attach chargers and other accessories, much like with Apple’s MagSafe system, except the magnets won’t be built into the phones themselves, so you’ll need to equip them with a magnetic case first. If so, that would be disappointing but not surprising.Samsung is expected to unveil all of these phones at the next Galaxy Unpacked on July 9, so we should find out exactly what they have to offer very soon.You might also likeHow to watch Samsung Galaxy Unpacked on July 9: get ready for new foldable phones and moreGorgeous leaked photos give us our best look yet at the super-slim Samsung Galaxy Z Fold 7A massive new Samsung Galaxy Z Fold 7 and Z Flip 7 leak suggests we could see some serious upgrades at next week's Unpacked
-

Picture from static.independent.co.uk
Rank 62695 -
Picture from cdn.mos.cms.futurecdn.net
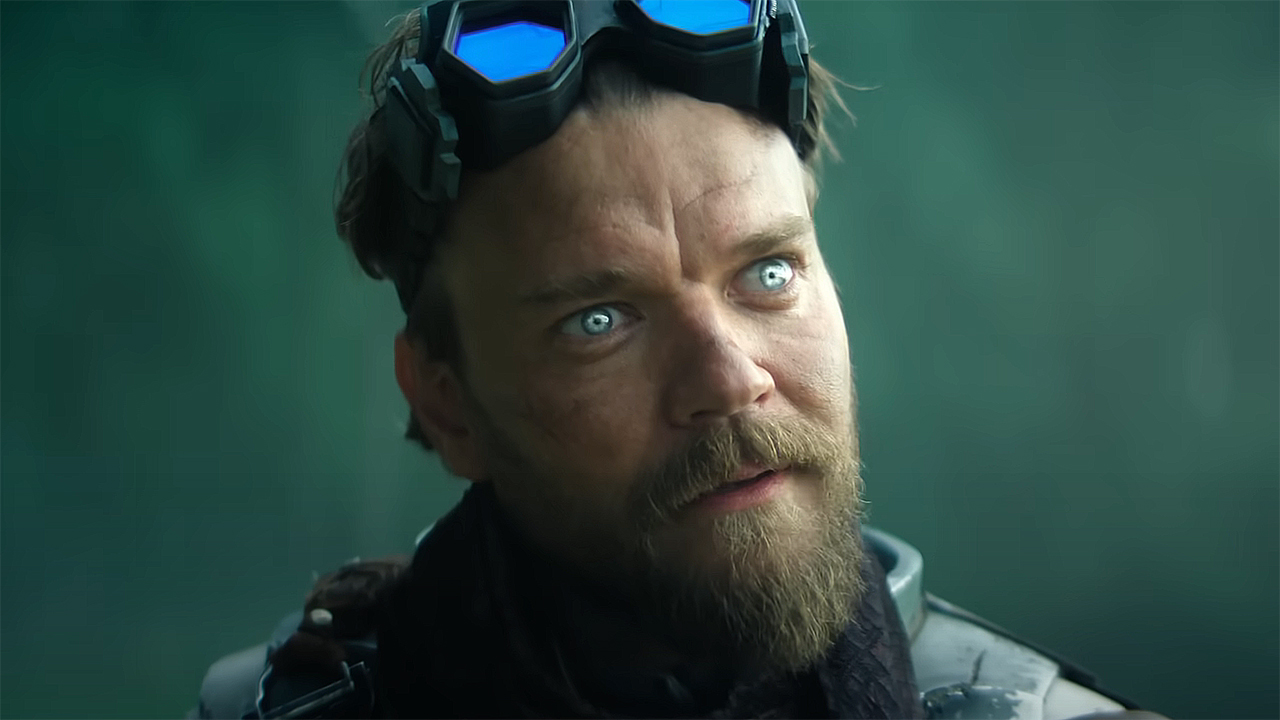
Rank 62696Pilou Asbaek has outlined what fans can expect from his villain in Foundation season 3The Mule is an incredibly powerful antagonist who threatens Empire and The FoundationThe series newcomer has also revealed why it's so fun to play villainous charactersFoundation season 3 will introduce the show's most terrifying villain yet in The Mule – and Pilou Asbaek has teased what viewers can expect from his take on the fan-favorite antagonist.Speaking to TechRadar ahead of Foundation's return on July 11, Asbaek revealed his version of the character will be something of a departure from how he's depicted in Isaac Asimov's book series namesake.In Asimov's best-selling novels, The Mule is a weedy individual who proves looks can be deceiving. Indeed, The Mule is one of the most powerful Mentalics – humans who possess incredibly potent psychic abilities – to ever live in Asimov's fictional universe. Due to his weak appearance, he's constantly underestimated by his foes, which allows him to conquer vast swathes of the galaxy before The Imperium or The Foundation can muster a response to the growing threat he poses.The Mule retains his telepathic superpowers in Apple's live-action adaptation. But, as Foundation season 3's official trailer revealed, he's a far more physically imposing character than he's presented in the books.The Mule is the most dangerous antagonist we've seen in Foundation so far (Image credit: Apple TV+)"He needs to be a big, immediate threat to Empire and The Foundation," Asbaek told me of the decision to make The Mule taller and more muscular in the Apple TV+ space opera. "So, he's physically different. He's a pretty big, wide guy who's also more roguish, brutish, and impolite than he's described in Asimov's brilliant books."The Mule's altered build is less of a surprise when you think back to last season. As I covered in my Foundation season 2 ending explained piece, The Mule makes a brief cameo before the finale's end credits sequence rolls. The unhinged villain, who was played in that scene by Mikael Persbrandt before he was replaced by Asbaek as part of a season 3 cast shake-up, was similarly tall in stature. So, there's some continuity between Persbrandt and Asbaek's iterations of the character from a physicality perspective.Nevertheless, Asbaek is well aware that some long-time fans of Asimov's literary works might take exception to how The Mule is depicted in one of the best Apple TV+ shows. Perhaps unsurprisingly, he's already prepared himself for any potential backlash."I've done a few adaptations – Ghost in the Shell and Game of Thrones (GoT), for example – so I've been down that path," he mused. "I know that some people will like it [my take on The Mule] and some won't, but it's my job to make the best possible version in collaboration with the creative team."I didn't know Mikael had done it, but I knew of the show and what I wanted to bring to the character," he added. "It's the same thing as someone doing an adaptation of a Shakespearean play. We've seen a million different versions of Hamlet, so this is just my interpretation of The Mule."As for how The Mule differs from GoT's Euron Greyjoy, the unlikeable and power-hungry character that Asbaek played in one of the best HBO Max shows, or any other villain he's played, Asbaek said: "He's probably the most human one I've ever played. He's got the biggest storyline I've had with playing a villain, but he's also the most chaotic, tortured soul of of them all. I'm not going to spoil it, but I can say you'll get a sense of why [that's the case]."At the end of the day, he's just a little boy who wants to be loved," Asbaek continued. "I was very inspired by French novel 'The Little Prince'. That's also the reason why he [The Mule] wears a red coat, because I wanted to look like the Little Prince, who comes to our world because he wants to know what it is to be human and have emotions. That's the only thing that The Mule doesn't have. He's one of a kind and, throughout this season, you'll find out what happens when he doesn't get what he wants."Are you excited to see Asbaek as The Mule? Let me know in the comments. And, before the sci-fi epic's next installment arrives, read my Foundation season 3 review to see if it's better than its predecessors.You might also like'We're the last to find out': Foundation stars don't know if it'll return for season 4 – but they haven't given up hope for the Apple TV+ show's renewalPrime Video users, rejoice! Save big on Apple TV+ and watch these 4 shows with 85% or higher Rotten Tomatoes scores using this Amazon add-on dealThese are the best Apple TV+ movies to watch today
-
Picture from cdn.mos.cms.futurecdn.net
Rank 62697Hunters International struck many private and public entities, including Tata and Telecom Namibia The group says it is disbanding "in light of recent events"It even released decryption keys for their victimsA major ransomware operation has announced a complete shutdown and the public release of decryption keys - however, some are skeptical that this is the last we’ve seen of this particular group.The operators, known as Hunters International, published a short announcement on their dark web site, notifying their followers, affiliates, and the wider cybercriminal community, that they will no longer operate.“After careful consideration and in light of recent developments, we have decided to close the Hunters International project,” the announcement reads. “This decision was not made lightly, and we recognize the impact it has on the organizations we have interacted with.”Get 55% off Incogni's Data Removal service with code TECHRADAR Wipe your personal data off the internet with the Incogni data removal service. Stop identity thievesand protect your privacy from unwanted spam and scam calls.View DealCallback phishingWhile the group mentions “recent developments”, it doesn’t elaborate, so we don’t know if this means they were seized by law enforcement, or they simply extorted enough money to call it quits.TechCrunch, on the other hand, believes there could be a third option - a smoke-and-mirrors effort to throw the police off. Discussing the matter with threat intelligence analyst from Recorded Future, Allan Liska, TechCrunch learned the group might be rebranding to World Leaks.“I think this is more of a ‘cutting of ties’ with the old infrastructure,” Liska told the publication. This wouldn’t be the first group that rebranded to try and hide their tracks.After the Colonial Pipeline attack, DarkSide, rebranded into BlackMatter, and later Alphv/BlackCat, and REvil (Sodinokibi) was preceded by GandCrab.As for releasing decryption keys, while commendable, it doesn’t mean much for the attackers, Liska argues. These are mostly older victims who had no intention of paying anyway, so for the group - nothing was lost.“As far as releasing decryption keys, at this point they aren’t likely to make any money from any Hunters’ victims who are still out there, so they probably see it as a gesture that doesn’t really cost them anything,” Liska concluded.You might also likeAmerica is the top source of spam, and it’s getting worse thanks to growing data center infrastructureTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-

Picture from ichef.bbci.co.uk
Rank 62698 -

Picture from static.independent.co.uk
Rank 62699 -
Picture from cdn.mos.cms.futurecdn.net
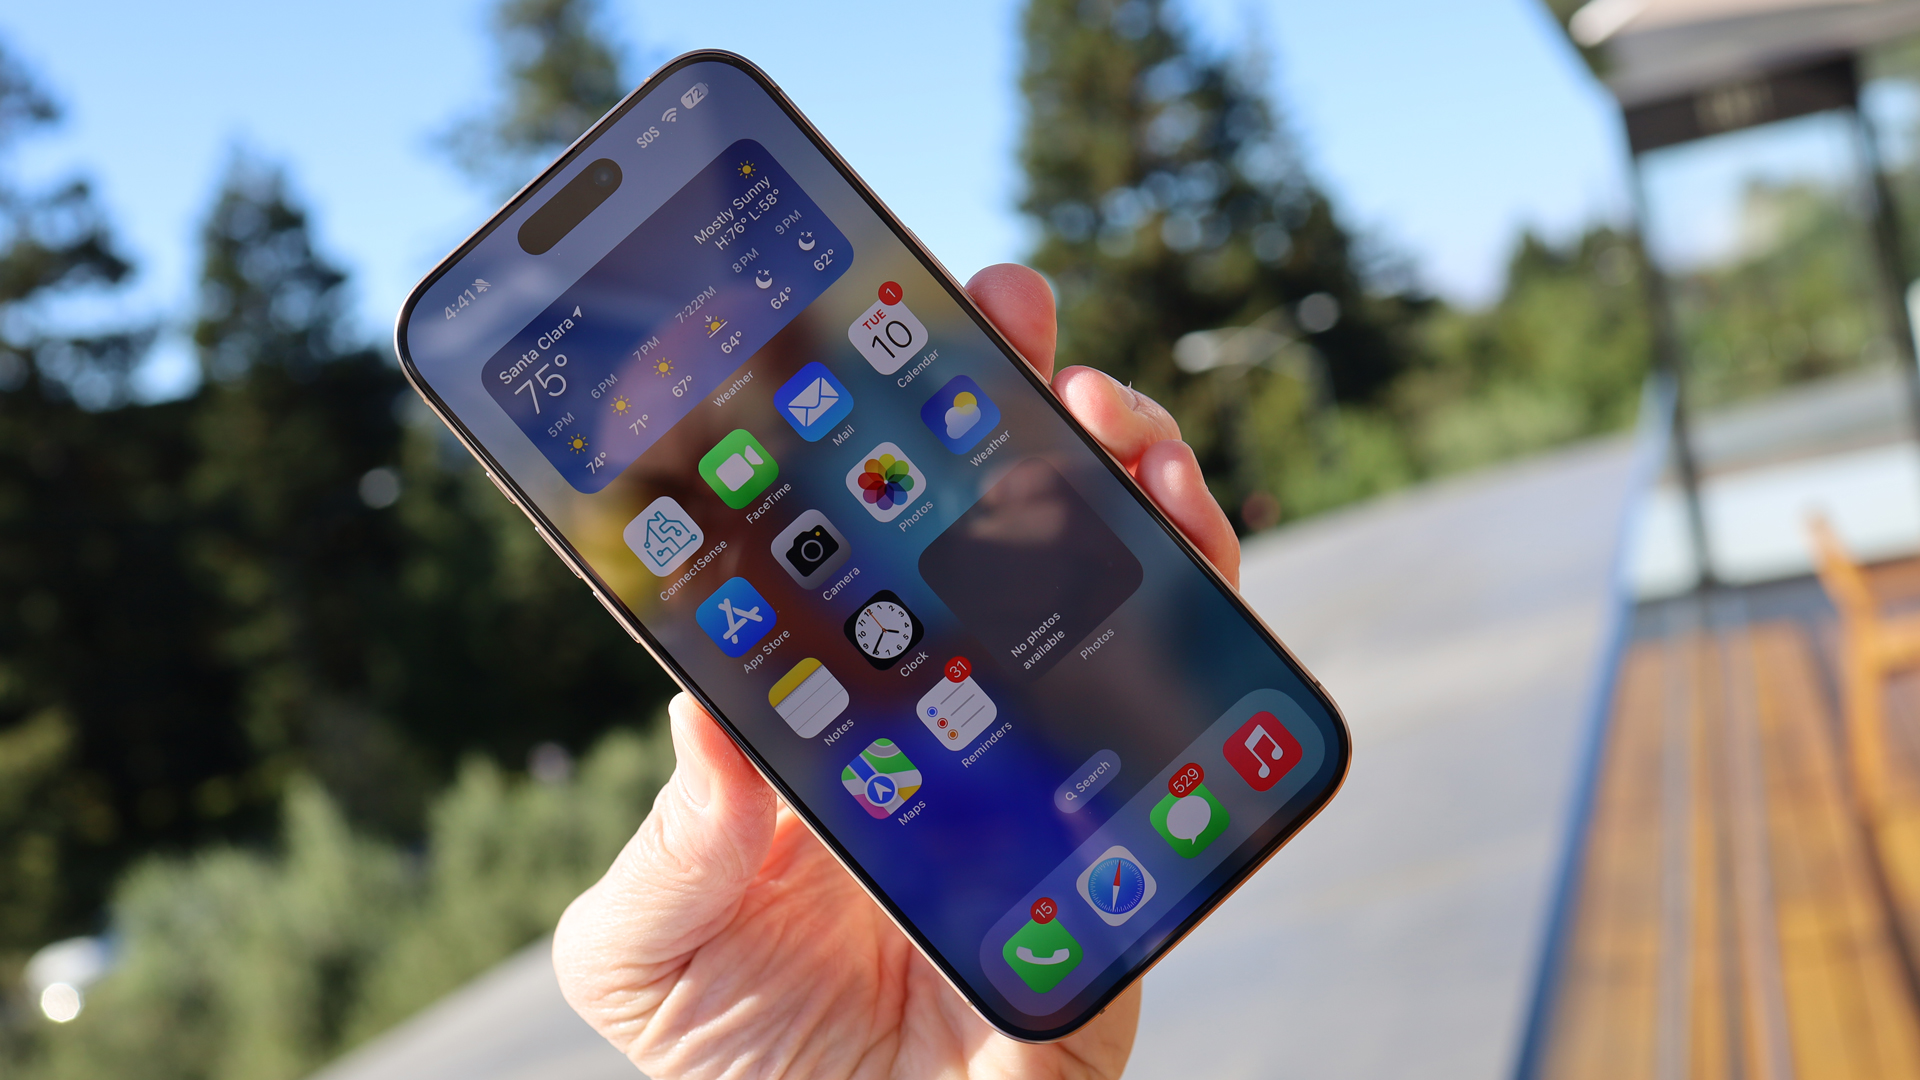
Rank 62700The iPhone 17 Pro Max could have a 5,000mAh batteryThat would make it over 300mAh higher capacity than the iPhone 16 Pro Max'sThis could be one of the main spec upgrades on this phoneWe’ve heard quite a lot about the iPhone 17 Pro Max at this point, but surprisingly one of the biggest potential upgrades has only just leaked.According to leaker Setsuna Digital (via GSMArena), the iPhone 17 Pro Max could have a 5,000mAh battery, and while that’s a common capacity for Android phones, it’s far higher than we’ve so far seen from an iPhone.The iPhone 16 Pro Max has the biggest battery Apple has so far put in a phone, but it’s still only 4,685mAh. So if this leak is correct, the iPhone 17 Pro Max will have an extra 315mAh to play with.Boosting the battery to 5,000mAh would finally make Apple’s battery specs more comparable with Android phones, and would likely mean the actual life of the iPhone 17 Pro Max is far greater than most Android handsets, as iPhones tend to be very power-efficient.The iPhone 16 Pro Max (Image credit: Future / Lance Ulanoff)A bigger boost than usualSo that’s all good news, though we’d take this with a pinch of salt, as while the source of this tip has a solid track record we haven’t heard this from anyone else yet, and that would be a slightly bigger battery jump than we tend to see from Apple.But if the iPhone 17 Pro Max really does have a 5,000mAh battery then that could make for one of the most exciting upgrades on a phone that so far doesn’t sound like it will be a vast improvement on the iPhone 16 Pro Max.Going by current leaks, the main change could be to the design – though the chipset and some of the cameras will probably also be improved. So a boost in battery life could help this phone feel like more of an upgrade than it might otherwise.And while this leak only talks about the iPhone 17 Pro Max, if it really is getting a big battery boost then there’s a fair chance the other iPhone 17 models will too. We should find out in September, as that’s probably when Apple will unveil these new handsets.You might also likeiPhone 17 Air leaked specs suggest it's likely to beat the S25 Edge in one key way – and lose out in anotherThe foldable iPhone’s cameras might leave it trailing behind the Galaxy Z Fold 7The iPhone 17 Pro’s rumored camera bar looks much better than before in new dummy unit photos