News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-
Picture from cdn.mos.cms.futurecdn.net
Rank 61951Hackers are actively targeting a messaging app used by federal agenciesThe app was also involved in the Signalgate scandalHackers have already stolen chats and metadata from 60 government officialsThe US Cybersecurity and Infrastructure Security Agency (CISA) has warned a popular Signal messaging app clone being used by federal agencies is under attack.The clone, TeleMessage, was found to have some serious issues, including a lack of proper end-to-end encryption.Hackers have been exploiting two flaws, CVE-2025-48927 and CVE-2025-48928, to access federal chat logs and metadata. CISA has given federal agencies until July 22 to apply patches.Federal chat app hackedThe new comes months after then-US national security advisor Mike Waltz accidentally added Jeffrey Goldberg, editor in chief at The Atlantic, to a secret Signal chat discussing ongoing US strikes against Houthi rebels in Yemen. Waltz was then removed from his position as a result.Following investigations into the fiasco, it emerged that Waltz and others weren’t using Signal, but a clone of the app called TM SGNL, which was developed by TeleMessage.The app was then subsequently targeted in an attack that saw the chat logs and metadata of around 60 government officials including Secret Service members and a White House official leaked online.The first flaw listed by CISA, CVE-2025-48927, has a CVSS score of 5.3, and allows hackers to extract sensitive data from memory dumps exposed by a Spring Boot Actuator misconfiguration in the TeleMessage app that exposes the /heapdump endpoint.The second flaw, CVE-2025-48928, has a CVSS score of 4.0, and allows an attacker to access exposed passwords sent over HTTP by stealing a memory-dump file through local access to the TeleMessage server.No other details on the flaws have been released by CISA, but the agency has said that federal agencies must patch the app by July 22 or stop using it altogether.Via The RegisterYou might also likeSalt Typhoon: US cybersecurity watchdog urges switch to Signal-like messaging appsTake a look at the best encrypted messaging appsEven Donald Trump can't get a good connection for a work video call
-
Picture from o.aolcdn.com
Rank 61952The developer beta for iOS 26 has been out for a few weeks, and as always,tech sleuths are uncovering features and details that weren't explained during WWDC. Among the latest discoveries stirring up conversation online is a safety and privacy feature for FaceTime that blurs your feed when it detects you in a state of undress. Should FaceTime detect nudity, it will display a message reading "Audio and video are paused because you may be showing something sensitive. If you feel uncomfortable, you should end the call."
Originally discovered by X user @iDeviceHelpus, the feature is off by default and can be enabled in FaceTime settings under "Sensitive Content Warning." The feature reads, "Detect nude photos and videos before they are viewed on your device, and receive guidance to help make a safe choice. Apple does not have access to the photos or videos."It seems the feature is intended for child accounts, though it can currently be enabled in the beta for adults as well.
The Apple support page for the company's "Communication Safety" features reads, "Communication Safety uses on-device machine learning to analyze photo and video attachments and determine if a photo or video appears to contain nudity. Because the photos and videos are analyzed on your child's device, Apple doesn't receive an indication that nudity was detected and doesn't get access to the photos or videos as a result."
Features in beta come and go, as testing and feedback are partly the point of the beta system, so this may or may not see broader adoption. The public beta for iOS 26 is slated for July.This article originally appeared on Engadget at https://www.engadget.com/mobile/ios-26-can-freeze-your-facetime-video-if-it-detects-nudity-135329941.html?src=rss
-

Picture from ichef.bbci.co.uk
Rank 61953 -
Picture from assets3.cbsnewsstatic.com
Rank 61954 -

Picture from assets1.cbsnewsstatic.com
Rank 61955 -

Picture from image.cnbcfm.com
Rank 61956 -
Picture from cdn.mos.cms.futurecdn.net
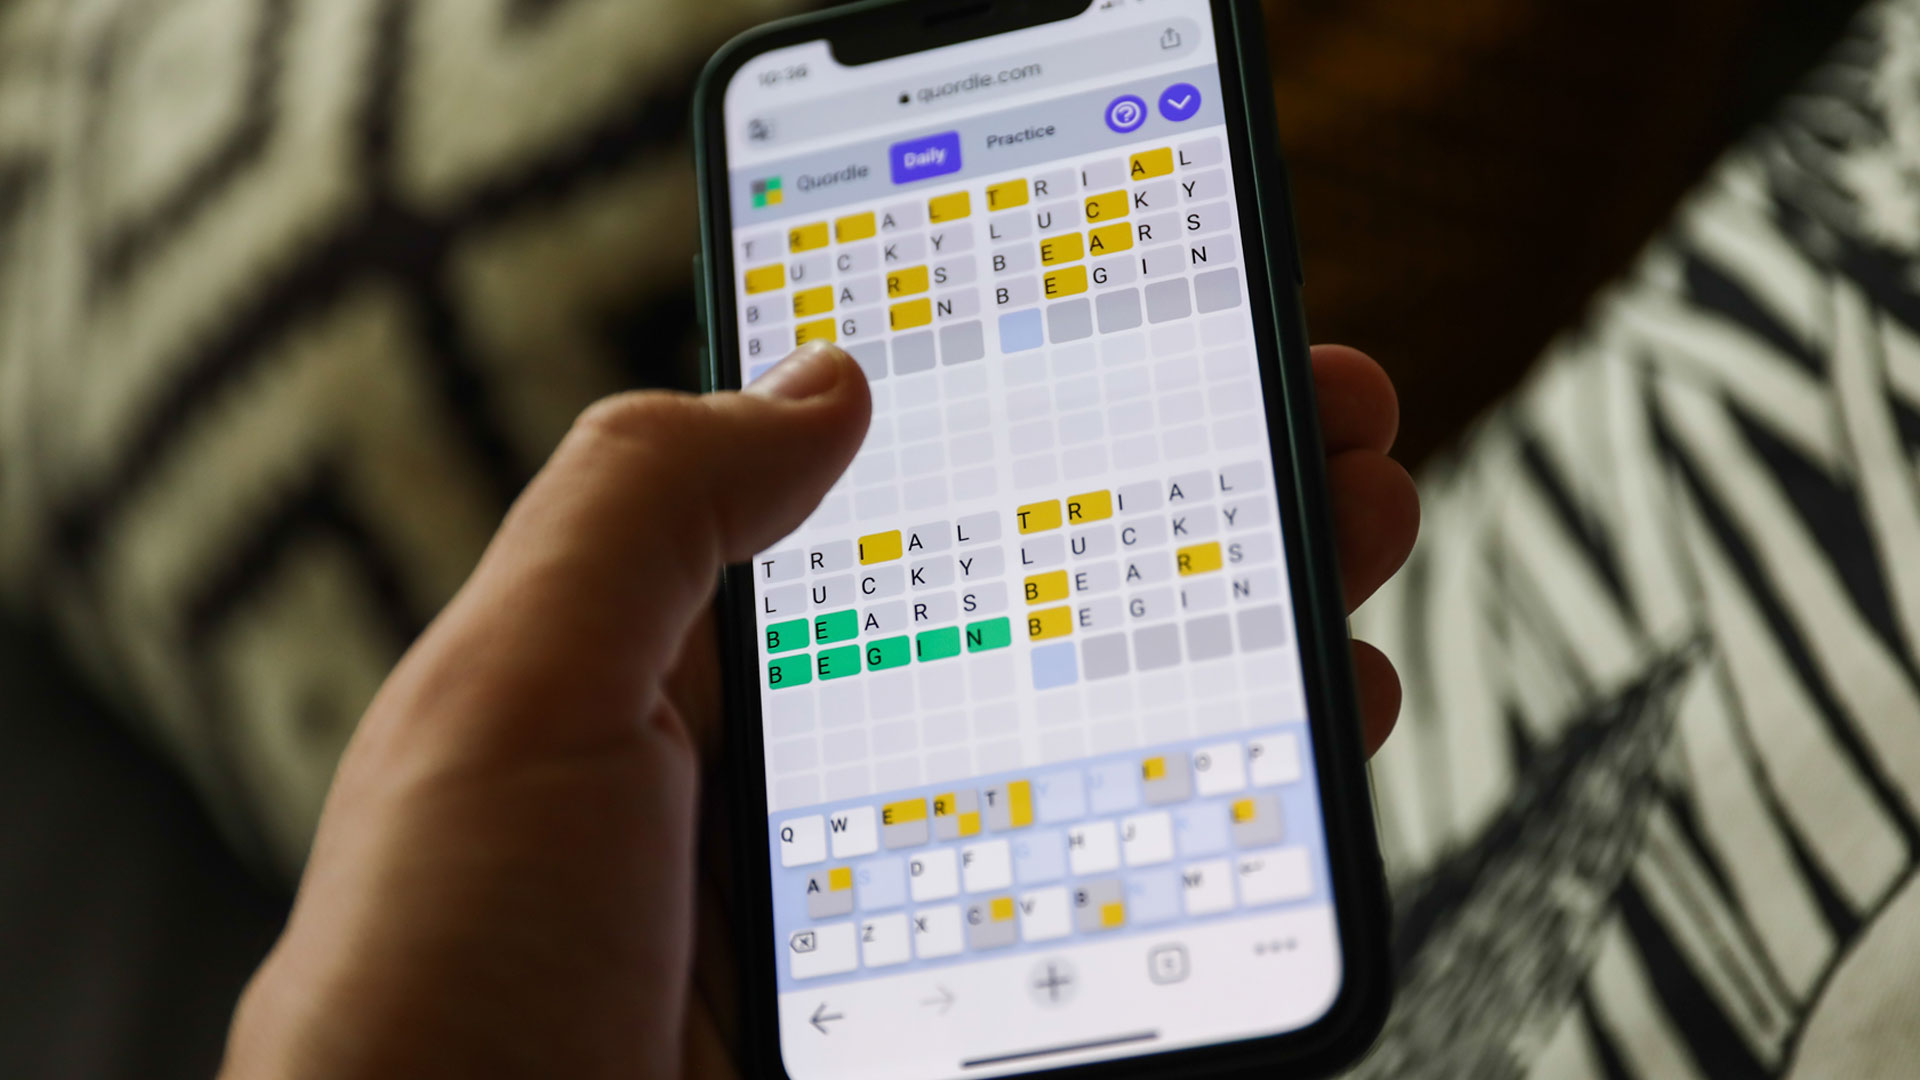
Rank 61957Looking for a different day?A new Quordle puzzle appears at midnight each day for your time zone – which means that some people are always playing 'today's game' while others are playing 'yesterday's'. If you're looking for Thursday's puzzle instead then click here: Quordle hints and answers for Thursday, July 3 (game #1256).Quordle was one of the original Wordle alternatives and is still going strong now more than 1,100 games later. It offers a genuine challenge, though, so read on if you need some Quordle hints today – or scroll down further for the answers.Enjoy playing word games? You can also check out my NYT Connections today and NYT Strands today pages for hints and answers for those puzzles, while Marc's Wordle today column covers the original viral word game.SPOILER WARNING: Information about Quordle today is below, so don't read on if you don't want to know the answers.Quordle today (game #1257) - hint #1 - VowelsHow many different vowels are in Quordle today?• The number of different vowels in Quordle today is 3*.* Note that by vowel we mean the five standard vowels (A, E, I, O, U), not Y (which is sometimes counted as a vowel too). Quordle today (game #1257) - hint #2 - repeated lettersDo any of today's Quordle answers contain repeated letters?• The number of Quordle answers containing a repeated letter today is 2.Quordle today (game #1257) - hint #3 - uncommon lettersDo the letters Q, Z, X or J appear in Quordle today?• No. None of Q, Z, X or J appear among today's Quordle answers.Quordle today (game #1257) - hint #4 - starting letters (1)Do any of today's Quordle puzzles start with the same letter?• The number of today's Quordle answers starting with the same letter is 2.If you just want to know the answers at this stage, simply scroll down. If you're not ready yet then here's one more clue to make things a lot easier:Quordle today (game #1257) - hint #5 - starting letters (2)What letters do today's Quordle answers start with?• F• S• G• FRight, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON'T WANT TO SEE THEM.Quordle today (game #1257) - the answers(Image credit: Merriam-Webster)The answers to today's Quordle, game #1257, are…FAVORSKUNKGAWKYFLUFFToday was a great example of a mistake leading to a tricky answer I might not have solved otherwise. I incorrectly guessed “snuff” instead of SKUNK and the F-F ending opened up FLUFF.Incidentally, fluff is one of a small number of five-letter words with just three unique letters. Only one English five letter word has two unique letters. Don’t know it? Ask your mamma.Sorry for the terrible dad joke.How did you do today? Let me know in the comments below.Daily Sequence today (game #1257) - the answers(Image credit: Merriam-Webster)The answers to today's Quordle Daily Sequence, game #1257, are…THEMEMULCHDEUCEOCCURQuordle answers: The past 20Quordle #1256, Thursday, 3 July: DANCE, EYING, GLAZE, EGRETQuordle #1255, Wednesday, 2 July: INANE, SCOUR, ELITE, ULCERQuordle #1254, Tuesday, 1 July: REBAR, YEARN, FORTH, CROWDQuordle #1253, Monday, 30 June: INGOT, INFER, TAPIR, CLUEDQuordle #1252, Sunday, 29 June: MIRTH, APTLY, SCRUB, SMACKQuordle #1251, Saturday, 28 June: AWOKE, SMOKY, DEVIL, SWINGQuordle #1250, Friday, 27 June: SPEAK, EAGLE, AVERT, SUINGQuordle #1249, Thursday, 26 June: SLUMP, REBUS, GUAVA, MONEYQuordle #1248, Wednesday, 25 June: SOGGY, CLASH, MODEM, SQUADQuordle #1247, Tuesday, 24 June: QUALM, SQUIB, AXIAL, FLACKQuordle #1246, Monday, 23 June: PIXEL, FJORD, STEAL, EXISTQuordle #1245, Sunday, 22 June: WREST, CRAZE, PAPAL, SCIONQuordle #1244, Saturday, 21 June: BUDDY, GROUT, BEGIN, MADAMQuordle #1243, Friday, 20 June: BRAID, DULLY, HASTE, LURIDQuordle #1242, Thursday, 19 June: BRUSH, ISLET, FRUIT, PRIVYQuordle #1241, Wednesday, 18 June: MEDIA, SHARK, GUPPY, MOURNQuordle #1240, Tuesday, 17 June: LEAPT, PRISM, ADMIN, WHINEQuordle #1239, Monday, 16 June: RETRY, SCALD, DINGO, FEIGNQuordle #1238, Sunday, 15 June: SHOCK, STEIN, BROIL, COVENQuordle #1237, Saturday, 14 June: STICK, FERRY, THESE, IONIC
-
Picture from cdn.mos.cms.futurecdn.net
Rank 61958Looking for a different day?A new NYT Connections puzzle appears at midnight each day for your time zone – which means that some people are always playing 'today's game' while others are playing 'yesterday's'. If you're looking for Thursday's puzzle instead then click here: NYT Connections hints and answers for Thursday, July 3 (game #753).Good morning! Let's play Connections, the NYT's clever word game that challenges you to group answers in various categories. It can be tough, so read on if you need Connections hints.What should you do once you've finished? Why, play some more word games of course. I've also got daily Strands hints and answers and Quordle hints and answers articles if you need help for those too, while Marc's Wordle today page covers the original viral word game.SPOILER WARNING: Information about NYT Connections today is below, so don't read on if you don't want to know the answers.NYT Connections today (game #754) - today's words(Image credit: New York Times)Today's NYT Connections words are…DRABBLOWMISSSPOKETIREDUCTWASTEFATIGUEEXHAUSTRIMKHAKIHOSELOSEPIPEHUBCAMONYT Connections today (game #754) - hint #1 - group hintsWhat are some clues for today's NYT Connections groups?YELLOW: Circular car componentGREEN: Army garments BLUE: Let it flowPURPLE: A chance that slipped awayNeed more clues?We're firmly in spoiler territory now, but read on if you want to know what the four theme answers are for today's NYT Connections puzzles…NYT Connections today (game #754) - hint #2 - group answersWhat are the answers for today's NYT Connections groups?YELLOW: PARTS OF A WHEEL GREEN: MILITARY CLOTHING DESCRIPTORS BLUE: USED IN VENTILATION PURPLE: FAIL TO TAKE ADVANTAGE OF, AS AN OPPORTUNITY Right, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON'T WANT TO SEE THEM.NYT Connections today (game #754) - the answers(Image credit: New York Times)The answers to today's Connections, game #754, are…YELLOW: PARTS OF A WHEEL HUB, RIM, SPOKE, TIREGREEN: MILITARY CLOTHING DESCRIPTORS CAMO, DRAB, FATIGUE, KHAKIBLUE: USED IN VENTILATION DUCT, EXHAUST, HOSE, PIPEPURPLE: FAIL TO TAKE ADVANTAGE OF, AS AN OPPORTUNITY BLOW, LOSE, MISS, WASTEMy rating: EasyMy score: PerfectAfter a terrible streak it felt good to complete a round of Connections without making a mistake. I can only conclude that today’s edition was an unusually easy one; even the purple group would be at yellow-level on some days. My only pause for thought was over MILITARY CLOTHING DESCRIPTORS; CAMO, FATIGUE, and KHAKI all seemed common enough, but DRAB was a guess based on how dull army clothing is.How did you do today? Let me know in the comments below.Yesterday's NYT Connections answers (Thursday, July 3, game #753)YELLOW: CORRESPONDENCE CONTACT, DEALINGS, EXCHANGE, INTERACTIONGREEN: AIRPORT BOARD INFO ARRIVAL, DESTINATION, FLIGHT, GATEBLUE: PRO ATHLETE DATA COLLEGE, NUMBER, POSITION, TEAMPURPLE: FARMERS' THINGS ALMANAC, INSURANCE, MARKET, TANWhat is NYT Connections?NYT Connections is one of several increasingly popular word games made by the New York Times. It challenges you to find groups of four items that share something in common, and each group has a different difficulty level: green is easy, yellow a little harder, blue often quite tough and purple usually very difficult.On the plus side, you don't technically need to solve the final one, as you'll be able to answer that one by a process of elimination. What's more, you can make up to four mistakes, which gives you a little bit of breathing room.It's a little more involved than something like Wordle, however, and there are plenty of opportunities for the game to trip you up with tricks. For instance, watch out for homophones and other word games that could disguise the answers.It's playable for free via the NYT Games site on desktop or mobile.
-
Picture from cdn.mos.cms.futurecdn.net
Rank 61959Looking for a different day?A new NYT Strands puzzle appears at midnight each day for your time zone – which means that some people are always playing 'today's game' while others are playing 'yesterday's'. If you're looking for Thursday's puzzle instead then click here: NYT Strands hints and answers for Thursday, July 3 (game #487).Strands is the NYT's latest word game after the likes of Wordle, Spelling Bee and Connections – and it's great fun. It can be difficult, though, so read on for my Strands hints.Want more word-based fun? Then check out my NYT Connections today and Quordle today pages for hints and answers for those games, and Marc's Wordle today page for the original viral word game.SPOILER WARNING: Information about NYT Strands today is below, so don't read on if you don't want to know the answers.NYT Strands today (game #488) - hint #1 - today's themeWhat is the theme of today's NYT Strands?• Today's NYT Strands theme is… ... Let's have a picnic!NYT Strands today (game #488) - hint #2 - clue wordsPlay any of these words to unlock the in-game hints system.BARNLOREBUGSSTARTRACESNORENYT Strands today (game #488) - hint #3 - spangram lettersHow many letters are in today's spangram?• Spangram has 8 lettersNYT Strands today (game #488) - hint #4 - spangram positionWhat are two sides of the board that today's spangram touches?First side: top, 4th columnLast side: bottom, 4th columnRight, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON'T WANT TO SEE THEM.NYT Strands today (game #488) - the answers(Image credit: New York Times)The answers to today's Strands, game #488, are…BURGERSSALADCOLESLAWBRATSBEANSWATERMELONSPANGRAM: BARBECUEMy rating: EasyMy score: PerfectI roared through today’s word search at rapid speed. Most likely because I’m hungry and I’d love a BURGER – not one from a BARBECUE, though. In my experience that’s a bad idea. But also because there was little to challenge us here beyond the twisty-turny WATERMELON.It may be different in the United States, where people who don’t usually cook have more opportunities to practice burning meat, but in the UK a barbecue is a rare event that usually results in some form of drama caused by drinking in the sunshine alongside a long list of food hygiene infringements.Again, most likely different in other parts of the world, but the traditional British barbecued burger is burnt to a crisp on the outside and raw, bordering on still frozen, on the inside – and served on a bun that is chemically closer to rubber than bread. Strangely, I don't feel hungry anymore.How did you do today? Let me know in the comments below.Yesterday's NYT Strands answers (Thursday, July 3, game #487)CHERRYCOFFEEBUTTERSCOTCHBROWNIEPISTACHIOSPANGRAM: ICE CREAMWhat is NYT Strands?Strands is the NYT's not-so-new-any-more word game, following Wordle and Connections. It's now a fully fledged member of the NYT's games stable that has been running for a year and which can be played on the NYT Games site on desktop or mobile.I've got a full guide to how to play NYT Strands, complete with tips for solving it, so check that out if you're struggling to beat it each day.
-

Picture from techcrunch.com
Rank 61960 -

Picture from static.independent.co.uk
Rank 61961 -
Picture from static.independent.co.uk
Rank 61962 -

Picture from image.cnbcfm.com
Rank 61963 -

Picture from image.cnbcfm.com
Rank 61964 -

Picture from ichef.bbci.co.uk
Rank 61965 -

Picture from static.independent.co.uk
Rank 61966 -

Picture from assets2.cbsnewsstatic.com
Rank 61967 -
Picture from cdn.mos.cms.futurecdn.net
Rank 61968There’s no shortage of ambition around AI in UK businesses. It’s on board agendas, investor decks and product roadmaps. And yet, for all the buzz, not every organization is seeing meaningful value. According to our research, three out of four UK business leaders say they’re falling behind on AI.It’s not due to a lack of vision. In fact, most businesses know exactly what AI could do – automate manual work, generate insights, scale faster. The challenge often comes down to execution.Because success with AI isn’t about one tool, one use case or one budget cycle. It’s about the systems, behaviors and product choices that shape how work gets done. And when those foundations aren’t set up for speed, even the smartest AI strategy can stall.From a product perspective, three recurring patterns emerge: infrastructure that hasn’t kept up, ways of working that resist change and tools that overcomplicate instead of enable. None of these are permanent blockers – but they need to be designed for, not worked around.Turning legacy systems into launchpads Most businesses aren’t dealing with broken systems – just ones that were built for a different time. And over years of growth and expansion, those systems can become more tangled than intentional.45% of UK business leaders say legacy tech stacks are a major barrier to getting real value from AI – often because the systems beneath them can’t keep up. That’s where friction builds: data stored in different formats, tools that don’t integrate, teams working around the tech rather than with it. When AI enters the picture, those gaps matter. It doesn’t just need data – it needs data that moves.The good news is that you don’t need to start from scratch. Strategic simplification – consolidating systems, integrating platforms, removing duplications – creates the breathing room AI needs to function. It’s about aligning what you already have to work harder, together.That’s why businesses are moving towards platforms that unify core tools. We see the most progress when customers focus less on overhauling and more on unlocking single sources of truth. When systems are connected and data flows freely, AI becomes less of a bolt-on and more of a multiplier.Designing change people want to be part of Our research found that a third of UK business leaders experience pushback when updating legacy systems or introducing new processes. That hesitation is often labelled as resistance – but more often, it’s a call for clarity. People want to understand how AI fits into their day-to-day work.When AI is introduced without context – or without input from the people expected to use it – it can feel more like disruption than progress. And that’s where adoption often falters.The real shift happens when leaders approach change like a product rollout – with transparency and feedback built in. That means involving teams early, framing AI as an enabler and showing clear wins that matter to employees: time saved, tasks simplified, better decisions made faster. It also needs commitment from leadership to effective change management and AI empowerment.Equally important is giving teams the confidence to experiment. AI is an evolving capability. Employees need to feel safe to test, question and shape how these tools work in practice.It doesn’t always take a huge transformation programme to shift culture. In many teams, the change starts with solving a small, frustrating problem in a better way – and sharing how it’s done.Keeping it simple enough to scaleEven with modern systems and engaged teams, there is one more barrier that can slow AI adoption: complexity. Not in the concept of AI itself, but in how it shows up in people’s work.According to our research, 35% of UK business leaders say they’re struggling to bridge this skills gap and give their teams the confidence to use new AI tools effectively. And often, that comes down to how those tools are built – with technical users in mind, not everyday use.They sit outside established workflows or feel disconnected from the work people are actually trying to do. In resource-conscious organizations, this kind of friction can stall adoption altogether.Simplicity is all about reducing the time between intention and outcome. The more intuitive a tool is, the faster it delivers value. A well-designed AI system doesn’t just speed up tasks – it helps teams reach clarity faster, with less back-and-forth and fewer dependencies. It also scales better. Tools that are simple to use are easier to roll out, train, and maintain – especially across cross-functional teams.Creating the right conditions for AI to deliver UK businesses seeing value from AI aren’t rushing ahead. They’re creating conditions for progress.That means designing processes that evolve, cultures that stay open to iteration and products that learn alongside the people actually using them. The fact is that AI doesn’t need a perfect environment. It just needs a responsive one – built to both implement change and sustain it.What matters most isn’t scale on day one, but the ability to keep improving.We've featured the best AI chatbot for business.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-

Picture from static.independent.co.uk
Rank 61969 -
Picture from sc.cnbcfm.com
Rank 61970 -

Picture from ichef.bbci.co.uk
Rank 61971 -

Picture from static.independent.co.uk
Rank 61972 -

Picture from static.independent.co.uk
Rank 61973 -

Picture from static.independent.co.uk
Rank 61974 -

Picture from assets3.cbsnewsstatic.com
Rank 61975 -
Picture from cdn.mos.cms.futurecdn.net
Rank 61976From sleek conferencing setups and smart classrooms to complex control rooms, audiovisual (AV) systems have become an essential part of how we work and communicate. But behind the interfaces lies an often-overlooked risk – security. Many AV systems still run on outdated software and firmware, creating vulnerabilities that attackers can exploit with relative ease.Because AV equipment is not always seen as ‘business critical’ and is sometimes managed separately from the core IT infrastructure, it is frequently assumed to be safe - isolated on its own network or low risk by nature. But this complacency is dangerous. Many devices operate on older versions of software packages which are not always updated even when new versions are released for the device. This creates vulnerabilities in the system.Knowing the risks While hybrid working has brought convenience it’s also increased risk. Remote access may speed up troubleshooting, but it also expands the attack surface. Social engineering attacks such as phishing can trick users into handing over access credentials, especially when awareness is low.As cyber attackers become more sophisticated, they’re shifting their attention to overlooked entry points like AV infrastructure. A good example is YouTuber Jim Browning’s infiltration of a scam call center, where he used unsecured CCTV systems to monitor and expose criminals in real time. This highlights the potential for AV vulnerabilities to be exploited for intelligence gathering.To counter these risks, organizations must adopt a more proactive approach. Simulated social engineering and phishing attacks can help assess user awareness and expose vulnerabilities in behavior. These simulations should be backed by ongoing training that equips staff to recognize manipulation tactics and understand the value of security hygiene.In parallel, organizations that use third parties for remote support should be prioritize partners that undergo independent security audits such as ISO 27001 and Cyber Essentials Plus. These accreditations help ensure that strict controls are in place around remote access, including the use of secure management tools and clearly defined policies governing their use.CVSS – a measured approach to risk Not all AV vulnerabilities are created equal. That's where the Common Vulnerability Scoring System (CVSS) comes in. CVSS helps IT and AV teams prioritize their response by evaluating the complexity of an attack, the scope of its potential impact, and its effect on confidentiality, integrity, and availability.Vulnerabilities with CVSS scores above 7.5 should prompt swift mitigation. Those rated at the maximum 10 out of 10 require immediate action due to their high severity and low complexity of exploitation. That said, patching these vulnerabilities isn’t always straightforward. In complex, interconnected AV environments, patching updates can introduce compatibility issues that disrupt operations. Organizations should adopt a measured, risk-based approach, balancing the likelihood of exploitation against operational stability.The severity of breaches also depends on the device and its role. Compromised management interfaces or control code could allow attackers to manipulate systems or access other network devices. Exploited cameras and microphones can lead to breaches of video or audio data, posing serious privacy risks and enabling unauthorized surveillance.Strengthening AV security To mitigate the risks posed by vulnerable AV systems, organizations should take a proactive and layered approach to security. This includes regularly updating device firmware and underlying software packages, which are often left outdated even when new versions are available. Strong password policies should be enforced, particularly on devices running webservers, with security practices aligned to standards like the OWASP Top 10.Physical access to AV infrastructure must also be tightly controlled to prevent unauthorized LAN connections. Where legacy protocols like SCP, SFTP, FTP, or Telnet are still in use, these should be hardened or disabled wherever possible. Encrypting communication between devices using modern protocols such as TLS 1.3, and ensuring appropriate cipher suites are in place, helps safeguard data in transit. Similarly, encrypting data at rest, whether configuration files, control code or temporary data, adds another layer of protection, limiting the damage that can result from a breach.Collaboration is key Ultimately, security is a shared responsibility. While network teams play a central role in defending infrastructure, leaving all security decisions to them can be shortsighted. Many vulnerabilities stem from device-specific issues such as outdated firmware, default configurations, or poorly managed passwords that cannot always be mitigated by network controls alone. Even a well-configured device can present risks if it’s connected to a poorly segmented or insecure network.AV professionals, IT leads, and vendors need to collaborate closely, sharing expertise and intelligence to identify vulnerabilities and address integration challenges. AV teams must take an active role by ensuring devices are updated and properly configured before deployment, clearly communicating potential risks and requirements to network teams, and following best practices such as implementing VLANs, restricting unnecessary traffic, and enabling secure management protocols.By working together, organizations can build a layered defense that addresses risks at both the device and network levels; strengthening the overall security posture and reducing the likelihood of a breach.AV systems may not be the first thing you think of when you hear ‘cybersecurity risk’ and that’s exactly the problem. From data leaks and surveillance breaches to unauthorized lateral movement across networks, the consequences of ignoring AV security are real. It’s time to treat AV like the critical infrastructure it has become.We've featured the best headset for working from home.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-
Picture from o.aolcdn.com
Rank 61977Regardless of if you need a new laptop for the upcoming semester or for general use at home, Amazon Prime Day 2025 may have just what you’re looking for at a good price. Among the clothing, shoes, household essentials and other tech gear already on sale are some decent laptop deals that you can snag if you’re a Prime member — and even some that you can grab without a Prime subscription.But deciphering what constitutes a “good deal” on a laptop during Prime Day can be a bit challenging. That’s due in part to the manic nature of laptop prices on Amazon in particular: they fluctuate often depending on model, brand, configuration, seller and more. But Engadget can help by collecting all of the best Prime Day laptop deals here so you don’t have to go searching for them.
Prime Day laptop deals: MacBooks
Apple’s latest laptops are the MacBook Air M4 and the MacBook Pro M4, but the M3-powered machines are still available and great values when you can get them at steep discounts. But for the most future-proof options, we recommend going with the M4 MacBooks. Amazon actually has decent MacBook deals throughout the year, most of the time on the base configurations of any given model. In a welcomed update, Apple recently made all base models of the MacBook Air M4 have 16GB of RAM by default (which is the same as you’ll find on the base-level Pros).
MacBook Air (15-inch, M4, 16GB RAM, 256GB SSD) for $1,049 ($150 off)
MacBook Air (15-inch, M3, 24GB RAM, 512GB SSD) for $1,249 (26 percent off)
MacBook Pro (14-inch, M4, 16GB RAM, 512GB SSD) for $1,429 (11 percent off)
Prime Day laptop deals: Chromebooks
Most Chromebooks start off pretty affordable, so that just means you can get them for even less during an event like Prime Day. If you’re a Chrome OS lover, it’s also a decent time to check out sales on premium Chromebooks, which can usually cost $500 or more. In general, we recommend looking for at least 4 to 8GB of RAM and at least 128GB of SDD storage in a Chromebook that you plan on using as your daily driver.
Google Pixelbook Go (13-inch, Intel Core M3) for $315 (51 percent off)
HP Chromebook Plus x360 (14-inch, Intel Core i3, 8GB RAM, 128GB UFS) for $329 (45 percent off)
Acer Chromebook Plus 514 (14-inch, Intel Core i3, 8GB RAM, 128GB SSD) for $335 (16 percent off)
Prime day laptop deals: Windows laptops
You’ve got a lot of variety to choose from when it comes to Windows laptops, and that can be a blessing or a curse. We recommend looking for a laptop from a reputable brand (i.e. Microsoft, Dell, Acer, Lenovo and others like them), and one that can handle daily work or play pressures. That means at least 8GB of RAM and 245GB of SSD storage, plus the latest Intel or AMD CPUs. If you’re looking for a new gaming laptop, you’ll need a bit more power and a dedicated graphics card to boot.
Samsung Galaxy Book5 360 (Windows 11, Copilot+, 15.6-inch, Intel Core Ultra 7, 16GB RAM, 512GB SSD) for $1,100 ($250 off)
Microsoft Surface laptop (Windows 11, Copilot+, 13.8-inch, Snapdragon X Plus) for $880 (27 percent off)
Lenovo V15 G2 laptop (Windows 11 Pro, 15.6-inch, Intel Celeron N4500, 32GB RAM, 1TB SSD) for $399 (33 percent off)
Microsoft Surface Pro 2-in-1 (Windows 11, Copilot+, 13-inch, Snapdragon X Plus, 16GB RAM, 512GB SSD) for $900 (25 percent off)
This article originally appeared on Engadget at https://www.engadget.com/deals/the-best-prime-day-laptop-deals-on-macbooks-chromebooks-windows-11-machines-and-more-130057131.html?src=rss
-

Picture from ichef.bbci.co.uk
Rank 61978 -

Picture from static.independent.co.uk
Rank 61979 -

Picture from static.independent.co.uk
Rank 61980 -

Picture from static.independent.co.uk
Rank 61981 -

Picture from image.cnbcfm.com
Rank 61982 -

Picture from ichef.bbci.co.uk
Rank 61983 -

Picture from static.independent.co.uk
Rank 61984 -

Picture from static.independent.co.uk
Rank 61985 -
Picture from assets3.cbsnewsstatic.com
Rank 61986 -

Picture from image.cnbcfm.com
Rank 61987 -
Picture from cdn.mos.cms.futurecdn.net
Rank 61988Cisco Talos warns of callback phishing scams on the risePhishing emails come with PDF attachments, in which are phone numbersThreat actors are exploiting people's trust in phone callsSecurity researchers from Cisco Talos have warned of an ongoing phishing campaign in which victims are tricked into calling the attackers on the phone.In a new report, the researchers said that between early May and early June 2025, they observed threat actors spoofing major tech companies, such as Microsoft, Adobe, or Docusign.Cisco Talos calls this type of scam “callback phishing” - in the phishing emails, they would notify the victims of a problem, or an incoming/pending transaction, then share a phone number they control, and invite the victim to dial in and address these issues. During the call, the attackers would masquerade as a legitimate customer representative and explain to the victim that in order to sort out their problem, they need to either disclose sensitive information, or install a piece of malware on their device.Get 55% off Incogni's Data Removal service with code TECHRADAR Wipe your personal data off the internet with the Incogni data removal service. Stop identity thievesand protect your privacy from unwanted spam and scam calls.View DealCallback phishing“Attackers use direct voice communication to exploit the victim's trust in phone calls and the perception that phone communication is a secure way to interact with an organization,” the researchers explained.“Additionally, the live interaction during a phone call enables attackers to manipulate the victim's emotions and responses by employing social engineering tactics. Callback phishing is, therefore, a social engineering technique rather than a traditional email threat.”Most phone numbers used in these campaigns are VoIP ones, Cisco Talos further explained, stating that these are more difficult to trace.The key information, including the attacker-controlled phone number, is shared via a .PDF file sent as an attachment. This is usually done to bypass traditional email security mechanisms and ensure the email lands in the inbox.As an added layer of obfuscation, the attackers would sometimes add a QR code into the body of the PDF file, since most AV and email protection tools cannot scan that deep. Furthermore, QR codes are usually scanned via smartphone cameras, and mobile devices rarely have the same level of security as laptops or desktop computers do.Via The Hacker NewsYou might also likeAmerica is the top source of spam, and it’s getting worse thanks to growing data center infrastructureTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-
Picture from o.aolcdn.com
Rank 61989Everyone’s been hit with a bitingly pass-agg "?" text after waiting just a bit too long to reply. And you might soon get similar (though likely more upbeat) treatment from AI chatbots you’ve previously engaged with on Meta platforms like Instagram or WhatApp. A new report from Business Insider claims that the Mark Zuckerberg-owned company is trialling a proactive feature in customizable chatbots created using its no-code AI Studio software, that will enable them to send unprompted follow-up messages based on previous conversations.
Known internally to data labeling firm Alignerr as "Project Omni", the training project will "provide value for users and ultimately help to improve re-engagement and user retention," according to guidelines in the documents BI claims to have seen. Meta advertises AI studio as a platform where "anyone can create an AI character based on their interests" and encourages creators to view the bots as an AI extension of themselves. You can customize a chatbot’s appearance, choose the content it’s trained on and decide which Meta-owned application you want it to appear in, all without "any technical expertise."
According to the BI report, Alignerr’s Project Omni guidelines use the example of a film-focused AI bot it calls "The Maestro of Movie Magic" that might send a user message such as: "I hope you're having a harmonious day! I wanted to check in and see if you've discovered any new favorite soundtracks or composers recently. Or perhaps you'd like some recommendations for your next movie night? Let me know, and I'll be happy to help!"
As BI notes, there is a business incentive for Meta to keep people engaged with its chatbots. Prolonged engagement is vital for increasing revenue, and this year Meta expects to bring in $2 billion to $3 billion from its generative AI products alone. By 2035, the company estimates that figure could be as high as $1.4 trillion. Those kinds of forecasts will only be possible if its AI tools are being used consistently, so a friendly reminder from a chatbot every now and then feels like an obvious move.
The proactive messages are currently still just a test feature. And while it definitely feels like remembering conversations and initiating new ones without invitation is approaching a user consent gray area, a Meta spokesperson told BI that the AI will only send a follow-up message if a user has first initiated the conversation, and it won’t send another message if the first one is ignored. Responses must also be consistent with the AI’s personality and the nature of the previous conversation, maintaining a positive tone while staying away from controversial or sensitive topics unless the user themself has mentioned them.
Last month, Meta started warning its users not to share intimate details in Meta AI’s public feed after it emerged that a large number of users appeared to be doing so unwittingly.This article originally appeared on Engadget at https://www.engadget.com/big-tech/meta-is-reportedly-training-its-ai-chatbots-to-send-unprompted-messages-143229039.html?src=rss
-

Picture from techcrunch.com
Rank 61990 -

Picture from ichef.bbci.co.uk
Rank 61991 -
Picture from ichef.bbci.co.uk
Rank 61992 -

Picture from static.independent.co.uk
Rank 61993 -
Picture from assets3.cbsnewsstatic.com
Rank 61994 -

Picture from assets2.cbsnewsstatic.com
Rank 61995 -

Picture from ichef.bbci.co.uk
Rank 61996 -

Picture from static.independent.co.uk
Rank 61997 -

Picture from static.independent.co.uk
Rank 61998 -

Picture from assets2.cbsnewsstatic.com
Rank 61999 -
Picture from ichef.bbci.co.uk
Rank 62000