News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from ichef.bbci.co.uk
Rank 61151 -

Picture from static.independent.co.uk
Rank 61152 -
Picture from cdn.mos.cms.futurecdn.net
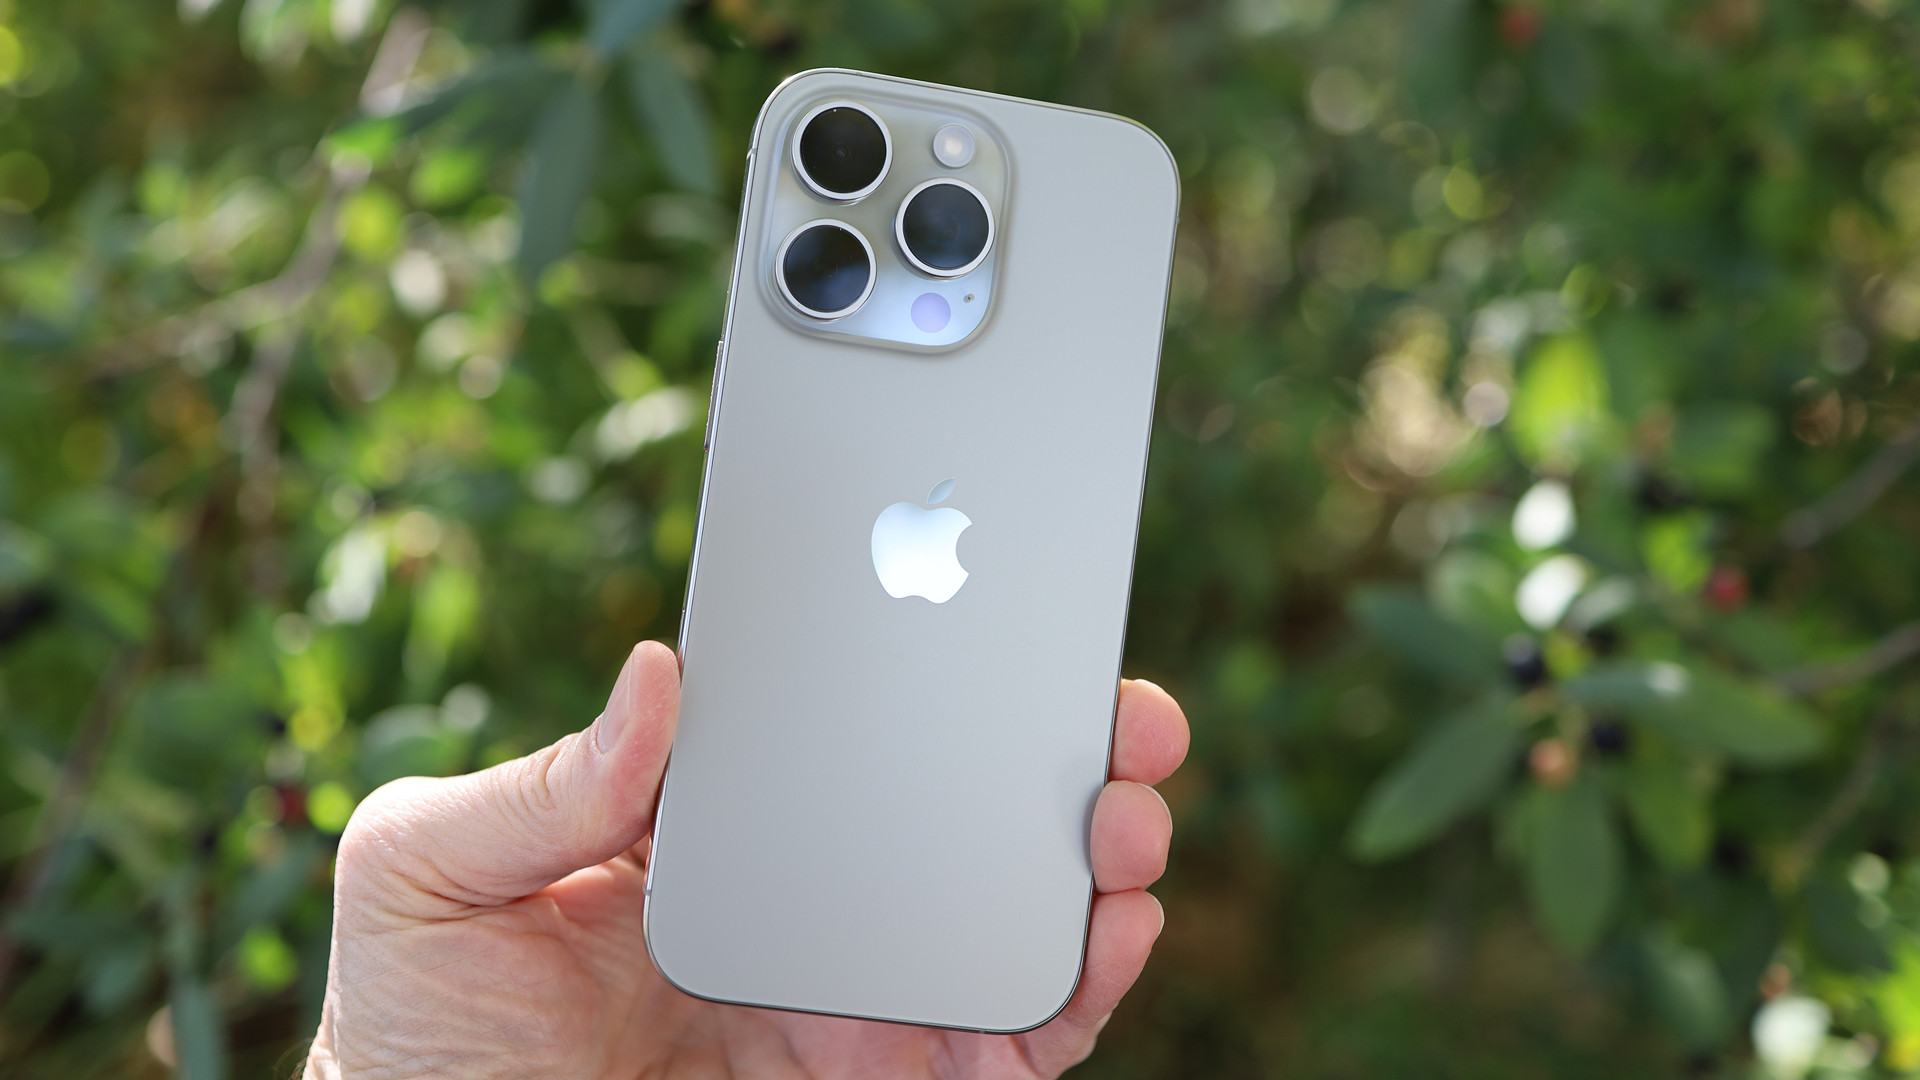
Rank 61153A new rumor suggests Apple could move the logo on the iPhone 17 Pro The logo could move down to make space for the new camera bar and to align with the MagSafe magnet ring While a minor change, this could give some insight into Apple's prioritiesApple could be making a change to an iconic iPhone design element with the release of the rumored iPhone 17 Pro.According to new rumors from somewhat reliable tipster Majin Bu (via GSMArena), Apple could move its logo to a lower position on the rear panel of the iPhone 17 Pro.The possible change has been corroborated in an X (formerly Twitter) post from Apple tipster Sonny Dickson, who posited that the move could align the logo with the phone’s ring of MagSafe magnets.You may be thinking that a logo moving a few centimeters isn’t a huge story on its own – and in all fairness, you’d be right. This alone isn’t too big of a deal.However, I think this latest design rumor has the potential to say a lot about where Apple’s priorities lie when it comes to the next generation of iPhone.Aesthetic alterationsThis mock-up, shared by tipster Majin Bu, shows the iPhone 17 Pro with a lower Apple logo. (Image credit: Majin Bu)This logo tipoff is the latest in a pretty long list of redesign rumors concerning the iPhone 17 lineup, specifically the iPhone 17 Pro and iPhone 17 Pro Max.In fact, it seems to me that the strongest and most repeated rumors surrounding the next Pro-level iPhones have concerned the design and aesthetics of the supposedly-upcoming handsets.As we previously reported, the iPhone 17 Pro and iPhone 17 Pro Max are rumored to get a Google Pixel-like camera bar, a wild departure from the function-led design philosophy of previous generations. Several separate rumors have given us a look at CAD mock-ups and dummy units that seem to confirm the changed design.Though we have heard of a possible higher-resolution telephoto camera, as well as murmurs of a unified volume and Action button and under-display Face ID, it seems like we could be in for a lighter year when it comes to new iPhone hardware features.Considered change, or cover up?It's possible a better telephoto camera could be the only real upgrade to this year's Pro iPhone. (Image credit: Future / Lance Ulanoff)All of this brings new context to the supposed new logo placement – what was previously a pretty innocuous design update begins to look like meddling for the sake of finding something to change.And while all of this is based on rumors at the moment, if Apple were to launch the iPhone 17 Pro with only iterative or less-impactful hardware improvements, then these design shakeups would start to look like an effort to draw attention elsewhere.It wasn’t too long ago that Apple faced considerable backlash for launching the iPhone 14 in a very similar state to the iPhone 13 – Cupertino would be wise to avoid a similar situation this year.With all that said, it’s also possible that Apple is simply looking to refresh the visual identity of its next-gen handsets, to match the new look of the Liquid Glass design language coming with iOS 26.So, while the shifting of an Apple logo by a few centimeters might not seem the biggest story, it’s worth keeping an eye on these small changes as we get closer to the expected September launch date of the iPhone 17 series. Be sure to let us know what you think of this rumored change in the comments below.You might also likeThe foldable iPhone edges closer to reality, according to a new leak – but there's bad news about the foldable iPadGoogle Messages now lets you edit texts you’re sending to iPhones, but there’s a serious catchI went hands-on with the Nothing Phone 3, and it might just be the most interesting phone of the year – here's why
-
Picture from o.aolcdn.com
Rank 61154A US judge has ruled that Huawei must stand trial following a 16-count indictment from 2019 accusing the Chinese telecommunications company of trying to steal trade secrets from its US rivals and selling surveillance equipment to Iran despite trade sanctions, according to a report by Reuters. A trial is currently set for May 4, 2026.
US District Judge Ann Donnelly found sufficient evidence in the indictment to refute the company's bid for dismissal. In a 52-page decision, the Brooklyn judge ruled that its arguments for dismissal were premature. The indictment alleges that Huawei engaged in racketeering, stole trade secrets from six companies and committed bank fraud by misleading the financial organizations about its work in Iran.
The Iran accusations stem from Huawei's alleged control over a Hong Kong-based company called Skycom, which did business in that country. Donnelly said that prosecutors successfully alleged that Skycom "operated as Huawei's Iranian subsidiary and ultimately stood to benefit" from over $100 million in money transfers through the US financial system.
Huawei has pleaded not guilty and sought to dismiss 13 of the 16 counts, referring to itself as "a prosecutorial target in search of a crime." The case goes all the way back to 2019 during President Trump's first term and coincided with the Department of Justice launching an investigation into China's alleged theft of intellectual property.
Chinese officials have accused the US government of "economic bullying" and of using national security concerns as a pretext for "oppressing Chinese companies." The company's CFO Meng Wanzhou, whose father founded the company, was arrested and detained in Canada for three years on allegations that Huawei violated sanctions with Iran. Wanzhou was eventually released and the charges were dismissed.
The US government began restricting Huawei's access to American technology in 2019, citing security concerns. The company struggled to maintain its market share with these restrictions in place, but has since ramped up its own development of chips and related technologies. The company also shifted its focus to the Chinese market.This article originally appeared on Engadget at https://www.engadget.com/big-tech/us-judge-rules-huawei-must-answer-criminal-charges-about-alleged-iran-deal-161552940.html?src=rss
-

Picture from static.independent.co.uk
Rank 61155 -

Picture from static.independent.co.uk
Rank 61156 -

Picture from static.independent.co.uk
Rank 61157 -

Picture from static.independent.co.uk
Rank 61158 -

Picture from static.independent.co.uk
Rank 61159 -

Picture from static.independent.co.uk
Rank 61160 -

Picture from static.independent.co.uk
Rank 61161 -
Picture from static.independent.co.uk
Rank 61162 -
Picture from o.aolcdn.com
Rank 61163In today's gaming world, a decade of development can sometimes amount to nothing. Parent company Microsoft has reportedly cancelled Rare's long-in-development project Everwild. The news comes amid broader layoffs across Microsoft's Xbox division.
Rare employees will likely be part of the Xbox layoffs, according to Video Games Chronicle. VGC and Bloomberg's Jason Schreier were the first to report the game's cancellation. (Schreier added that an MMORPG project from Zenimax, codenamed "Blackbird," was also scrapped.)
Rare officially announced Everwild in 2019. But the game had been in development since around 2014. Its trailer finally arrived five years ago, hinting at a lush and magical atmosphere. However, the footage offered no hints about gameplay. That may have been intentional. Its development reportedly suffered from a lack of clear direction.
Rare / Xbox
It was even said to have survived a "restart from scratch" in 2021 when Gregg Mayles took over direction. (He's known for titles like Donkey Kong Country, Banjo-Kazooie, Viva Piñata and Sea of Thieves.) Xbox explained the lack of official updates by saying it was waiting until it had "something cool to show."
As recently as February, the game seemed to be on track. Microsoft's Phil Spencer said, "It's nice to see the team with Everwild and the progress that they're making." Words, words, words…
That brings us to today, with the coda of an all-too-familiar story. Developers lose jobs. Gamers miss out on the chance to play something that had countless resources poured into it. And the gaming industry tightens its belt even further. How much tighter can it get?This article originally appeared on Engadget at https://www.engadget.com/gaming/everwild-has-reportedly-been-cancelled-amid-xbox-layoffs-162200526.html?src=rss
-
Picture from o.aolcdn.com
Rank 61164The software used by EU border security forces to prevent undocumented immigrants and suspected criminals from travelling in the region is allegedly riddled with holes and vulnerable to cyber attacks. The Second Generation Schengen Information System (SIS II) is an IT system and database shared between most EU states for law enforcement and public security purposes. And according to a new collaborative report between Bloomberg and investigative non-profit Lighthouse Reports, SIS II — which has been used since 2013 — is plagued with "thousands" of cybersecurity issues, to the extent that an EU auditor flagged them to be of "high" severity in a report filed last year.
The report notes that there is no evidence of any data theft, but the "excessive number" of accounts that unnecessarily have access to the database means it could be fairly easily exploited. During its initial rollout, SIS II’s major additions included fingerprint technology and photographs in alerts, and in 2023 the software was updated with upgraded data and enhancements to its existing functionality, including the ability to signal when someone has been deported from a country. Bloomberg reporters spoke to Romain Lanneau, a legal researcher at an EU watchdog called Statewatch, who warned that an attack would be "catastrophic, potentially affecting millions of people."
Right now SIS II operates within an isolated network, but will soon be rolled into the EU’s Entry/Exit system (EES), which will make registering biometric details a requirement for individuals travelling to Schengen-associated areas when it comes into effect, likely later this year. As the EES will be connected to the internet, a hack on the SIS II database will become significantly easier.
Bloomberg and Lighthouse note that while most of the SIS II system’s estimated 93 million records pertain to objects such as stolen vehicles, there are around 1.7 million linked to people. It adds that people usually aren’t aware that their details are logged in the database until law enforcement gets involved, so if the information was leaked, wanted individuals may find it easier to evade the authorities.
SIS II’s development and maintenance is managed by a Paris-based contractor called Sopra Steria. According to the report, as vulnerabilities were reported, they took between eight months and upward of half a decade to resolve. This is despite it being contractually obligated to fix issues deemed to be of critical importance within two months of releasing a patch.
A spokesperson for Sopra Steria did not respond to Bloomberg regarding the detailed list of allegations concerning SIS II’s security holes, but said in a statement printed in the report that EU protocols had been adhered to. "As a key component of the EU’s security infrastructure, SIS II is governed by strict legal, regulatory, and contractual frameworks," it said. "Sopra Steria’s role was carried out in accordance with these frameworks."
EU-Lisa, the EU agency that oversees large-scale IT systems like SIS II, regularly farms out duties to external consulting firms as opposed to building its own in-house tech, according to the investigation. The audit accused the agency of not informing its management about security risks that had been flagged, to which it responded by saying that all systems under its management "undergo continuous risk assessments, regular vulnerability scans, and security testing."This article originally appeared on Engadget at https://www.engadget.com/cybersecurity/the-eus-border-security-software-is-reportedly-full-of-holes-162033816.html?src=rss
-

Picture from ichef.bbci.co.uk
Rank 61165 -
Picture from ichef.bbci.co.uk
Rank 61166 -
Picture from static.independent.co.uk
Rank 61167 -

Picture from static.independent.co.uk
Rank 61168 -

Picture from assets2.cbsnewsstatic.com
Rank 61169 -

Picture from assets2.cbsnewsstatic.com
Rank 61170 -

Picture from assets1.cbsnewsstatic.com
Rank 61171 -

Picture from static.independent.co.uk
Rank 61172 -

Picture from static.independent.co.uk
Rank 61173 -
Rank 61174
-

Picture from static.independent.co.uk
Rank 61175 -

Picture from static.independent.co.uk
Rank 61176 -

Picture from static.independent.co.uk
Rank 61177 -
Picture from image.cnbcfm.com
Rank 61178 -

Picture from static.independent.co.uk
Rank 61179 -

Picture from static.independent.co.uk
Rank 61180 -

Picture from static.independent.co.uk
Rank 61181 -

Picture from static.independent.co.uk
Rank 61182 -

Picture from static.independent.co.uk
Rank 61183 -

Picture from image.cnbcfm.com
Rank 61184 -

Picture from static.independent.co.uk
Rank 61185 -

Picture from assets2.cbsnewsstatic.com
Rank 61186 -
Picture from cdn.mos.cms.futurecdn.net
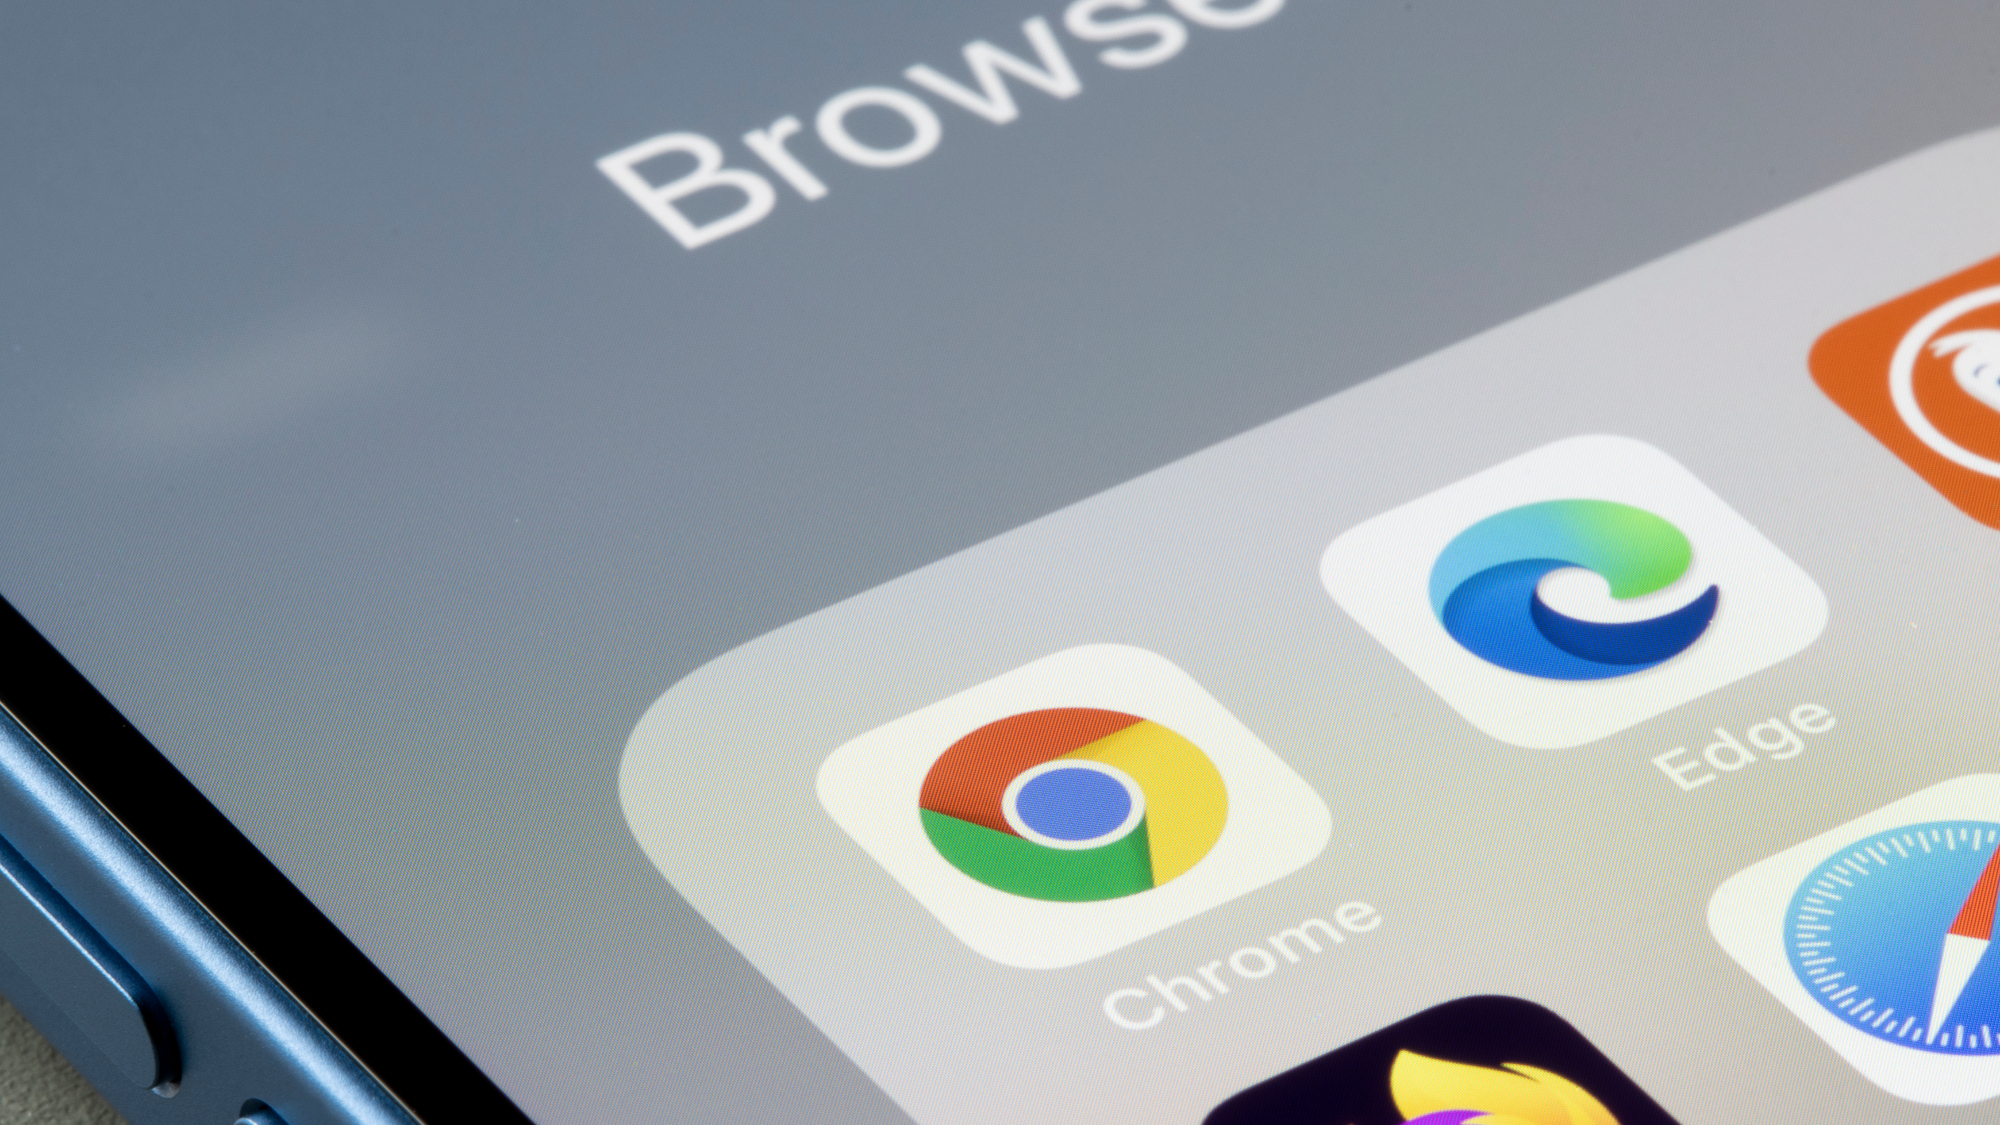
Rank 61187Google's TAG team finds high-severity bug in Chrome V8The bug allows threat actors to run arbitrary code on endpointsIt is being actively exploited, so users should patch nowGoogle has fixed a high-severity Chrome vulnerability which was allegedly being exploited in the wild, possibly by nation-state threat actors.In a new security bulletin, Google said it addressed a type confusion issue in Chrome V8, tracked as CVE-2025-6554, which allowed threat actors to perform arbitrary read/write operations, potentially giving way to sensitive data theft, token exfiltration, or even malware and ransomware deployment.The V8 engine is Google’s open source high-performance JavaScript and WebAssembly engine used in Chrome and other Chromium-based browsers to execute web code efficiently. The bug caused V8 to incorrectly interpret data, leading to unintended behavior. In theory, a threat actor could serve a specially crafted HTML page to a target, which could trigger the RCE.Get 55% off Incogni's Data Removal service with code TECHRADAR Wipe your personal data off the internet with the Incogni data removal service. Stop identity thievesand protect your privacy from unwanted spam and scam calls.View DealNation-states and other adversariesThe bug was given a severity score of 8.1/10 - high, and was addressed in versions 138.0.7204.96/.97 for Windows, 138.0.7204.92/.93 for macOS, and 138.0.7204.96 for Linux, on June 26.In the advisory, Google confirmed the bug was being actively abused, but decided not to share any details until the majority of the browsers are patched. Usually, Chrome automatically installs the patches, but just in case, you might want to head over to chrome://settings/help and allow Chrome to look for updates.While Google kept the details under wraps, knowing who blew the whistle tells us a little more about potential abusers. The bug was discovered by Clément Lecigne of Google’s Threat Analysis Group (TAG), a cybersecurity arm that usually investigates nation-state threat actors.If TAG was looking into this bug, and we know it’s abused in the wild, then it’s safe to assume that it was used by nation-states in highly targeted attacks. Previous V8 flaws have been abused in campaigns against high-profile targets in the past, including journalists, dissidents, IT admins, and similar people.Via Infosecurity MagazineYou might also likeNew Chrome flaw leaks sensitive information across websites - your data could already be in the wrong handsTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-

Picture from techcrunch.com
Rank 61188 -

Picture from assets2.cbsnewsstatic.com
Rank 61189 -
Picture from assets2.cbsnewsstatic.com
Rank 61190 -
Picture from assets2.cbsnewsstatic.com
Rank 61191 -

Picture from assets1.cbsnewsstatic.com
Rank 61192 -

Picture from assets3.cbsnewsstatic.com
Rank 61193 -

Picture from ichef.bbci.co.uk
Rank 61194 -

Picture from image.cnbcfm.com
Rank 61195 -
Picture from o.aolcdn.com
Rank 61196Awesome Games Done Quick and Summer Games Done Quick aren't the only speedrunning marathons in town. There are others dotted throughout the year, such as Frost Fatales and Flame Fatales. Those all-women and femmes events are also operated by the Games Done Quick organization. The schedule for this year's Flame Fatales has just dropped, and there are lots of fascinating runs on deck.
For one thing, you'll be able to watch an Any% run (i.e. beating the game with any percentage) of Hollow Knight. What's more, SawaYoshi will do this one-handed. The runner is expected to pull this off in around 45 minutes — it typically takes around 27 hours to beat that game.
Some newer titles are in the mix as well, such as Blue Prince. It might seem odd that a puzzle game with a heavy randomization element is on the schedule. ProfessorBurtch will be undertaking what's known as a "B Quest Bingo" run. The idea here is to get to the Antechamber while using a bingo board. Here's an example of such a run (it contains spoilers, of course):
Elsewhere, we have Any% runs of the wonderful Neva, The Legend of Zelda: Twilight Princess and New Super Mario Bros. in the mix, along with speedrunning staples like Celeste and The Legend of Zelda: A Link to the Past. The bonus runs include the first act of Clair Obscur: Expedition 33 and all regions of Hades II. I'm very intrigued by the Stardew Valley finale, which is a "Marriage% Co-Op Haley/Penny (Lesbian%)" run.
In all, there will be more than 50 speedruns during this edition of Flame Fatales, which runs from September 7 - 14. This year's edition is being held in support of Malala Fund, which is a non-profit that helps girls around the world to have safe, secure and quality education. The event will be livestreamed on the GDQ Twitch channel.This article originally appeared on Engadget at https://www.engadget.com/gaming/the-flame-fatales-2025-speedrunning-event-includes-blue-prince-hades-2-and-clair-obscur-runs-171451081.html?src=rss
-

Picture from static.independent.co.uk
Rank 61197 -

Picture from static.independent.co.uk
Rank 61198 -

Picture from static.independent.co.uk
Rank 61199 -
Picture from assets2.cbsnewsstatic.com
Rank 61200


