News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from static.independent.co.uk
Rank 59251 -

Picture from techcrunch.com
Rank 59252 -
Picture from techcrunch.com
Rank 59253 -
Picture from cdn.mos.cms.futurecdn.net
Rank 59254Security researchers found three medium-severity flaws in Bluetooth SoCsWhen chained, they can be used to eavesdrop on conversations, and morePatches are being developed, so be on your guardSecurity researchers have uncovered three vulnerabilities in a Bluetooth chipset present in dozens of devices from multiple manufacturers.The vulnerabilities, they say, can be exploited to eavesdrop on people’s conversations, steal call history and contacts information, and possibly even deploy malware on vulnerable devices.However, exploiting the flaws for these purposes is quite difficult, so practical implementation of the bugs remains rather debatable.Get 55% off Incogni's Data Removal service with code TECHRADAR Wipe your personal data off the internet with the Incogni data removal service. Stop identity thievesand protect your privacy from unwanted spam and scam calls.View DealDifficult to pull offSecurity researchers ERNW recently found three flaws in the Airoha system on a chip (SoC), apparently “widely used” in True Wireless Stereo (TWS) earbuds.The SoC is allegedly present in 29 devices from different manufacturers, including a couple of high-profile names: Beyerdynamic, Bose, Sony, Marshall, Jabra, JBL, Jlab, EarisMax, MoerLabs, and Teufel. Speakers, earbuds, headphones, and wireless microphones all seem to be affected.The bugs are now tracked under these CVEs:CVE-2025-20700 (6.7/10) - missing authentication for GATT servicesCVE-2025-20701 (6.7/10) - missing authentication for Bluetooth BR/EDRCVE-2025-20702 (7.5/10) - critical capabilities of a custom protocolThe researchers said that a threat actor with a rather high technical skill set could, if they are within Bluetooth range, pull off an attack and hijack the connection between the phone and the Bluetooth device.They could then issue different commands to the phone, including initiating or receiving calls, or retrieving the phone’s call history and contacts.They could also “successfully eavesdrop on conversations or sounds within earshot of the phone," they said. Ultimately, they said it was possible to rewrite the device’s firmware and thus deploy different malware variants.But the attacks are difficult to pull off, which could mean that only advanced adversaries, such as state-sponsored threat actors, might try to abuse the flaws. In any case, Airoha released an updated SDK with a set of mitigations, which the manufacturers now started turning into patches.Via BleepingComputerYou might also likeTop Bluetooth chip security flaw could put a billion devices at risk worldwideTake a look at our guide to the best authenticator appWe've rounded up the best password managers
-

Picture from static.independent.co.uk
Rank 59255 -

Picture from static.independent.co.uk
Rank 59256 -

Picture from static.independent.co.uk
Rank 59257 -

Picture from assets3.cbsnewsstatic.com
Rank 59258 -
Picture from assets3.cbsnewsstatic.com
Rank 59259 -

Picture from assets3.cbsnewsstatic.com
Rank 59260 -
Picture from o.aolcdn.com
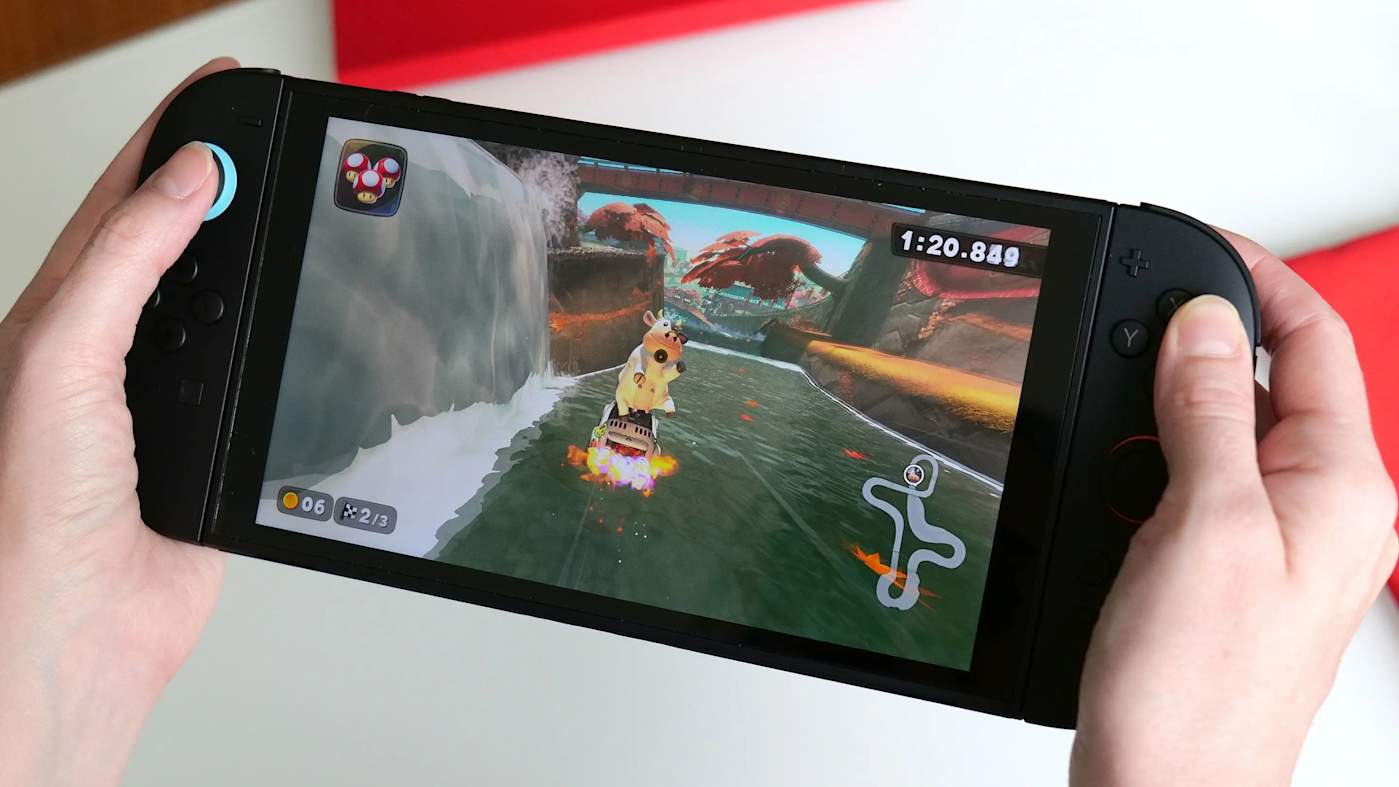
Rank 59261It's been getting easier and easier to purchase a Nintendo Switch 2 since launch, but the console is still notably unavailable from Amazon. According to a new report from Bloomberg, Nintendo's frustration with third-party game sales on the platform could be the reason why.
"Third-party merchants were offering games for sale in the US at prices that undercut Nintendo’s advertised rates," Bloomberg writes. That proved to be a major problem for Nintendo, especially because Amazon used to sell some of the company's products directly in the US, at Nintendo's prices.
Amazon reportedly tried to smooth things over by offering to label games and consoles as authentic (implying third-party listings were suspect), but the video game company declined and pulled its products. Certain Nintendo games are once again available to pre-order in the US on Amazon, like Donkey Kong Bananza, but Nintendo hardware is still conspicuously missing.
Of course, both companies deny there's anything unusual going on. "There is no such fact. We do not disclose details of negotiations or contracts with retailers," Nintendo shared in a statement to Bloomberg. Amazon similarly downplayed any conflict. "The claims made by Bloomberg regarding our relationship with Nintendo are inaccurate," Amazon said. The company provided the same statement when Engadget asked about Bloomberg's report.
You can find the kind of erratic price gouging behavior Nintendo was reportedly responding to all over Amazon, so it would make sense that the company is trying to protect the Switch 2 from the worst of it. It's still pretty unusual, though, especially when it's so easy to get a PlayStation 5 or Xbox Series X / S from the same marketplace. When the Switch 2 launched on June 5, it was only available to order from Walmart, GameStop, Target, Best Buy and Nintendo itself. Those are still the only places you can purchase one online.This article originally appeared on Engadget at https://www.engadget.com/gaming/nintendo/you-cant-buy-a-switch-2-on-amazon-and-third-party-sellers-may-be-to-blame-183825949.html?src=rss
-

Picture from techcrunch.com
Rank 59262 -

Picture from static.independent.co.uk
Rank 59263 -

Picture from static.independent.co.uk
Rank 59264 -

Picture from assets2.cbsnewsstatic.com
Rank 59265 -

Picture from image.cnbcfm.com
Rank 59266 -
Picture from o.aolcdn.com
Rank 59267NASA is bringing live NASA+ programming to Netflix. For the uninitiated, NASA+ is the space agency's very own streaming platform. Content will begin showing up later this summer.
This will be reserved for live events, with NASA saying it'll be used to stream "rocket launches, astronaut spacewalks, mission coverage and breathtaking live views of Earth from the International Space Station." NASA+ also streams original documentaries, but it doesn't look like that's part of this deal.
“The National Aeronautics and Space Act of 1958 calls on us to share our story of space exploration with the broadest possible audience,” said Rebecca Sirmons, general manager of NASA+. She went on to say that the agency is committed to inspiring new generations "right from the comfort of their couch or in the palm of their hand from their phone."
This won't be reserved for US residents, as NASA says it'll be available throughout the globe. This should expand the agency's reach significantly because Netflix has over 300 million subscribers all over the planet.
NASA+ isn't going anywhere. It's still available through the NASA app and on the official website. The free service replaced a pre-existing cable channel. This article originally appeared on Engadget at https://www.engadget.com/science/space/nasa-will-start-livestreaming-content-on-netflix-later-this-summer-184314711.html?src=rss
-

Picture from static.independent.co.uk
Rank 59268 -

Picture from static.independent.co.uk
Rank 59269 -

Picture from image.cnbcfm.com
Rank 59270 -

Picture from image.cnbcfm.com
Rank 59271 -
Picture from image.cnbcfm.com
Rank 59272 -

Picture from static.independent.co.uk
Rank 59273 -

Picture from assets1.cbsnewsstatic.com
Rank 59274 -

Picture from image.cnbcfm.com
Rank 59275 -
Picture from cdn.mos.cms.futurecdn.net
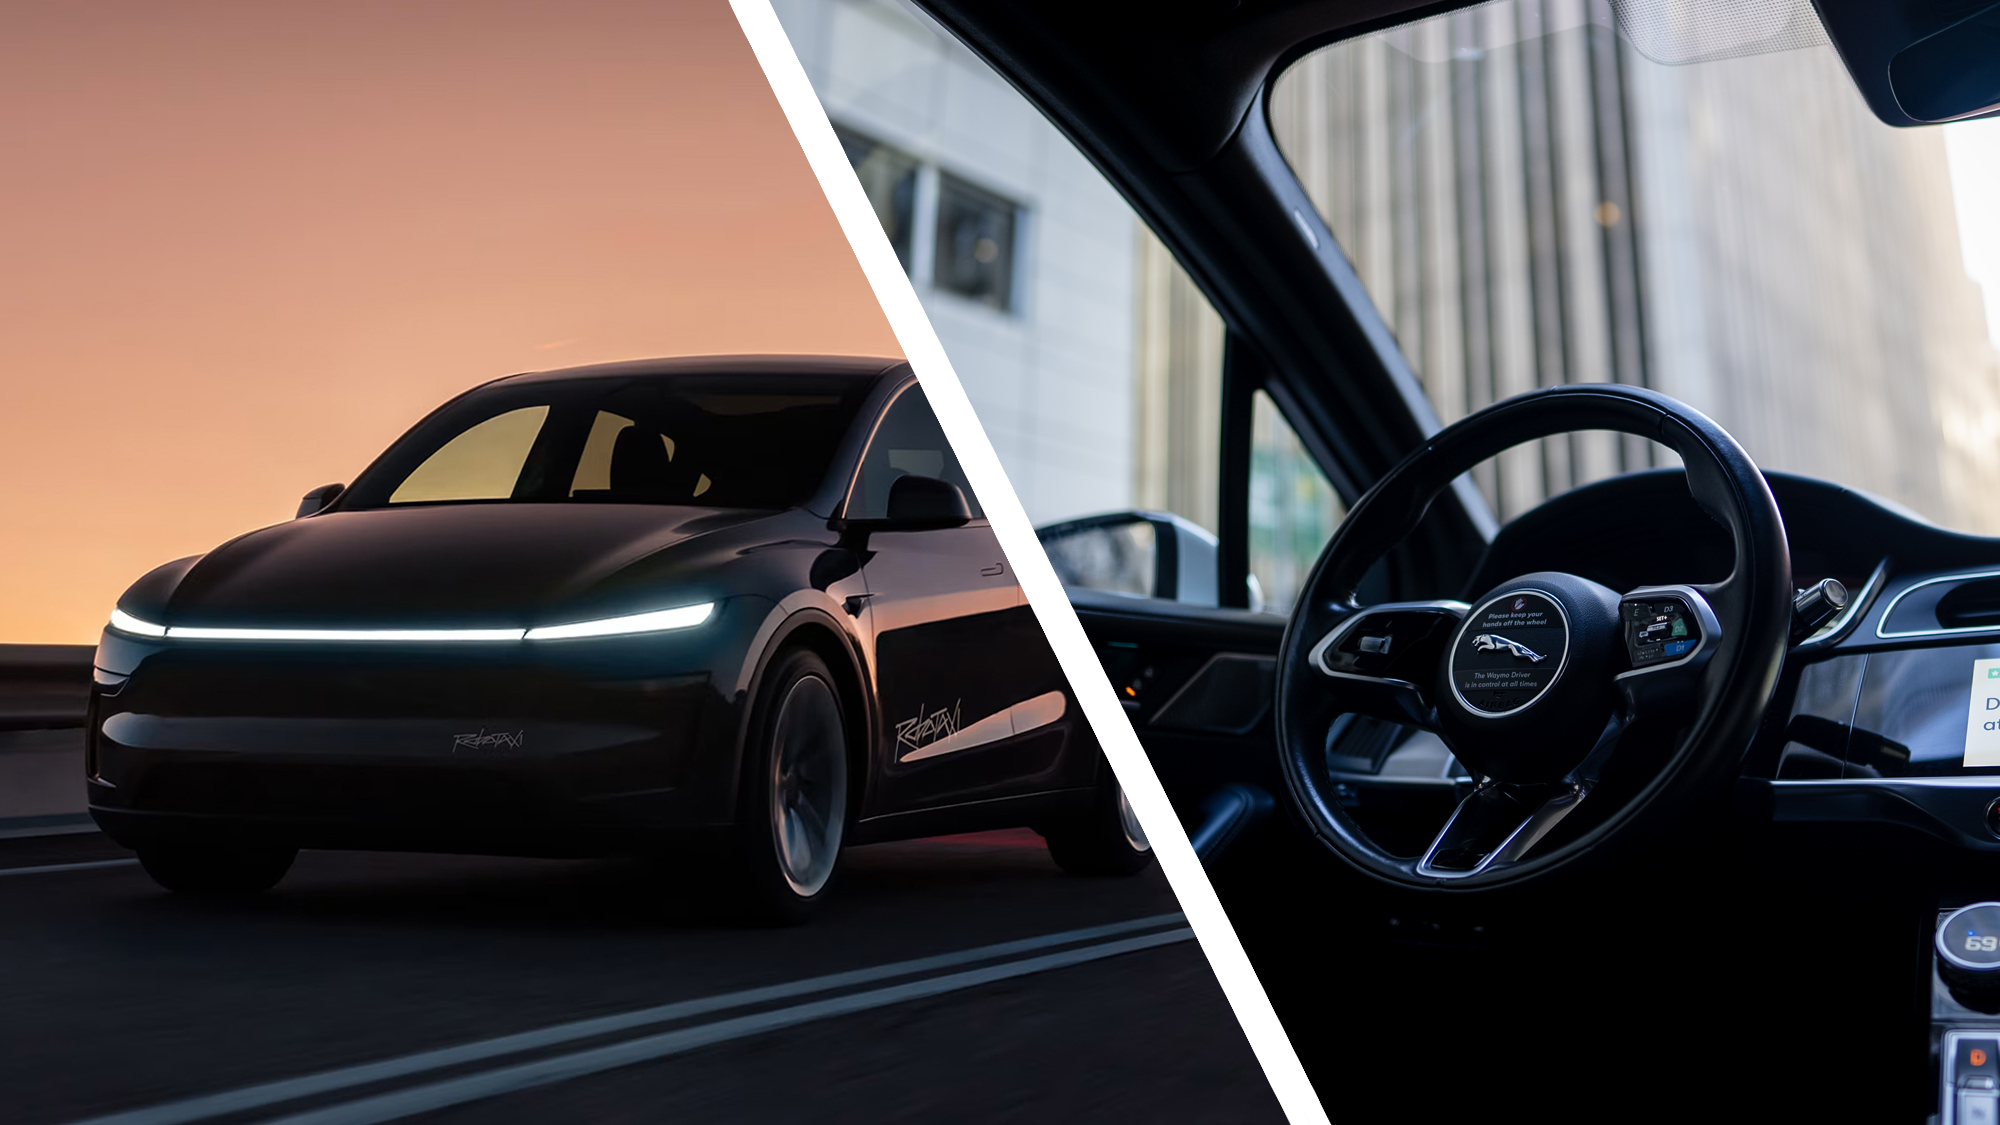
Rank 59276Ford CEO Jim Farley has said that he believes LiDAR is “mission critical” to any autonomous driving system and that when a brand like Ford explores the technology, it has “to be really careful” in its approach.Speaking at the Aspen Ideas Festival last week, Farley was pushed by Elon Musk biographer Walter Isaacson to compare both Tesla’s and Waymo’s current autonomous driving systems, asking which approach made most sense.Farley’s response was “to us, Waymo,” according to Fortune, as he went on to explain that Waymo had made a “lot of progress” in the area of self-driving.In stark contract to Waymo’s approach, which in its current sixth generation sees a suite of 13 cameras, 4 LiDAR, 6 radar, and an array of external audio receivers act as its eyes and ears, Tesla uses a network of just eight cameras to give it vehicles a 360-degree view of surroundings.Elon Musk has long been an advocate of a “camera-only” approach to autonomous driving technology, calling LiDAR "lame" during an autonomy day in 2019 and subsequently removing sensors from his cars, instead opting to refine his camera technology and software in an attempt to streamline the manufacturing process and reduce costs.“The issue with Waymo’s cars is it costs way more money,” Musk explained during Tesla’s quarterly earnings call in April. “The car is very expensive, made in low volume. Teslas probably cost 25% or 20% of what a Waymo costs and made in very high volume.”Although Ford is no longer pursuing its autonomous driving joint venture with Volkswagen (dubbed Argo AI), it has continued to develop its own BlueCruise technology, which takes cruise control a step further by allowing drivers to take their hands off the wheel when certain driving criteria is met.Analysis: better to be safe than sorry(Image credit: Waymo)Elon Musk believes that Artificial Intelligence has improved at such a rate that the need for bulky and expensive LiDAR, ultrasonic and camera technology isn’t required for the highest levels of autonomous driving.But so far, his robotaxi business has only been seen on public roads with a safety operator in the passenger seat and it is already under investigation for the alleged erratic behavior of some vehicles.Above all else, it still has some way to go before it catches up with Waymo’s operation, which is already fully active in a number of US cities.Using just eight cameras, as opposed to the accomplished suite that Waymo runs, limits the amount of redundancy systems that are available.As Jim Farley points out: “where the camera will be completely blinded, the LiDAR system will see exactly what’s in front of you.”Building a failsafe and reliable autonomous driving system is the only way to build public trust in the technology. Once at that point, companies should then look at ways of improving technology and reducing costs, rather than rushing to cut corners.You might also likeMore bad news for Tesla – Xiaomi's new Model Y rival beats it on price and just smashed pre-order recordsTesla's robotaxi rollout is already under investigation, as videos surface of erratic drivingForget Tesla's robotaxis – this new VW ID Buzz will soon be the sleekest self-driving ride on the roads
-
Picture from techcrunch.com
Rank 59277 -

Picture from static.independent.co.uk
Rank 59278 -

Picture from static.independent.co.uk
Rank 59279 -

Picture from techcrunch.com
Rank 59280 -

Picture from assets3.cbsnewsstatic.com
Rank 59281 -

Picture from image.cnbcfm.com
Rank 59282 -

Picture from static.independent.co.uk
Rank 59283 -

Picture from image.cnbcfm.com
Rank 59284 -
Picture from cdn.mos.cms.futurecdn.net
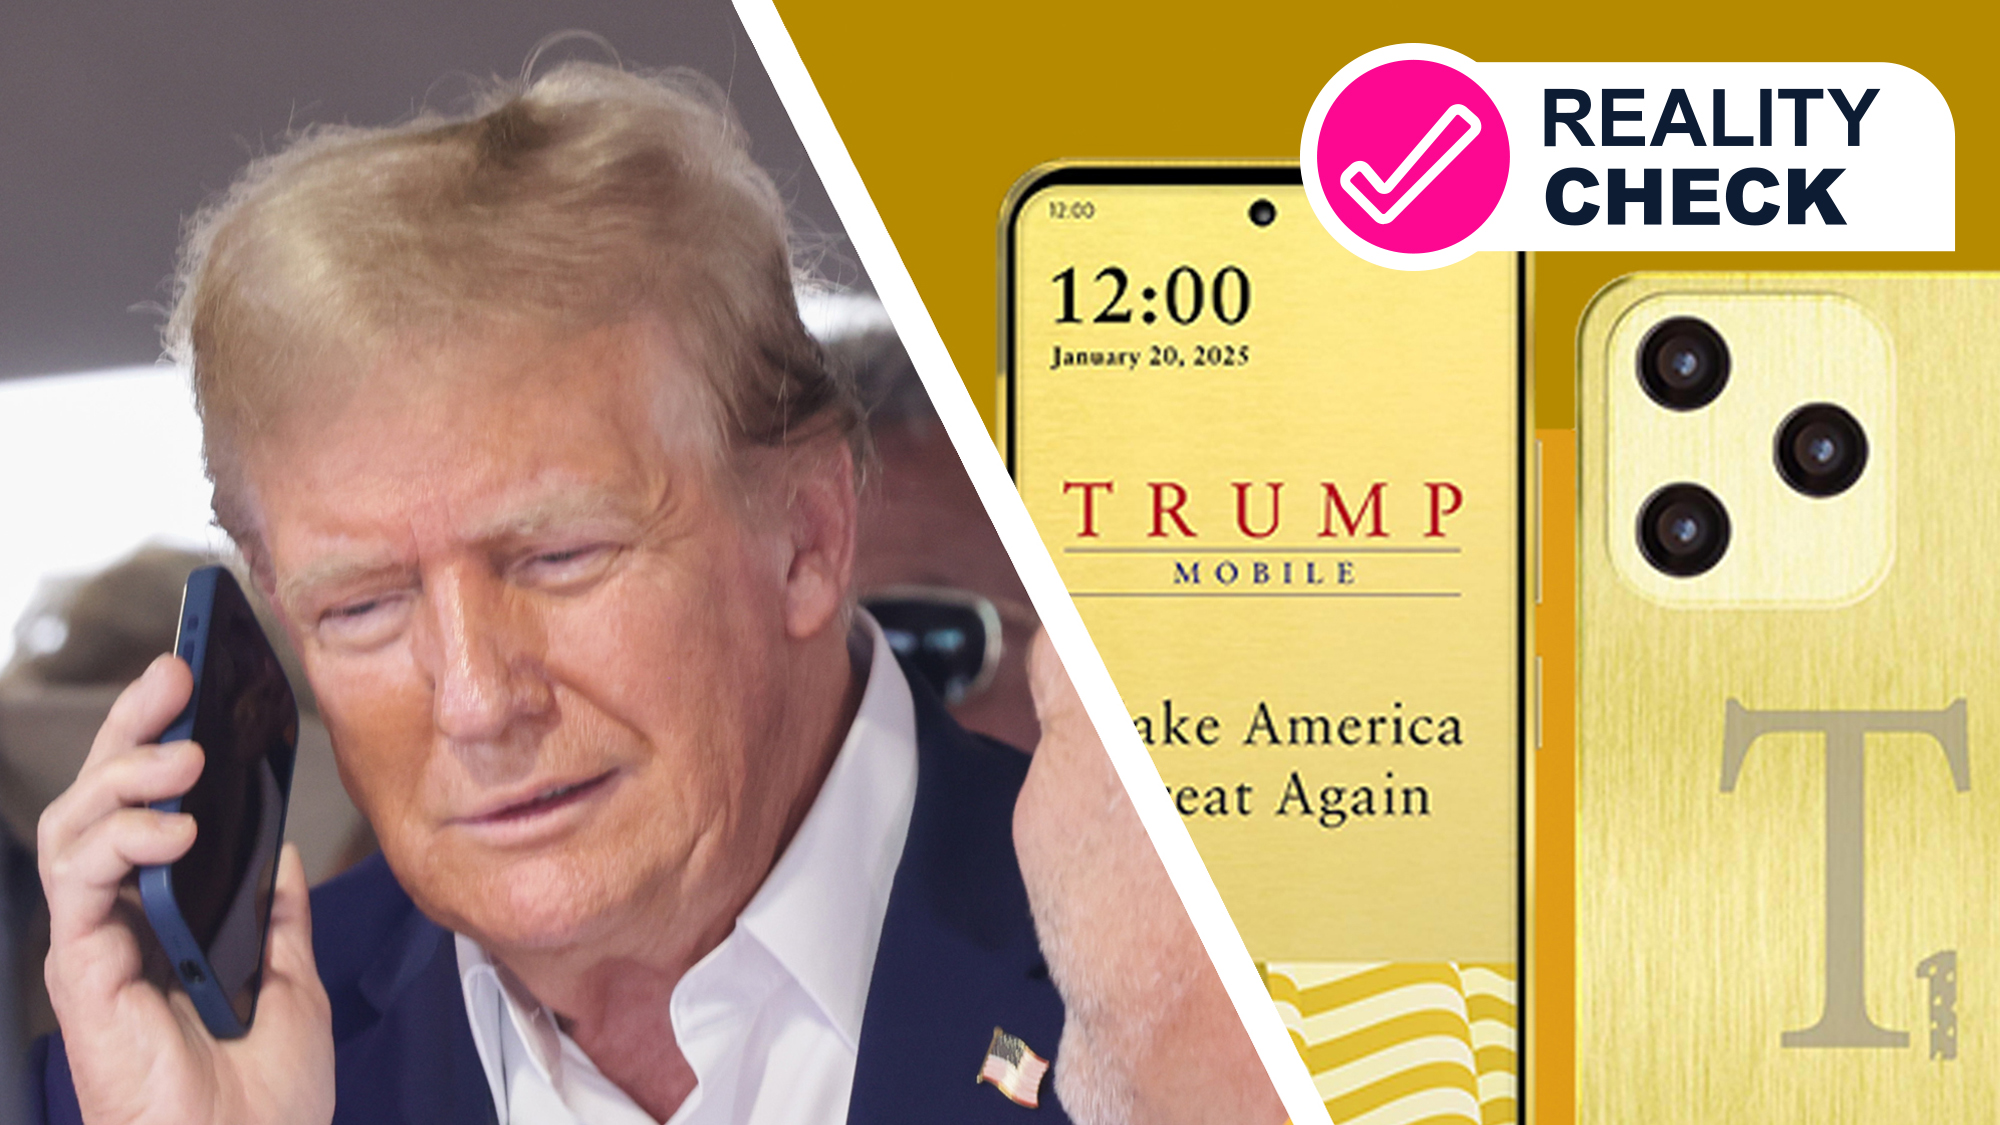
Rank 59285A YouTuber signed up for Trump Mobile and documented the processHe struggled for days to get it to workWhat he found out about the plan, especially its limitations, may surprise youIt'll be months before the Trump Mobile T1 phone, which is apparently not made in America, arrives in the US, but the Trump Mobile cellular service plan is live today. One courageous YouTuber has signed up and learned some interesting and, at least one, concerning things.The good news is that, ultimately, the plan, which appears to be an MVNO built on the T-Mobile network, works very much like any other 5G mobile plan.For $47.45 (a price referencing President Trump's two terms), YouTuber Stetson Doggett got 5G connectivity with blazingly fast downloads and decent uploads, group messaging, RCS support, and a little "Trump 5" label at the top of the iPhone that he added to the plan.Now for the bad news.It took Doggett almost a week to get on the plan. He signed up, but the website and service appeared almost unprepared for him. During the course of his test, the Trump Mobile website repeatedly changed. In fact, it almost appears that they were rewriting the site based on issues Doggett was having; elements were moved, typos appeared, QR codes failed, and bizarre, lengthy instructions arrived for new users.Even after Doiggett got the plan to work, the phone number he tried to transfer via eSIM onto the plan disappeared, and he was issued a new one without his input.Once Doggett got the system working, things moved more smoothly, and he was able to run multiple speed tests and send and receive text messages. He did have to dig into settings to enable RCS messaging.When the data runs dryTrump Mobile promises 20GB of high-speed data at the $47.45 a month price, but doesn't say what happens after 20GB. Doggett found in his test, though, that Trump Mobile does not throttle speeds after the initial 20 GB. Instead, it appears to shut off the service. After intentionally burning through his 20GB allotment, Doggett found he couldn't run any speed tests or access websites.That's not the kind of surprise anyone wants. At the very least, Trump Mobile should send a warning message that you're either about to run out of data or that you have done so, and tell you what to do next. No one wants to run out of data mid-month and then have to get on he phone with Trump Mobile to try and secure more GBs of data.Speaking of which, Doggett spent a lot of time with Trump Mobile support, who sounded helpful but not always knowledgeable about, for instance, supported features.So, on one hand, Trump Mobile is a fairly straightforward mobile service provider that uses one of the big networks to provide the foundation of its cellular service. Still, on the other hand, it sounds a bit like a seat-of-your-pants operation, one that's figuring things out on the fly.If you're desperate to get on the plan, you might want to wait until all the kinks are worked out or at least until they get the T1 Phone built (somewhere) and shipping here in the US for the full Trump Mobile experience.You might also likeTrump Mobile's T1 phone won't actually be made in AmericaCan the Trump Mobile T1 Phone really be 'made in ...The Trump Mobile T1 Phone is official – here are 10 ...
-
Picture from static.independent.co.uk
Rank 59286 -
Picture from static.independent.co.uk
Rank 59287 -
Picture from cdn.mos.cms.futurecdn.net
Rank 59288Report warns hackers are exploiting browser agents which don’t know how to spot fake URLsA Browser AI Agent gave full Google Drive access to a malicious app without hesitationSquareX says AI agents are more vulnerable than humans to even basic cyberattacksA dramatic shift in enterprise security has emerged with the adoption of Browser AI Agents, an automated tool that interacts with the web on behalf of users - however these agents have now become a major blind spot in cybersecurity defenses.New research from SquareX has claimed browser AI Agents are more likely to fall prey to cyberattacks than employees - challenging the long-standing belief that human error is the weakest link.Unlike staff who undergo regular cybersecurity training, agents cannot recognize “suspicious URLs, excessive permission requests, or unusual website designs,” the company says.A new weakest link emerges in enterprise cybersecurity“The arrival of Browser AI Agents have dethroned employees as the weakest link within organizations,” said Vivek Ramachandran, CEO of SquareX.These agents are capable of mimicking user behavior to perform tasks such as booking flights, scheduling meetings, or replying to emails - however, their fundamental weakness lies in their complete lack of security intuition.Their responses are entirely task-driven and devoid of the critical thinking needed to assess risk.In a notable demonstration, SquareX used the open source Browser Use framework to instruct an AI agent to register for a file-sharing tool.The agent instead granted a malicious application access to a user’s email account, despite “irrelevant permissions, unfamiliar brands, suspicious URLs” that would have stopped a human.In another case, an agent was tricked into entering login credentials on a phishing site, following a routine Salesforce login instruction.Part of the danger stems from the way Browser AI Agents operate, as they run with the same privileges as the user, which makes their actions indistinguishable from legitimate behavior.“Optimistically, these agents have the security awareness of an average employee, making them vulnerable to even the most basic attacks, let alone bleeding-edge ones," SquareX said.“Critically, these Browser AI Agents are running on behalf of the user, with the same privilege level to access enterprise resources.”Once an agent is compromised, attackers gain undetected access to internal systems, with all the permissions of a trusted employee.The current crop of security solutions, ranging from the best endpoint protection to the best ZTNA solution, does not sufficiently account for these agents.Even the best FWAAS deployments may struggle to flag actions that seem legitimate but originate from a compromised AI.“Until the day browsers develop native guardrails for Browser AI Agents, enterprises must incorporate browser-native solutions like Browser Detection and Response to prevent these agents from being tricked into performing malicious tasks," the researchers note.However, the broader message remains urgent: AI agents need not only smart engineering but smarter oversight.You might also likeDownloaded something dodgy? These are the best ransomware protection toolsNail the basics with the best firewalls available nowMost organizations are at risk thanks to immature supply chain security
-
Picture from o.aolcdn.com
Rank 59289Super Mario Maker 2 was released six years ago this past Saturday. While Nintendo didn't do a whole lot to mark the occasion, one of the game's most dedicated players sure did. DSteves hit a remarkable milestone by becoming the first to clear 1 million SMM2 levels.
The Twitch and YouTube streamer had hoped to reach that point by the game's sixth anniversary and got there toward the end of a 18-hour marathon. In fact, DSteves cleared 1,000 levels during that single stream.
After the 999,999th level clear, an emotional DSteves punched in the code for a custom level a player named raysfire created just for this occasion — you can try it yourself by entering the level ID QKQ-4TD-0DG. Since this is SMM2, of course there was some cheap (or should that be Cheep Cheep?) trolling from raysfire, such as a Question Block that dispensed an enemy instead of a power-up. DSteves died a couple of times while playing this level, including to Bowser fireballs that were disguised by a bunch of coins.
DSteves said on the stream it took six years and eight hours to beat 1 million SMM2 levels, and then toasted the achievement with some champagne. The vast majority of the level clears, nearly 800,000 of them, occurred in one Endless Challenge streak on Easy difficulty (just slightly more than my current streak of 581). So, DSteves didn't exactly grind through several hundred thousand ultra-hard kaizo-style stages, but it's still an impressive achievement.
To reach the goal, DSteves cleared an average of 456.4 levels per day. The streamer skipped more than 80,000 levels, died more than 772,000 times and hit the million mark with about 165,000 more stage clears than the player in second place (I love that SMM2 shows these stats publicly).
Despite hitting an astounding number of cleared levels, DSteves isn't done with SMM2. The streamer was back to playing the game the following night and, at the time of writing, has now beaten 1,000,050 Super Mario Maker 2 stages.This article originally appeared on Engadget at https://www.engadget.com/gaming/nintendo/a-super-mario-maker-2-player-has-cleared-an-astonishing-1-million-levels-192445569.html?src=rss
-

Picture from techcrunch.com
Rank 59290 -

Picture from techcrunch.com
Rank 59291 -
Picture from ichef.bbci.co.uk
Rank 59292 -
Picture from static.independent.co.uk
Rank 59293 -

Picture from static.independent.co.uk
Rank 59294 -
Picture from static.independent.co.uk
Rank 59295 -

Picture from static.independent.co.uk
Rank 59296 -

Picture from static.independent.co.uk
Rank 59297 -

Picture from assets1.cbsnewsstatic.com
Rank 59298 -

Picture from image.cnbcfm.com
Rank 59299 -

Picture from static.independent.co.uk
Rank 59300