News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from static.independent.co.uk
Rank 54301 -
Picture from static.independent.co.uk
Rank 54302 -

Picture from static.independent.co.uk
Rank 54303 -

Picture from static.independent.co.uk
Rank 54304 -

Picture from ichef.bbci.co.uk
Rank 54305 -

Picture from static.independent.co.uk
Rank 54306 -

Picture from static.independent.co.uk
Rank 54307 -

Picture from ichef.bbci.co.uk
Rank 54308 -

Picture from static.independent.co.uk
Rank 54309 -

Picture from ichef.bbci.co.uk
Rank 54310 -
Picture from static.independent.co.uk
Rank 54311 -

Picture from static.independent.co.uk
Rank 54312 -

Picture from image.cnbcfm.com
Rank 54313 -

Picture from static.independent.co.uk
Rank 54314 -

Picture from static.independent.co.uk
Rank 54315 -

Picture from static.independent.co.uk
Rank 54316 -

Picture from static.independent.co.uk
Rank 54317 -

Picture from static.independent.co.uk
Rank 54318 -

Picture from ichef.bbci.co.uk
Rank 54319 -

Picture from ichef.bbci.co.uk
Rank 54320 -

Picture from static.independent.co.uk
Rank 54321 -
Picture from static.independent.co.uk
Rank 54322 -

Picture from static.independent.co.uk
Rank 54323 -

Picture from static.independent.co.uk
Rank 54324 -

Picture from assets2.cbsnewsstatic.com
Rank 54325 -
Picture from ichef.bbci.co.uk
Rank 54326 -
Picture from ichef.bbci.co.uk
Rank 54327 -

Picture from static.independent.co.uk
Rank 54328 -

Picture from static.independent.co.uk
Rank 54329 -
Picture from cdn.mos.cms.futurecdn.net
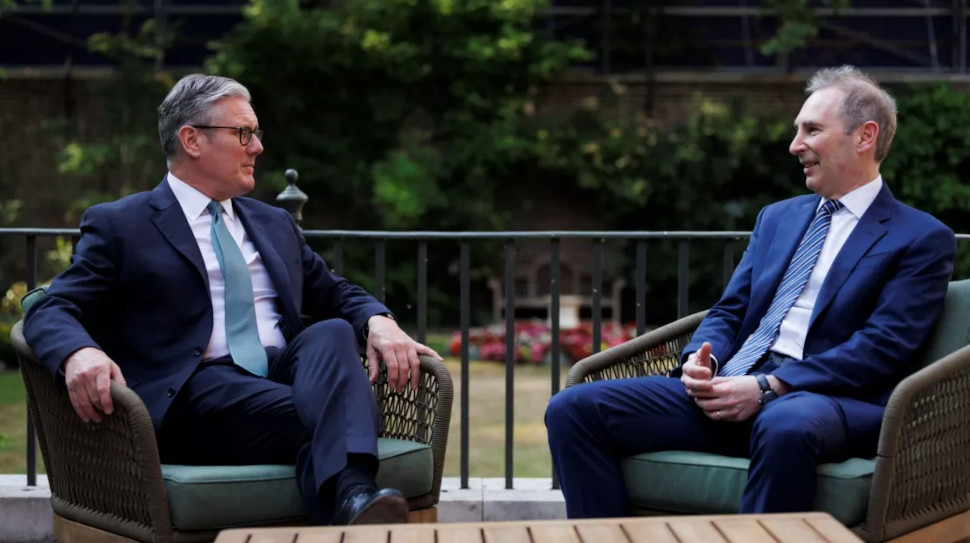
Rank 54330Amazon's three-year plan includes £40 billion in UK investment"Thousands" of jobs set to be created across new and upgraded sitesMost of the benefits will be seen in regions typically overlooked by such investmentsAmazon has announced plans to invest £40 billion into the UK over a three-year period spanning between 2025 and 2027.The multi-billion pound investment will fund the expansion of Amazon's operations within the UK, leading to more jobs, boosting national GDP and strengthening the infrastructure that Amazon relies on (and therefore other UK consumers and businesses).The huge sum isn't insignificant – the UK is Amazon's third-largest market, after the US and Germany, two nations that have already seen billions in investments spanning both ecommerce infrastructure and sovereign cloud efforts.UK Amazon investmentBoasting of its position as a top-10 private sector employer across the UK, with more than 75,000 citizens part of its workforce, Amazon said its latest investment would create thousands more jobs, the "vast majority" of which should be away from London and the South East.Four new Amazon fulfilment centers are in the pipeline, including two in the East Midlands, one in Hull and a further one in Northampton - with the latter two anticipated to generate 2,000 jobs each.The company also declared its investment would be nearly matched when it comes to boosting the UK's GDP, which Amazon anticipates adding £38 billion to the UK economy.Besides adding further delivery stations across the UK, Amazon also plans to upgrade more than 100 operational buildings and open two more at its East London corporate HQ.Promising a minimum salary of £28,000 for full-time workers (and £30,000 in London), robotics technicians, safety experts and mechatronic engineers will be among the more than 60 roles offered by the company as part of its huge investment."When Amazon invests, it’s not only in London and the South East – we’re bringing innovation and job creation to communities throughout England, Wales, Scotland, and Northern Ireland, strengthening the UK’s economy and delivering better experiences for customers wherever they live," noted Amazon CEO Andy Jassy.UK Prime Minister Keir Starmer welcomed the "thousands of new jobs," which he described as offering "real opportunities for people in every corner of the country to build careers, learn new skills, and support their families."“Amazon’s £40 billion investment adds another major win to Britain’s basket and is a massive vote of confidence in the UK as the best place to do business.," he added.You might also likeFancy a change? Here are the best job sitesLearn new skills with the best online learning platformsAmazon is planning one of its biggest cloud investments yet as it goes big down under
-
Picture from cdn.mos.cms.futurecdn.net
Rank 54331The cybersecurity profession is always on high alert for new attack tactics as criminal groups adapt to overcome improved defenses against phishing and ransomware. But alongside the new innovations, some old-school tactics appear to be evolving making a comeback – or rather they never quite went away.Document-borne malware is one such tactic. Once considered a relic of early cyber warfare, this method continues to pose a significant threat, particularly for organizations handling large volumes of sensitive information, such as those in critical infrastructure.The appeal for attackers is clear. Everyday files - Word documents, PDFs, Excel spreadsheets - are inherently trusted and flow freely between businesses, often through cloud-based platforms. With modern security more focused on endpoints, networks, and email filtering, these seemingly mundane files can act as the ideal Trojan horse.Understanding this evolving risk is key to stopping seemingly innocuous documents before they can wreak havoc.Why are cybercriminals still using document-borne malware?On the surface, attacks using malicious documents feel like a bit of a throwback. It’s a tactic that’s been around for decades at this point, however, that doesn’t make it any less dangerous for organizations.Still, while the concept is nothing new, threat groups are modernizing it to keep it fresh and bypass standard security controls. This means the seemingly old-school tactic is still a threat even for the most security-conscious sectors.As with other email-based tactics, attackers typically seek to hide in plain sight. Most attacks use common file types such as PDFs, Word documents, and Excel spreadsheets as malware carriers. The malware is usually hidden in macros, embedded in scripts such as JavaScript within PDFs, or hidden with obfuscated file formats and layers of encryption and archiving.These unassuming files are coupled with popular social engineering techniques, such as a supplier invoice or customer submission form. Email attack tactics, such as spoofed addresses or compromised accounts, further camouflage the malicious content.The rise of cloud-based collaboration tools has increased the attack surface. We’re all used to receiving any number of emails throughout the day with links to SharePoint, Google Docs, and other common platforms. This makes it harder to detect malicious files before they enter networks.What makes document-borne malware particularly dangerous for critical infrastructure? Most attacks seek to breach networks unnoticed to maximize their impact and eventual rewards. The potential gains for exfiltrating sensitive data or shutting down a system means groups are willing to invest more time and resources in trying new tactics that can pass unnoticed.Further, document-borne attacks are all about blending into the background. For example, in the financial sector, the ecosystem offers plenty of opportunities with the thousands of incoming documents from customers, suppliers, and partners daily. Most firms have a constant inflow of financial statements, loan applications, compliance paperwork, and myriad other files entering their system.If opened, a single malicious document can spread malware across critical networks. Attackers leverage document-based threats to deploy ransomware, steal credentials, or exfiltrate sensitive data, so one wrong click can come with catastrophic consequences, especially for critical sectors that rely heavily on a reputation for trust and reliability.Strict regulatory compliance demands can raise the stakes further and, depending on their region and function, firms could fall under the remit of the GDPR, DORA, NIS2, and more. Failing to meet these demands can result in severe financial penalties and a significant blow to the firm’s reputation.Why are organizations struggling to defend against these threats? From our experience, document security is often overlooked in favor of other areas like network perimeter and endpoint protection. Document-borne attacks are mundane enough to slip down the priorities list but advanced enough to defeat most standard security tools.Security teams may lack the visibility or tools to inspect and sanitize every incoming file, particularly in fast-moving digital workflows.There tends to be an over-reliance on signature-based antivirus solutions, which often fail to detect modern document-borne threats. While security teams are typically aware of malicious macros, formats like ActiveX controls, OLE objects, and embedded JavaScript may not be on the radar.Attackers have also latched onto the fact there is a significant mental blind spot around documents seemingly delivered through familiar cloud-based channels. Even when employees have received phishing awareness training, there is a tendency to automatically trust a document coming in through an expected source like Google or Office 365.What steps should businesses take to mitigate document-borne malware risks? As with most evolving cyberattack tactics, a multi-layered strategy is the key to fending off document-borne threats.One key step is adopting a multi-engine approach to malware scanning. While threat actors may be able to fool one detection engine, having multiple different tools will improve the chances of catching hidden malware and reduce false negatives.Content Disarm and Reconstruction (CDR) tools are another important element. These sanitize and remove malicious macros, scripts, and active content while preserving document integrity. Suspect files can then be run through advanced standboxes to identify previously unknown threats by detecting their malicious behavior whilst in a contained environment.The network should also be set with strict file policies, restricting high-risk file types and enforcing user authentication before document uploads. Setting file size limits can also help catch malicious documents where hidden code has made them larger than normal.Efficiency and reliability are also key here. Organizations need to be able to identify malicious documents hiding in their typical incoming traffic, but without disrupting a workflow that customers expect to be fast and consistent.Stronger email security measures will also help to detect and block malicious attachments before they reach users. Moving away from signature-based detection and towards behavioral analytics will improve the chances of catching out attackers posing as trusted contacts and services.Including document-based threats in employee awareness efforts will also help staff spot signs like unexpected macros and spoofed invoices in case they make it through other measures. In particular, more scrutiny is needed for files shared through cloud platforms.Companies should adopt a zero trust mindset, treating every incoming file as a potential threat until it has been scanned and sanitized.We list the best document management software.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-
Picture from ichef.bbci.co.uk
Rank 54332 -

Picture from static.independent.co.uk
Rank 54333 -

Picture from static.independent.co.uk
Rank 54334 -

Picture from static.independent.co.uk
Rank 54335 -

Picture from static.independent.co.uk
Rank 54336 -

Picture from static.independent.co.uk
Rank 54337 -

Picture from static.independent.co.uk
Rank 54338 -

Picture from static.independent.co.uk
Rank 54339 -

Picture from image.cnbcfm.com
Rank 54340 -

Picture from static.independent.co.uk
Rank 54341 -
Picture from cdn.mos.cms.futurecdn.net
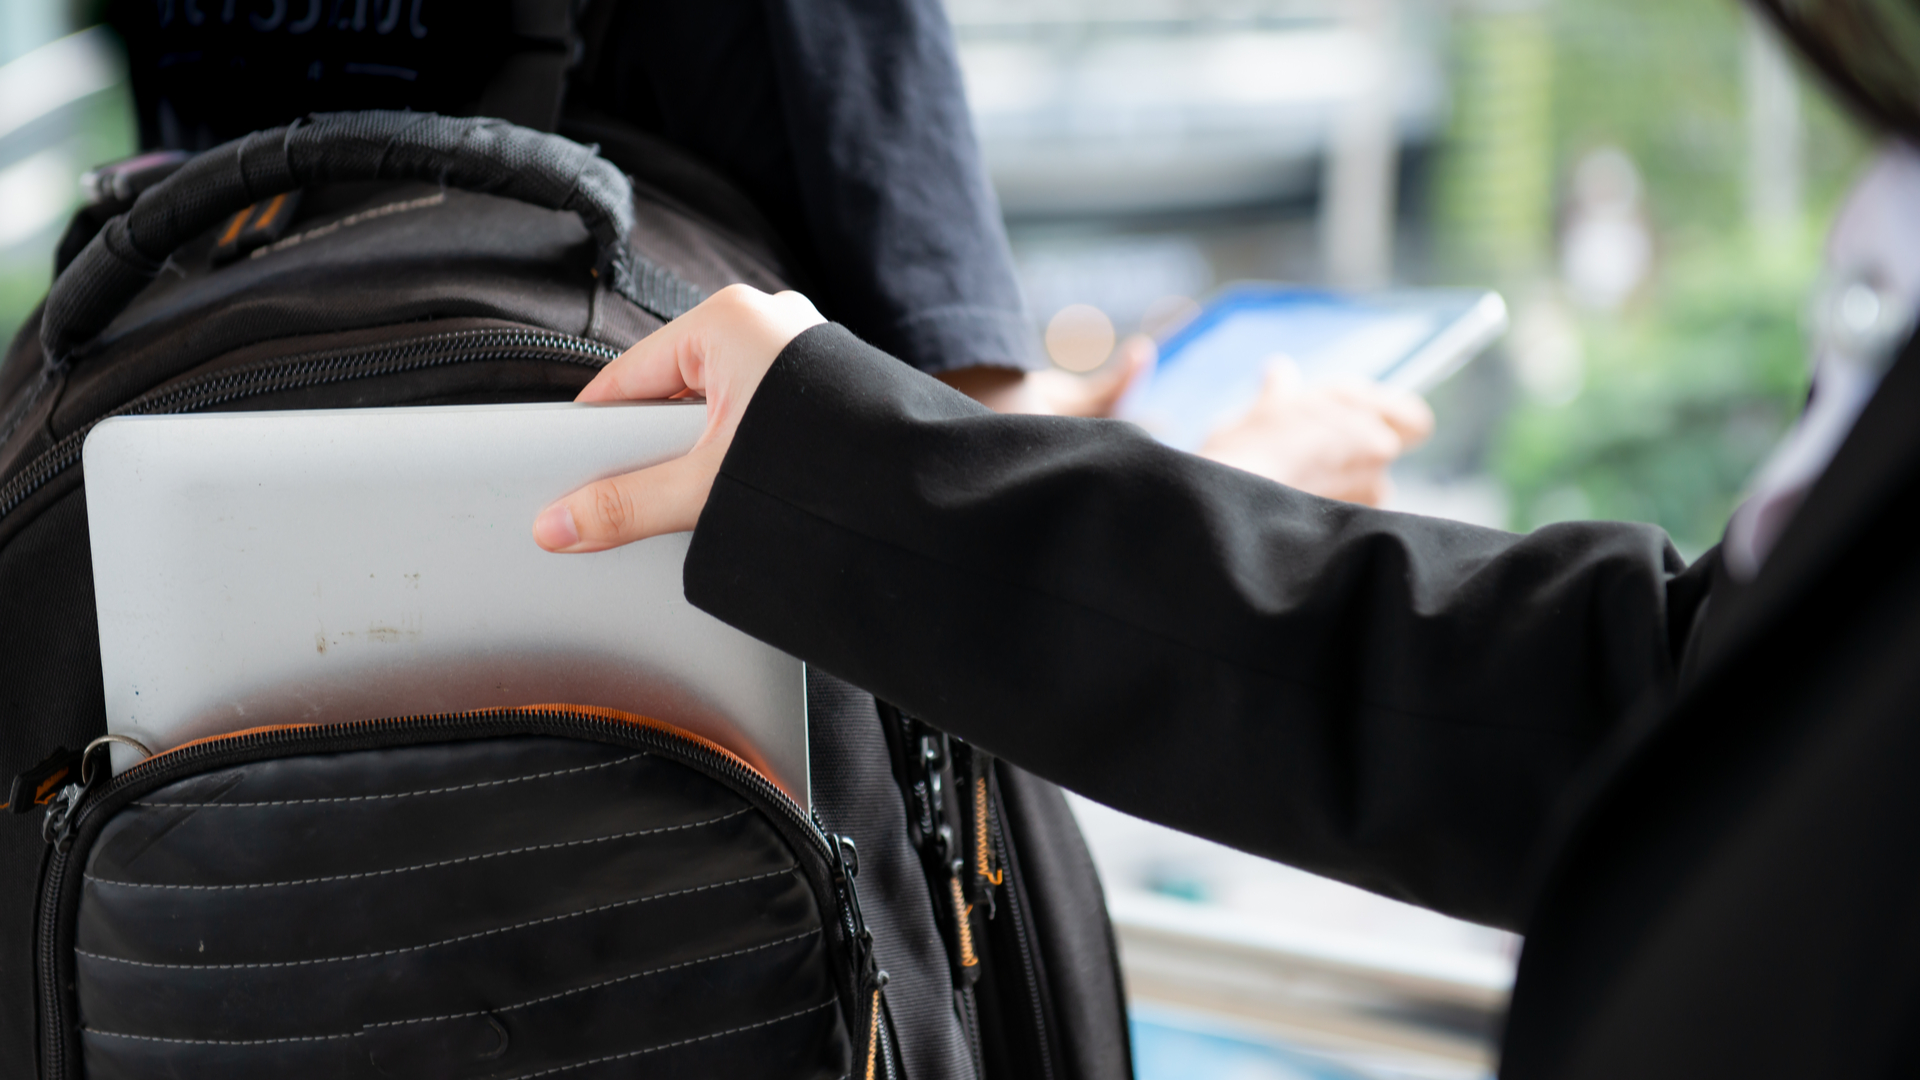
Rank 54342Device loss from UK governmental departments tops 2000 in just one yearExperts fear stolen devices could provide entry points for hackers Phone and tablet thefts pose risk despite widespread encryptionHave you ever lost a phone or computer and worried about what someone might find on it?Thousands of devices have gone missing from UK government departments in the past year, raising serious concerns about cybersecurity and data protection.Analysis by The Guardian, based on freedom of information disclosures, found the government lost over 2,000 laptops, phones and tablets in the past 12 months, with a replacement cost estimated at around £1.3m.Surprisingly large numbersThe Department for Work and Pensions, Ministry of Defence, and the Cabinet Office each reported hundreds of missing tech items.The Ministry of Defence alone recorded 103 missing laptops and 387 phones in just five months of 2025. Other departments affected included HM Treasury, the Bank of England, and the Home Office.“We treat all breaches of security very seriously and we require all suspected breaches to be reported. All incidents are subjected to an initial security risk assessment, with further action taken on a proportionate basis," an MoD spokesperson said.Playing down fears, the defence department added, “Encryption on devices ensures any data is safeguarded and prevents access to the defence network.”This sentiment was echoed by the Bank of England, which said it “takes the security of devices and data very seriously and has suitable protection in place.”The same official line was trotted out by a government spokesperson who said, “We take the security of government devices extremely seriously, which is why items such as laptops and mobile phones are always encrypted so any loss does not compromise security.”Professor Alan Woodward, a cybersecurity expert at the University of Surrey, wasn’t quite so reassured, telling The Guardian, “These are surprisingly large numbers. When you are talking about so many [it creates] a large attack surface [for hackers]. If 1% were system administrators who had their phones stolen, that’s enough to get in.”He added, “If devices were open when stolen, as frequently happens with phones snatched on the street, criminals could keep them open and drill down into the device and once the phone is open, by design it is readable and accessible.”You might also likeI am a cybersec expert and this is why we should be talking more about Data Loss PreventionOver 16 billion records leaked in "unimaginable" major data breachMillions of Brits to be impacted by UK Gov decision to move away from passwords
-

Picture from image.cnbcfm.com
Rank 54343 -

Picture from static.independent.co.uk
Rank 54344 -

Picture from static.independent.co.uk
Rank 54345 -
Rank 54346
-
Picture from static.independent.co.uk
Rank 54347 -

Picture from static.independent.co.uk
Rank 54348 -

Picture from static.independent.co.uk
Rank 54349 -

Picture from static.independent.co.uk
Rank 54350