News
This constantly updated list features the latest and most important news articles, ranked in order of significance. The top stories highlight major developments, breaking news, and critical updates across various topics, ensuring you stay informed about the most pressing issues. As new articles are added, the list adapts to reflect the latest priorities, keeping the most impactful stories at the forefront. Whether it’s global events, technology breakthroughs, or industry trends, this dynamic list ensures you always have access to the most relevant and timely information.
-

Picture from static.independent.co.uk
Rank 53501 -
Picture from ichef.bbci.co.uk
Rank 53502 -

Picture from static.independent.co.uk
Rank 53503 -

Picture from static.independent.co.uk
Rank 53504 -
Picture from assets3.cbsnewsstatic.com
Rank 53505 -

Picture from assets2.cbsnewsstatic.com
Rank 53506 -
Picture from cdn.mos.cms.futurecdn.net
Rank 53507Microsoft Teams is working on variable notification sizesThe new addition should hopefully minimize disruption while workingAll Microsoft Teams users should benefit upon launchBeing distracted by unruly Microsoft Teams pop-ups could soon be a thing of the past, thanks to a new update coming to the service soon.The video conferencing platform has revealed it is working on adding a feature which will allow users to tweak the size of Teams notifications.Once released, this tool should mean users are safe from having distracting pop-ups catch the corner of their eye when working - something I know I've definitely fallen victim to in the past.Microsoft Teams notification sizesIn a Microsoft 365 roadmap post, the company explained the feature will, quite simply, give users the chance to "change the size of Teams notifications".This includes a new "compact" size, which the company says, "takes up less space on the user's screen and offers a clean, minimalist design."That's all the detail we currently have on the feature itself, which we're guessing will be accessible from the Settings menu or preferences list.The feature is listed as being "in development", but has a scheduled rollout start date of July 2025, so users don't have too long to wait. When released, it will be available to users across the world using Teams on Windows, Mac, Android, and iOS.The launch is the latest in a series of recent improvements to Microsoft Teams announced by the company as it looks to improve the experience for users.This includes a tweak that will allow multiple people to control slides being presented in a meeting or call.Microsoft says the addition will mean that presenters are able to maintain "a smooth flow during meetings or webinars" - hopefully meaning the end of manual slide changes - and hopefully, the phrase "next slide please".It also recently announced it would be adding noise suppression for participants dialing in to a call, which should spell an end to potentially ear-splitting call interruptions, or participants being deafened by background noise from another person on the call.The platform also revealed it is rolling out "enhanced spell check", giving users the tools to make sure their messages are as accurate as possible.You might also likeMicrosoft Teams is finally adding a tiny but crucial feature I honestly can't believe it never hadMicrosoft Teams will now let companies block people for good — so you'd better behaveWe've rounded up the best productivity tools around right now
-
Picture from cdn.mos.cms.futurecdn.net
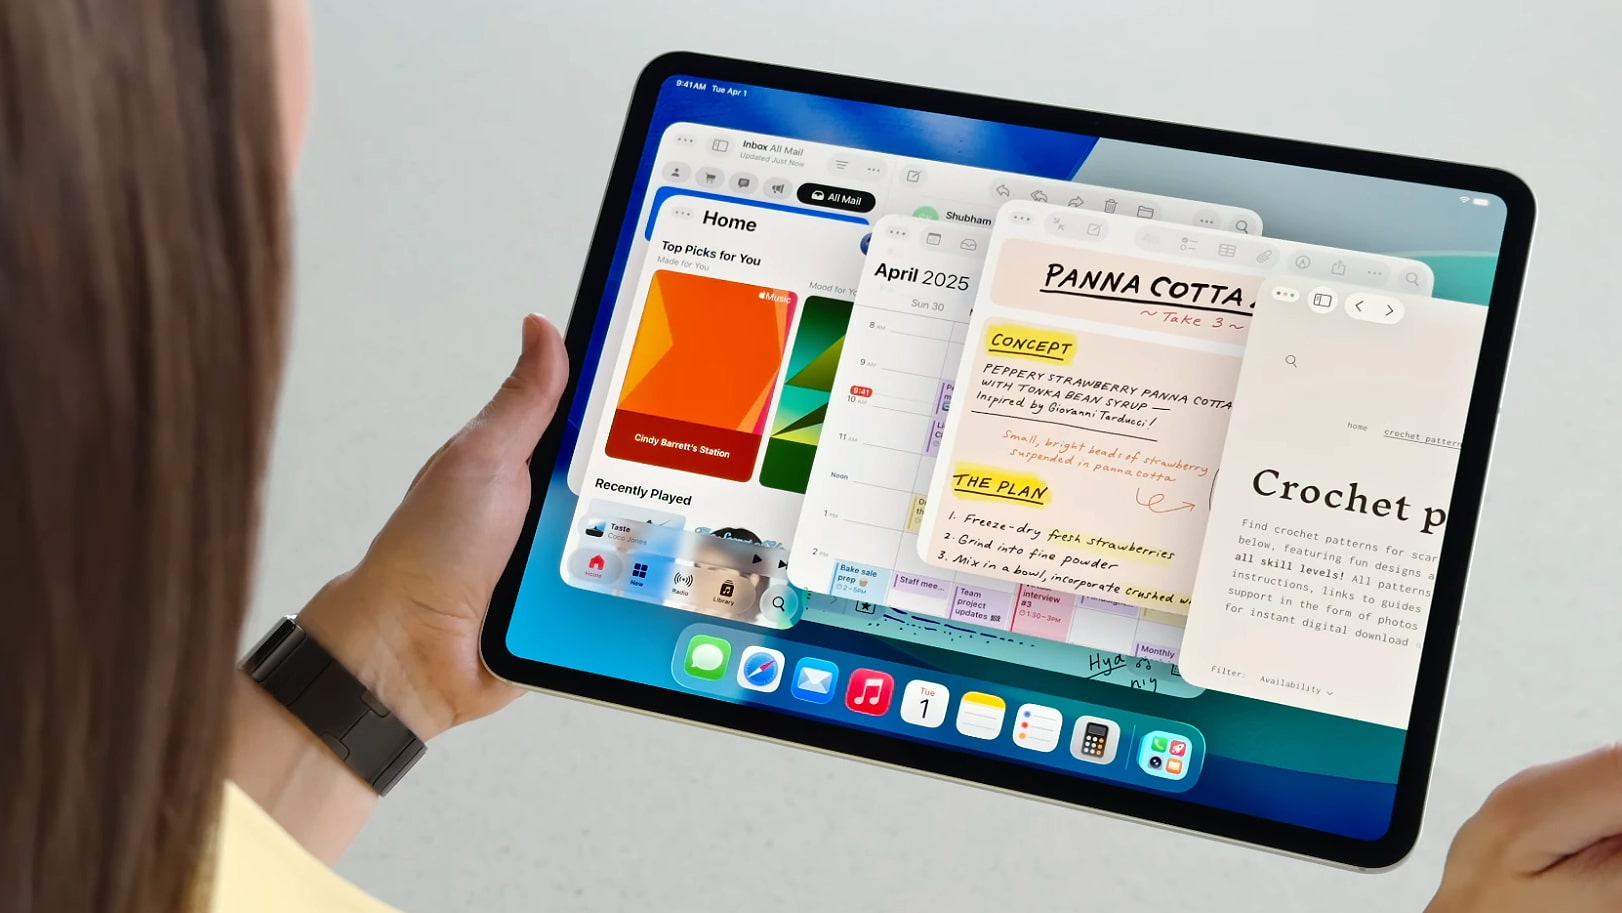
Rank 53508Apple’s Mac-like multitasking feature is coming to these iPads soon – but I prefer these handy toolsiPadOS’s Stage Manager feature is coming to more iPadsThat could improve multitasking capabilities for iPad usersBut iPadOS 26 brings even better features to iPad than Stage ManagerIf you’re a fan of multitasking on any of the best iPads, you were probably heartened to see all the new features Apple brought to iPadOS 26 at its Worldwide Developers Conference (WWDC). But while those additions are sure to make a splash for productivity power users, the company is also extending the existing Stage Manager feature to even more iPads.In case you missed it, Stage Manager lets you group apps into sets and then switch between those sets as needed. It’s designed to help you focus on one task and all the windows you need to complete it, then change to a different task and group of apps after. It’s available on both iPadOS and macOS.With iPadOS 26, Stage Manager will be available on more iPads than before. Previously, it only worked on the 13-inch iPad Pro with M4 chip, the 12.9-inch iPad Pro (third generation or later), the 11-inch iPad Pro (first generation or later), and the iPad Air (fifth generation or later).As noted on Reddit, in addition to those tablets, Stage Manager now also works with the third-generation iPad Air or later (not just the fifth-generation model), the iPad mini (fifth generation or later), and the entry-level iPad (eighth-generation or later). In essence, Stage Manager works with any iPad that can run iPadOS 26.Better than Stage Manager(Image credit: Apple)Stage Manager has proven to be a somewhat divisive feature since it was released – not helped by a buggy launch – and it’s struggled to establish itself as a must-have element of iPadOS. Although I was intrigued by it at first, I quickly found Stage Manager to be a little half-baked, and it never became a regular part of my setup on either my iPad or my Mac.What looks to be far more interesting is the range of productivity tools Apple has added to iPadOS 26. That includes a Mac-like menu bar, full overlapping app support, window resizing, and even the “traffic light” buttons used to close, minimize or maximize app windows. Window tiling in particular is an excellent addition to the iPad, as you get a lot more window position options than just using an older feature like Split View.Being able to use an iPad like a Mac offers much more appeal to me than Stage Manager. That’s partly because the Mac-like interface is just much more familiar to anyone who has used a computer before – there’s no new system to learn, as there is with Stage Manager. And gaining these new tools now makes it much more comfortable to work on the go with my iPad, as I no longer need to sacrifice capability in the name of portability.Still, with Stage Manager coming to more iPads than before, it could still find an audience among Apple fans who have never had access to it. In any case, combined with iPadOS 26’s new multitasking features, it’s clear that Apple is taking productivity and user interface management a little more seriously.You might also like'Our biggest iPadOS release ever' – iPadOS 26 has landed, here are the 10 biggest upgradesDon't call it a Mac – I went hands-on with iPadOS 26, here's what you need to knowHow to use Stage Manager on a Mac in macOS Ventura
-
Picture from cdn.mos.cms.futurecdn.net
Rank 53509The recent 16 billion record breach may not be as bad as it soundsThe datasets most likely contain previously leaked informationNevertheless, those affected could still be at risk, so be on your guardFollowing the recent reports of over 16 billion records being leaked in an ‘unimaginable’ major data breach, further research has claimed the reality of the incident might not be as disastrous as first thought.Following significant speculation about the effects and origins of the breach, new findings from BleepingComputer suggest this “breach” may not be new, or even a breach - but instead just a compilation of existing leaked credentials.The inital datasets discovered by the researchers included hordes of personal information, with each of the 30 datasets containing between tens of millions, to over 3.5 billion data points - totaling 16 billion records. It now looks likely this was a series of datasets simply containing breached credentials assembled by a cybersecurity firm (or by criminals) which was then exposed online.Save up to 68% on identity theft protection for TechRadar readers! TechRadar editors praise Aura's upfront pricing and simplicity. Aura also includes a password manager, VPN, and antivirus to make its security solution an even more compelling deal.Preferred partner (What does this mean?)View DealInfostealers to blame“Despite the buzz, there's no evidence this compilation contains new or previously unseen data,” BleepingComputer confirms.The information from these datasets has likely been circulating for a while, and the layout of the breached information suggests that it was collected using infostealers - a type of malware that has become one of the most prolific threats to security teams and internet users alike.The information found in these datasets is formatted in such a way that points the finger firmly at infostealers, with credentials appearing in a one per line format (URL:username:password) all compiled in one ‘log’.One attack from an infostealer can exfiltrate all of the credentials stored on a browser, and the logs are then uploaded and usually sold on the dark web.Criminals will often upload samples of their stolen data as a ‘taster’ to prove the information is legitimate.Since these breaches can sometimes contain billions of records, these samples frequently hold tens of thousands of credentials - and this data breach is most likely a compilation of these tasters.What to do nextNew or not, leaked credentials pose a huge threat to those affected. If your information has been leaked, make sure to take a look at some identity theft protection software, as criminals can use your name, address, and details to take out credit cards or loans in your name.HaveIBeenPwned? is probably the best resource only to check if your details have been affected, offering a run-down of every big cyber incident of the past few years.As a business, enabling multi-factor authentication (MFA) and ensuring all staff are thoroughly trained on the dangers and signs of social engineering attacks is key. Using business password managers can also help ensure all user passwords are secure.And if you save passwords to a Google account, you can use Google's Password Checkup tool to see if any have been compromised, or sign up for one of the best password manager options we've rounded up to make sure your logins are protected."If this news frightens you, then your security program probably has some fundamental gaps,” argues James Shank, Director of Threat Operations at Expel.“Let this be the fuel you need to position yourself and your department for solving the problem systematically, rather than defending against the news du jour. There will always be another breach, with even more passwords, and emergency handling will continue if you don't have systematic defenses in place."You might also likeTake a look at our picks for the best endpoint protection tools aroundCheck out our choice for best antivirus softwareHackers claim 64 million leaked T-Mobile records, but it denies breach
-

Picture from static.independent.co.uk
Rank 53510 -

Picture from static.independent.co.uk
Rank 53511 -

Picture from ichef.bbci.co.uk
Rank 53512 -

Picture from static.independent.co.uk
Rank 53513 -

Picture from static.independent.co.uk
Rank 53514 -

Picture from image.cnbcfm.com
Rank 53515 -

Picture from image.cnbcfm.com
Rank 53516 -

Picture from static.independent.co.uk
Rank 53517 -
Picture from cdn.mos.cms.futurecdn.net
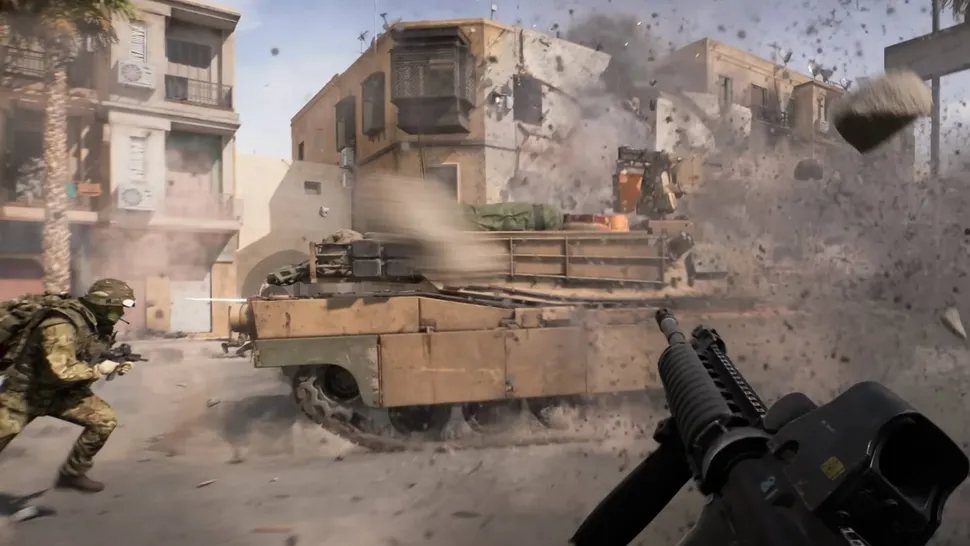
Rank 53518Footage purportedly showing the campaign of the next Battlefield game has leakedIt shows a firefight on a massive dam and some dramatic destructionThe video was allegedly found in the Battlefield Labs clientA reliable dataminer has leaked footage that purportedly shows part of a mission from the upcoming Battlefield 6 campaign.In an earnings call bac in February this year, we learned that the next Battlefield title will be released before March 31, 2026. Judging by this timeframe, a reveal is likely set for this summer, and testing is currently underway as part of the ongoing Battlefield Labs initiative.Described by publisher Electronic Arts (EA) as the “most ambitious community development collaboration ever,” the program allows select players to try parts of the next game and influence its development through feedback.As you might expect, this means that there has been a steady stream of leaks from those either playing these early builds or combing through them for data.The latest snippet of info comes from X / Twitter user 'temporyal', who has a strong track record as a leaker, and concerns the game's campaign. It takes the form of a short video file, purportedly found in the Battlefield Labs client.Here's a short clip from the Battlefield 6 singleplayer campaign in the latest BF Labs update.This work-in-progress footage shows the explosive finale of a mission to destroy a dam in Tajikistan. pic.twitter.com/n9ikBpUrmQJune 19, 2025In it, we see what appears to be a brief segment from the campaign in which the player boards a military truck in the shadow of a huge dam. Fire is exchanged briefly with some oncoming enemies before the scene reaches a climax as the dam dramatically explodes while the player flees in the back of the truck.It's the kind of showstopping destruction that you would want from a Battlefield and reminds me of some of the classic set-piece moments from older titles like Battlefield 4. Considering the fact that the latest entry in the series, Battlefield 2042, didn't even come with a single-player campaign component, this already seems like a massive improvement, and I can't wait to see more.The footage is obviously from a very early build of the game, though, as textures, lighting, and character animation are clearly unfinished. Still, it's easy to imagine how the scene might look in the finished product.Of course, you should bear in mind that there is no guarantee that anything shown in this leak will appear in the final game - or that it's even from the campaign in the first place. Games can change a lot throughout development, so we'll have to wait for some official details from EA for more concrete information.The leaker does go on to share some interesting titbits, though, including the fact that the campaign may comprise of a prologue and eight separate missions. These will allegedly take place in a range of global locations, including Egypt, Tajikistan, the US, and Gibraltar.You might also like...Call of Duty: Black Ops 7 is expected to launch just one year after its predecessor, and I’m worried it’ll repeat these three Modern Warfare 3 blundersI've replaced my Switch OLED with a Nintendo Switch 2 for two weeks now - here are the biggest improvements I’ve noticed in my time with the new consoleDon't buy a mobile controller without these six expert considerations
-
Picture from static.independent.co.uk
Rank 53519 -

Picture from static.independent.co.uk
Rank 53520 -

Picture from image.cnbcfm.com
Rank 53521 -
Picture from cdn.mos.cms.futurecdn.net
Rank 53522Believe it or not, there’s been a massive reduction in scam robocalls over the past few years. According to according to stats we gathered across millions of data points, scam calls are down roughly 75% since the Fall of 2021-- from more than 2 billion every month to roughly 500 million every month currently. That’s a massive decline, and it appears to be great news.So why does it feel like we’re in more danger, not less?Because we are.Total lossesIn 2021, the Federal Trade Commission reported the total losses from scams starting with a phone call were approximately $692 million, with a median loss of about $1,200 per victim. By 2024, those numbers had risen to $948 million, and a median loss of $1,500. Simple back-of-the-envelope math shows 25% of the calls led to 37% higher losses. In other words, the scammers have become roughly five to six times more efficient in their scamming ability from phone calls. They are making more money, with fewer calls and taking more from every victim.That’s not great.How do scammers do this? The answer is surprisingly simple: they became very efficient marketers.Scammers used to simply “dial for dollars,” calling one number after another, hoping to find vulnerable targets. That approach meant making calls to a lot of people who were irrelevant to the scam. Now, they are much smarter and more strategic.They often use curated lists of potential victims. If they want to run a banking scam, they can call everyone hoping to find customers of the bank, or scammers can obtain that bank’s customer list and launch a call campaign in which they impersonate that particular bank.And that’s exactly what they’re doing.Getting informationWhere do scammers get this information? They can simply go to the dark web, to find the results of data breaches that have exposed the personal details of millions. Breaches provide scammers with names, phone numbers, email addresses and even account details—everything they need to convincingly impersonate a trusted entity such as a bank. If scammers want to target an enterprise, they can easily get a list of employees, and call their personal cell phones.The sheer volume of data breaches in recent years means much of our personal information is essentially public. Phone numbers, e-mail addresses, Social Security numbers, credit card details, account numbers, medical records—the list goes on. With all that data in hand, it’s not hard to find the right targets with the right information to sound legitimate. After that, scammers can follow their script and pressure victims to transfer funds quickly or take some other problematic action.So what to do?Short answerThe short answer for individuals is that you must assume your identity is already out there. The genie is out of the bottle, and pretending otherwise only puts you at greater risk. The real question isn’t how to hide your identity-- it’s how to operate safely in a world where your personal and professional information is already exposed.Assume attackers know more than they should. They’re using publicly available data to impersonate company leaders, target employees, and launch social engineering campaigns that feel alarmingly real. Add in voice cloning and A.I.-generated deepfakes, and the risk multiplies quickly.That means you need to be skeptical, not scared. Focus less on chasing privacy and focus more on proactive protection. Assume that all unexpected inbound calls are potential fraud. Use technology like smart call blockers that can help filter out scams.And always validate the caller by hanging up and calling their institution on a number provided to you by a legitimate source. If they say they’re a bank, call the bank directly. If a caller says they’re from your company, make a call to a number provided by your employer.ConclusionWhile individuals must take those actions to protect themselves, business also play a major role in reducing the risks of scams. That should start with programs educating employees on how to recognize suspicious calls and impersonation tactics. Encourage employees to verify any unexpected requests, especially anything related to financial transactions and sensitive data. A quick phone call to a supervisor can prevent a costly mistake.The bad guys are only going to get better at their jobs. Your private information is only going to become more public. But if you stay vigilant and take the right precautions, you can protect yourself and avoid becoming the next victim.We list the best identity theft protection.This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
-

Picture from static.independent.co.uk
Rank 53523 -

Picture from static.independent.co.uk
Rank 53524 -

Picture from static.independent.co.uk
Rank 53525 -

Picture from static.independent.co.uk
Rank 53526 -

Picture from static.independent.co.uk
Rank 53527 -

Picture from static.independent.co.uk
Rank 53528 -
Picture from assets3.cbsnewsstatic.com
Rank 53529 -

Picture from static.independent.co.uk
Rank 53530 -

Picture from static.independent.co.uk
Rank 53531 -

Picture from static.independent.co.uk
Rank 53532 -

Picture from static.independent.co.uk
Rank 53533 -

Picture from static.independent.co.uk
Rank 53534 -

Picture from static.independent.co.uk
Rank 53535 -
Picture from assets2.cbsnewsstatic.com
Rank 53536 -

Picture from image.cnbcfm.com
Rank 53537 -
Picture from cdn.mos.cms.futurecdn.net
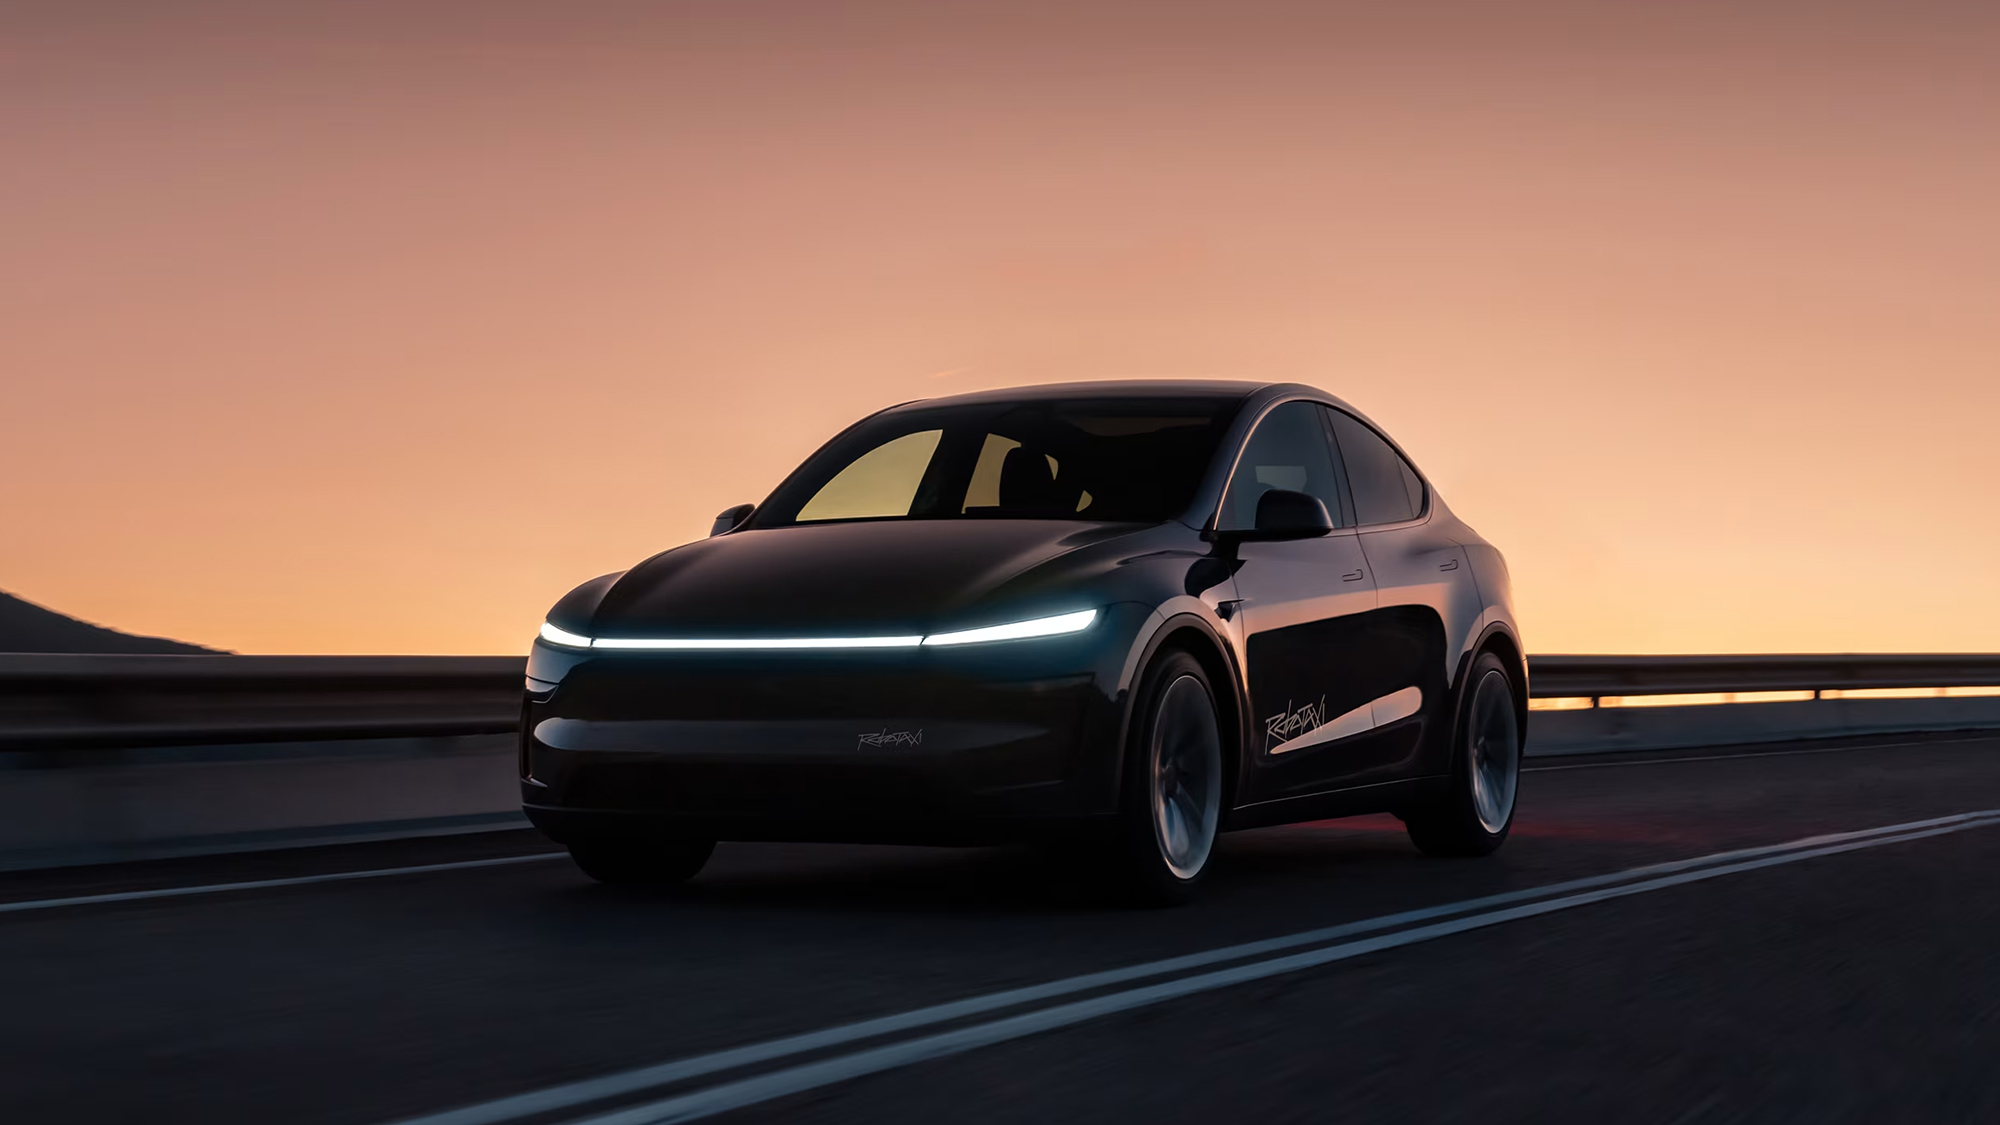
Rank 53538Tesla's Robotaxis are up and running in Texas, AustinMost online reactions have been positive so farYou can only get rides with special invites for nowIt's been quite a wait, but the Tesla robotaxi service has now launched in limited form, ferrying its first passengers around Austin, Texas with fully automated self-driving technology and no human cab drivers.The news was announced across various social media channels, including @Tesla_AI, and follows years of testing and teases from Tesla and its CEO Elon Musk. However, it's a very limited launch for now: you need to be invited to try out the service, and it only covers a specific part of Austin, a region that's been thoroughly mapped by Tesla's software.While there's no human driver, each robotaxi comes with a Tesla employee sitting in the passenger seat, ready to shut down the car if it gets into trouble.Rides are charged at a flat fee of $4.20 (around £3.15 / AU$6.60), with everything handled through the Tesla app. Musk has said the service will expand to other cities and reach the milestone of 1,000 vehicles in the coming months. So while it's good to see the service launch, I'll be shelving my Knightrider dreams for a little while yet.Third robo ride! pic.twitter.com/YOn7qe34kTJune 22, 2025Here is my experience in one of the first public nighttime @Tesla Robotaxi rides. It was smooth, comfortable and just as good as it is during the daytime. pic.twitter.com/7bDvVaWf3AJune 23, 2025There's also a brand new robotaxi page on the Tesla website, giving details of the service. Tesla is betting big on the robotaxi service as a future revenue stream, and there have even been hints that Tesla owners will eventually be able to rent out their cars as robotaxis, earning money while they're not otherwise being used.For now though, the service is a long way behind Waymo, which launched in San Francisco three years ago, and also operates in Austin, Los Angeles, and Phoenix. Waymo cabs don't have a member of staff present in the car, but the vehicles are all monitored remotely in case of any issues.Positive reactions – and some issues(Image credit: Tesla)Most of the robotaxi reactions arriving on social media have been very positive: the service apparently works very well, both during the day and at night, with a smooth passenger experience that reportedly beats what Waymo is offering.However, it's worth noting that most people who've been invited to use the robotaxi rides are Tesla owners, supporters, and investors. Check back through the social media accounts of people posting positively about their robotaxi rides, and you'll see there's plenty of pro-Tesla sentiment.Tesla Robotaxi drops us off at In-N-Out, deals with pedestrians crossing and the drive through line/traffic. Handled it perfectly. 🍔 pic.twitter.com/MgKiiFM2GsJune 22, 2025The best tech feels like magic because it’s so normal you don’t even notice it… until you do. Took a ride in a Tesla Robotaxi today. In this clip, it pulls aside on a narrow street with construction, making room for an oncoming car that illegally turns into our lane.The… pic.twitter.com/UZ9S13xGDOJune 23, 2025That's not a reason to dismiss these reactions, but it's important context. One of the clips circulating shows a robotaxi trying to swerve into the wrong lane, which it's prevented from doing. A clip posted to Reddit, meanwhile, shows issues with unnecessary braking, though it seems the robotaxi guardrails are working.There are now plenty of extended videos showing rides being taken in the robotaxis, with no obvious problems or issues. For the time being, rides can be hailed between the hours of 6am and midnight, and the Tesla app takes care of syncing data such as music playlists from passenger phones to the vehicles.If you want to read more positivity around the Tesla robotaxi, head to Elon Musk's feed on X – you'll see phrases such as "smooth as butter" and even "the beginning of post-driving civilization". There are a lot of technological and regulatory hurdles to overcome as Tesla's robotaxi service grows, but it is now at least operational.You might also likeTesla is secretly testing new versions of its next carsWaymo's robotaxis have hit impressive milestonesForget Tesla's robotaxis – this new VW ID Buzz is coming
-
Picture from ichef.bbci.co.uk
Rank 53539 -

Picture from ichef.bbci.co.uk
Rank 53540 -

Picture from ichef.bbci.co.uk
Rank 53541 -

Picture from static.independent.co.uk
Rank 53542 -

Picture from static.independent.co.uk
Rank 53543 -
Picture from cdn.mos.cms.futurecdn.net
Rank 53544Huge 38TB DDoS attack targeted a hosting providerCloudflare's DDoS protection kicked in and blocked the attackThis was the largest DDoS attack ever recordedDistributed-denial-of-service (DDoS) attacks usually use a network of compromised devices to bombard a server with an unusually large amount of data in order to render a service unusable.But Cloudflare says it recently blocked a monumental DDoS attack which attempted to dump almost 38TB worth of data in just 45 seconds - making it the largest such attack in history.For comparison, 38TB is the equivalent of downloading 9,350 full-length HD movies, or 9.35 million songs, or 7,480 hours of high-definition video.Cloudflare blocks mega-DDoSCloudflare said the attack resulted in 7.3 terabits per second (Tbps) of traffic hitting an average of 21,925 destination ports on an IP address belonging to an unnamed hosting provider.The attack used UDP packets as the main attack vector in order to ‘flood’ the IP address with illegitimate packets that the service will be unable to process, making up around 99.996% of the attack.The remaining 0.004% of the attack used a combination of reflection and amplification attacks which bounce data back onto the victim and amplify the attack, and flood attacks.Some of the additional attacks used obsolete diagnostic tools to ‘ping’ the IP address for an automatic response, which, when done en masse, overloads the network's ability to respond and amplifies the network’s traffic.The DDoS attack originated from 161 countries, with just under half of the traffic coming from IP addresses based in Brazil and Vietnam.Cloudflare said another third of the traffic was traced back to Taiwan, China, Indonesia, Ukraine, Ecuador, Thailand, the United States, and Saudi Arabia.For the uninitiated, this may make the attack sound like a huge coordinated effort by a highly organized group that span the globe, but in reality the majority of the devices used are compromised internet connected devices that have been infected with malware, turning the device into a ‘bot’.Hackers will use phishing, malicious downloads, or vulnerabilities to spread the malware, with the infected device continuing to operate as intended until called upon to take part in an attack.The attack peaked at 45,097 unique source IP addresses per second, with an average of 26,855 for the duration of the attack. To counter the attack, Cloudflare said it used the distributed nature of a DDoS attack to spread the traffic load across data centers close to where the traffic was originating from.Cloudflare’s DDoS detection and mitigation systems also detect suspicious packets and ‘fingerprints’ them, allowing the system to identify similarities in attack packets and mitigate them without impacting legitimate traffic.You might also likeThe best antivirus software can keep your devices protectedSurf the web at speed with the best browserDDoS attacks in 2025 have already surpassed the 2024 total
-
Picture from ichef.bbci.co.uk
Rank 53545 -

Picture from ichef.bbci.co.uk
Rank 53546 -

Picture from static.independent.co.uk
Rank 53547 -

Picture from static.independent.co.uk
Rank 53548 -

Picture from image.cnbcfm.com
Rank 53549 -
Picture from ichef.bbci.co.uk
Rank 53550